1
 →
Find vulnerabilities, misconfigurations, secrets, SBOM in containers, Kubernetes, code repositories, clouds and more
aquasecurity/trivy is an open-source project on GitHub, mainly written in Go. Find vulnerabilities, misconfigurations, secrets, SBOM in containers, Kubernetes, code repositories, clouds and more It currently holds 38,195 stars and 724 forks with 254 open issues, and was last pushed on 2026-10-02 (repository created 2019-04-11).
Git Homed tracks it on the Today's Trending board, currently at rank #98 with 24 new stars today.
[![GitHub Release][release-img]][release] [![Test][test-img]][test] [![Go Report Card][go-report-img]][go-report] [![License: Apache-2.0][license-img]][license] [![GitHub Downloads][github-downloads-img]][release] ![Docker Pulls][docker-pulls]
[📖 Documentation][docs]
Trivy ([pronunciation][pronunciation]) is a comprehensive and versatile security scanner. Trivy has scanners that look for security issues, and targets where it can find those issues.
Targets (what Trivy can scan):
To learn more, go to the [Trivy homepage][homepage] for feature highlights, or to the [Documentation site][docs] for detailed information.
Trivy is available in most common distribution channels. The full list of installation options is available in the [Installation] page. Here are a few popular examples:
brew install trivydocker run aquasec/trivyPlease be aware: canary builds might have critical bugs, so they are not recommended for use in production.
trivy [--scanners ]
Examples:
trivy image python:3.4-alpine
https://github.com/user-attachments/assets/af1c11e7-d9c5-48af-8e05-cb34dfd6352a
trivy fs --scanners vuln,secret,misconfig myproject/
https://github.com/user-attachments/assets/6b3894b7-77c5-4ffc-ac94-ffe6648a30dc
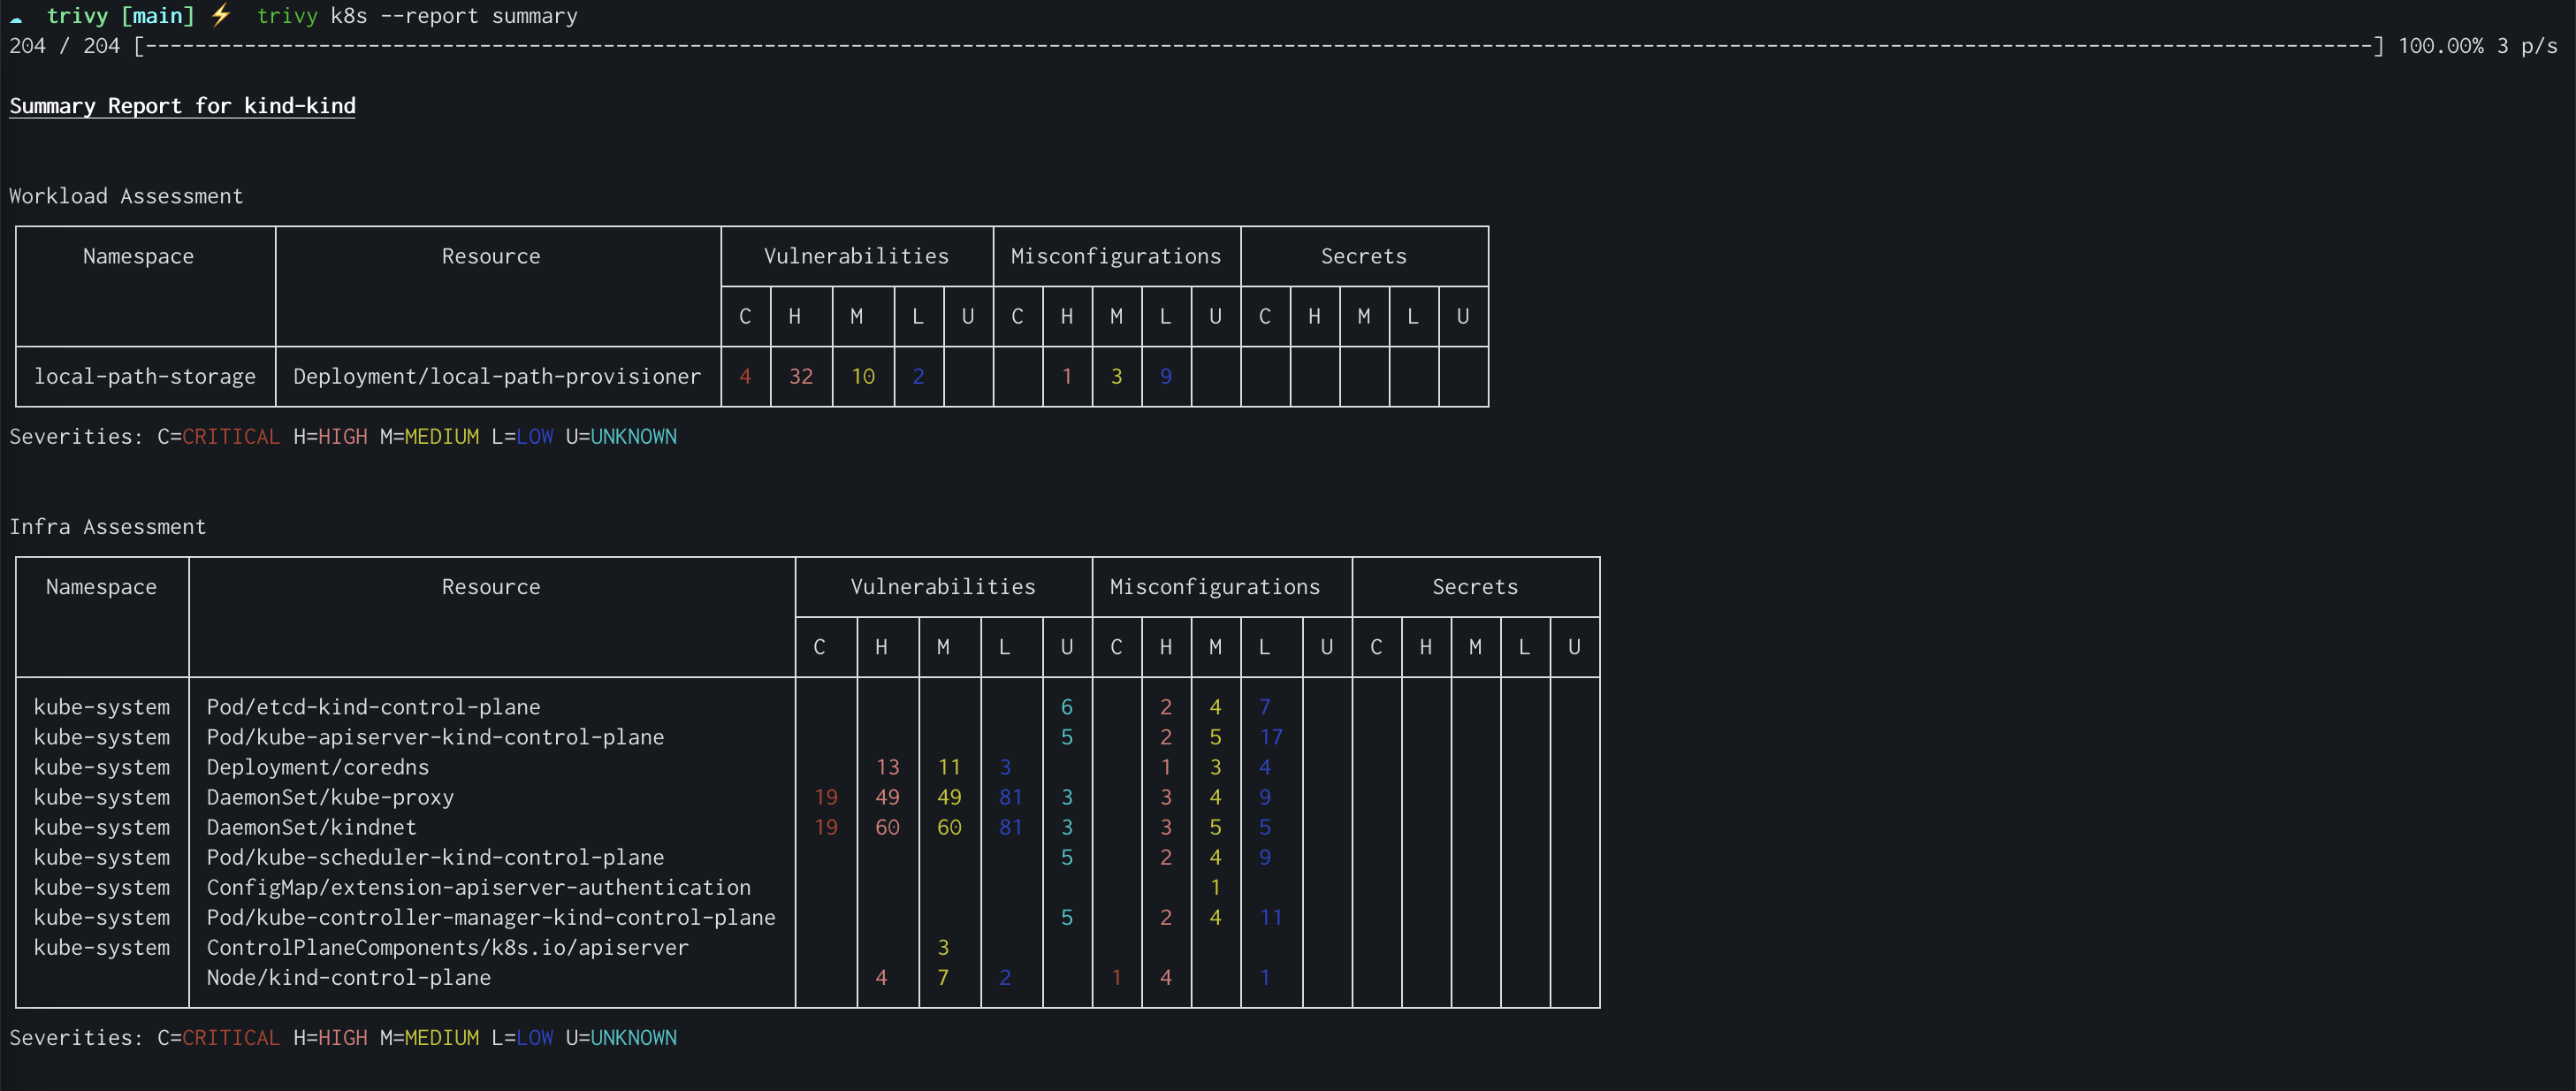
trivy k8s --report summary cluster
tri is pronounced like trigger, vy is pronounced like envy.
If you liked Trivy, you will love Aqua which builds on top of Trivy to provide even more enhanced capabilities for a complete security management offering. You can find a high level comparison table specific to Trivy users here. In addition check out the website for more information about our products and services. If you'd like to contact Aqua or request a demo, please use this form:
Trivy is an [Aqua Security][aquasec] open source project. Learn about our open source work and portfolio [here][oss]. Contact us about any matter by opening a GitHub Discussion [here][discussions]
Please ensure to abide by our [Code of Conduct][code-of-conduct] during all interactions.
[test]: https://github.com/aquasecurity/trivy/actions/workflows/test.yaml [test-img]: https://github.com/aquasecurity/trivy/actions/workflows/test.yaml/badge.svg [go-report]: https://goreportcard.com/report/github.com/aquasecurity/trivy [go-report-img]: https://goreportcard.com/badge/github.com/aquasecurity/trivy [release]: https://github.com/aquasecurity/trivy/releases [release-img]: https://img.shields.io/github/release/aquasecurity/trivy.svg?logo=github [github-downloads-img]: https://img.shields.io/github/downloads/aquasecurity/trivy/total?logo=github [docker-pulls]: https://img.shields.io/docker/pulls/aquasec/trivy?logo=docker&label=docker%20pulls%20%2F%20trivy [license]: https://github.com/aquasecurity/trivy/blob/main/LICENSE [license-img]: https://img.shields.io/badge/License-Apache%202.0-blue.svg [homepage]: https://trivy.dev [docs]: https://trivy.dev/docs/latest/ [pronunciation]: #how-to-pronounce-the-name-trivy [code-of-conduct]: https://github.com/aquasecurity/community/blob/main/CODE_OF_CONDUCT.md
[Installation]:https://trivy.dev/docs/latest/getting-started/installation/ [Ecosystem]: https://trivy.dev/docs/latest/ecosystem/ [Scanning Coverage]: https://trivy.dev/docs/latest/coverage/
[alpine]: https://ariadne.space/2021/06/08/the-vulnerability-remediation-lifecycle-of-alpine-containers/ [rego]: https://www.openpolicyagent.org/docs/latest/#rego [sigstore]: https://www.sigstore.dev/
[aquasec]: https://aquasec.com [oss]: https://www.aquasec.com/products/open-source-projects/ [discussions]: https://github.com/aquasecurity/trivy/discussions
→ →
 →
 →
 →
 →
 →
 →