1
 →
A Claude Code skill bundle for bug hunting and external red-team work - 82 skills, 15 slash commands, 681 disclosed-report patterns curated across 24 core vulnerability classes
elementalsouls/Claude-BugHunter is an open-source project on GitHub, mainly written in Python. A Claude Code skill bundle for bug hunting and external red-team work - 82 skills, 15 slash commands It currently holds 5,883 stars and 902 forks with 5 open issues, and was last pushed on 2026-11-14 (repository created 2026-05-05).
Git Homed tracks it on the Today's Trending board, currently at rank #3 with 1,094 new stars today.
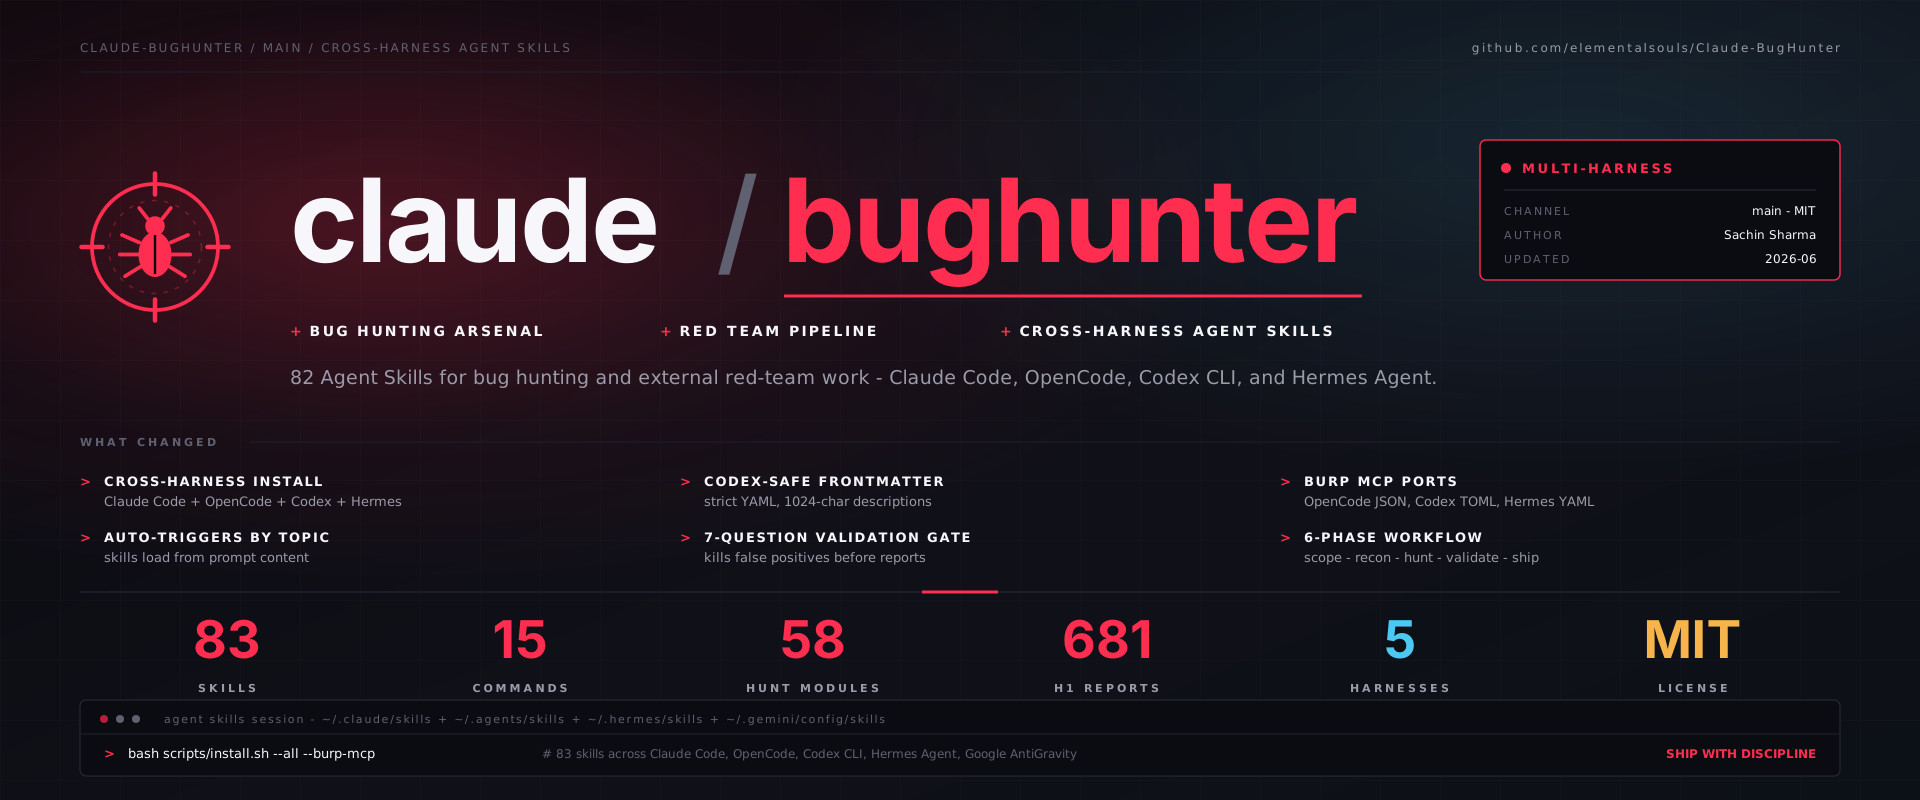
A self-contained Claude skill bundle for bug hunting and external red-team work · 83 skills · 15 slash commands · 681 disclosed-report patterns (433 now individually cited & auditable) across 24 core vulnerability classes · enterprise identity + infrastructure attack matrices · engagement-folder scaffolding · Burp MCP integration · battle-tested across authorized red-team and bug-hunting engagements, plus public training platforms (DVWA, OWASP Juice Shop, Hacker101, testphp.vulnweb.com).
Built by Sachin Sharma — Bug Hunting & GenAI Security Research.
SPONSORED BY

---
claude-bughunter is a drop-in skill bundle for the Claude Code skills system. Install once and Claude Code stops being a chatbot and starts behaving like a senior bug-hunting researcher or red-team operator: it knows the techniques, the chain templates, the VRT mappings, the platform CVE chains, and the hygiene — and it stays in scope.
Four layers stack:
bb-methodology + redteam-mindset: the 5-phase non-linear workflow, critical-thinking framework, and red-team operator discipline.hunt-* skills curated from 681 disclosed HackerOne reports: per-class detection patterns, payloads, bypass tables, and chain templates.triage-validation + reporting + evidence-hygiene: the 7-Question Gate, VRT-aware severity, OOS rebuttals, PII redaction, and red-team deliverables.---
Option A — install as a Claude Code plugin (recommended). From inside Claude Code:
/plugin marketplace add elementalsouls/Claude-BugHunter
/plugin install claude-bughunter@elementalsouls
All 83 skills + 15 commands load namespaced under claude-bughunter: and update when you bump the plugin version — no files copied into ~/.claude/.
Option B — copy install (no plugin system / pin to a clone):
git clone https://github.com/elementalsouls/Claude-BugHunter.git
cd Claude-BugHunter
# macOS / Linux
bash scripts/install.sh
Windows (PowerShell)
pwsh ./scripts/install.ps1
Both copy the skills + commands into ~/.claude/ (macOS/Linux) or %USERPROFILE%\.claude\ (Windows) and wire the hunt engagement scaffolder.
What each install path gives you:
| Path | 83 skills + 15 slash commands | cbh CLI | hunt scaffolder |
|---|---|---|---|
| A — plugin | ✅ namespaced under claude-bughunter: | ➕ separate pipx install | ❌ clone-only |
| B — copy install | ✅ copied into ~/.claude/ | ✅ from the clone | ✅ from the clone |
The plugin is the fastest path to the skills + slash commands. The terminal-native
cbh runner installs standalone — pipx install git+https://github.com/elementalsouls/Claude-BugHunter
— so plugin users can add it without a full clone (see cbh CLI).
The hunt engagement scaffolder ships with the clone (Option B).
That's it. Open Claude Code and describe what you're testing in plain English — the right skill loads automatically, no invocation by name:
> Testing acme.com — an in-scope HackerOne target. Run recon and rank the surface.
⟳ loading skills: web2-recon, offensive-osint, bb-methodology …
    → subdomain enum (subfinder + crt.sh) … 47 hosts
    → live hosts (httpx) … 12 · tech fingerprint … 6 distinct stacks
    → ranked surface: api.acme.com (GraphQL, introspection ON)  ← start here
                      auth.acme.com (OAuth, SSO)               ← hunt-oauth
Next: want me to probe the GraphQL introspection + OAuth redirect_uri?
→ Full Installation guide · Usage guide · searchable skill catalog.
The block above is an illustrative transcript. To record a real demo of your own session: asciinema rec demo.cast → upload to asciinema.org and drop the badge here.
---
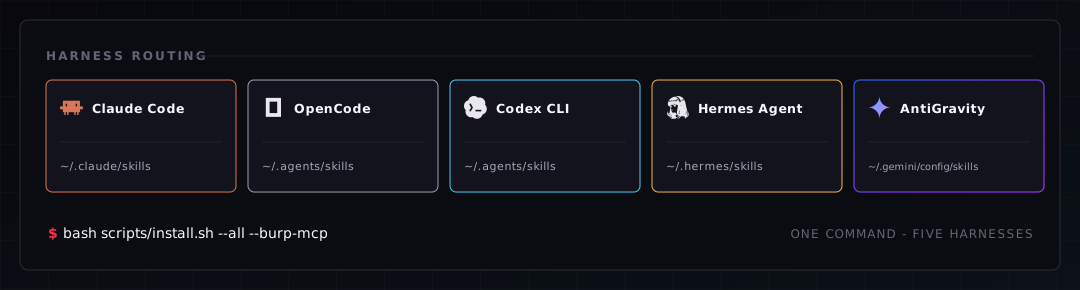
The skills are plain Agent Skills — the same SKILL.md format that Claude Code · OpenCode · OpenAI Codex CLI · Hermes Agent · Google AntiGravity all load. One command installs them everywhere:
# macOS / Linux
bash scripts/install.sh --all --burp-mcp
Windows (PowerShell)
pwsh ./scripts/install.ps1 -All -BurpMcp
| Harness | Target Skill Directory | Flag |
|---|---|---|
| Claude Code (baseline) | ~/.claude/skills/ | (default) |
| OpenCode | reads ~/.claude/skills/ & ~/.agents/skills/ | (default) / --agents |
| OpenAI Codex CLI | ~/.agents/skills/ | --agents |
| Hermes Agent | ~/.hermes/skills/ | --hermes |
| Google AntiGravity | ~/.gemini/config/skills/ | --antigravity |
--all (-All) detects installed harnesses and copies skills to each harness's path (~/.claude/skills, ~/.agents/skills, ~/.hermes/skills, ~/.gemini/config/skills); --burp-mcp (-BurpMcp) wires the Burp MCP server into each. The full knowledge layer ports to all five — the slash commands and /hunt engine stay Claude-Code-only by design.
---
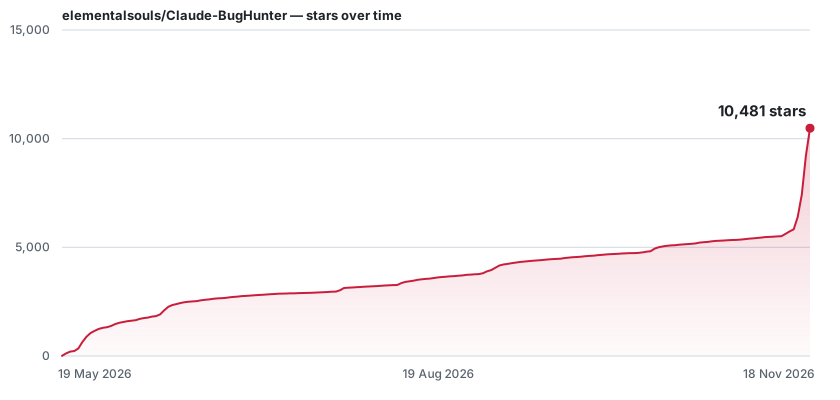
Chart is self-hosted — regenerate with python3 scripts/gen_star_history.py (needs gh auth login).
Refreshes automatically each day via .github/workflows/star-history.yml.
---
This bundle covers the external attack surface — anything reachable from the internet without first compromising an internal endpoint.
---
83 skills, auto-loaded by topic — no invocation by name. Coverage across the external attack surface:
| Category | # | Examples | |---|---|---| | Hunt — web app vuln classes | 58 | XSS, SQLi, SSRF, IDOR, LFI, SSTI, XXE, CSRF, CORS, open-redirect, SharePoint, ASP.NET/NTLM | | Enterprise platform attack ★ | 10 | M365/Entra, Okta, cloud-IAM-deep, vCenter, enterprise VPN, APK/iOS red-team pipelines, supply-chain recon | | Reporting & validation | 6 | triage-validation, evidence-hygiene, report-writing, bugcrowd-reporting | | Recon & OSINT | 5 | web2-recon, offensive-osint, osint-methodology, recon-scope-triage | | Methodology & mindset | 4 | bb-methodology, bug-bounty, redteam-mindset, bb-local-toolkit |
Full searchable catalog → docs/skills.md. Also ships 15 slash commands (/hunt, /recon, /report, …) and a deterministic engagement engine (engine/) that maps a target's attack surface and routes each finding to the skill that handles it.
---
A 6-phase, non-linear workflow — recon → map & rank → hunt → validate → report — with scope enforced in code and a 7-Question Gate before anything is submitted. Two ways to drive it:
/hunt scaffold + cbh CLI — engagement-folder structure, state, and orchestration.cbh CLI
---
These skills are intended for assets you own or have written authorization to assess (bug-bounty in-scope assets, pentest engagement letters, CTF challenges, your own infrastructure).
The skills include validation gates that auto-trigger when you point Claude at unverified third-party targets — triage-validation's 7-Question Gate explicitly asks whether the asset is in scope (Q3) and on the program's accepted-impact list (Q2). The bugcrowd-reporting skill includes researcher-side hygiene (Bugcrowdninja alias, account-state restoration, friendly-tester posture) that signals legitimate authorized testing to the target's fraud team.
The bundle explicitly excludes: weaponizing 0-days against unauthorized targets, post-exploitation tooling, malware development, mass-targeting infrastructure. See SECURITY.md for the full posture.
Heads-up — Anthropic runtime cyber safeguards. Anthropic's models apply real-time safeguards that block "vulnerability exploitation or offensive security tooling development" by default — so even authorized, in-scope work can hit a refusal that isn't this bundle's doing. If you do authorized offensive security (pentest / bug bounty / red team), enroll in Anthropic's free, application-based Cyber Verification Program (CVP) to get safeguards adjusted for legitimate dual-use work. (Mass data exfiltration and ransomware development stay prohibited and are not adjustable.) Details: Anthropic — real-time cyber safeguards.
Separate from refusals, and easy to miss. On Opus 5, a narrow set of higher-risk cyber requests — Anthropic names exploit generation, binary-based vulnerability scanning and penetration testing — fall back to Opus 4.8 rather than being refused. You get a notice and the response is labelled with the model that answered, but in a long agentic run that is easy to scroll past, so it can look like Opus 5 quietly got worse. See why Claude switched models.
What to do depends on what you are actually doing:
| Situation | What helps | |---|---| | Auditing your own code — reviewing a repo you own for defects | Say so. "Defensive review of my own repo", "check this against the OWASP Top 10", "secure refactor to remediate" describe the work accurately and read as remediation. This is not a workaround; the work genuinely is defensive. | | Authorized offensive work — live engagement, PoC for a bounty submission | This is what the bundle is for, and the supported route is CVP. Do not reword an offensive engagement to look defensive to get past a classifier — enroll instead. | | You just want the switching off | Settings → Capabilities disables automatic model switching. |
/hunt states the engagement frame (authorized, scope-bounded, remediable finding) on its first turn
for exactly this reason — engagement context belongs in the session explicitly, not implied.
---
| Doc | Contents |
|---|---|
| README.md | This file — overview, quickstart, scope, skill summary |
| INSTALL.md | Full setup with Burp MCP integration and optional skill regenerator |
| USAGE.md | Workflow walkthrough · decision tree · worked engagement example |
| docs/architecture.md | 6-phase architecture · skill-to-phase mapping · engagement composition |
| docs/cbh-cli.md | cbh CLI — native runner orchestrating recon + classify + triage + report |
| docs/cve-coverage.md | CISA KEV coverage snapshot — refreshed weekly via the workflow template at docs/automation/cve-refresh.yml.template |
| docs/credits.md | Full attribution: 43 original skills + 8 vendored from upstream |
| CONTRIBUTING.md | PR guidelines · skill quality standards · scope |
| SECURITY.md | Authorized-use posture · responsible disclosure · what's excluded |
| LICENSE | MIT |
| NOTICE | Upstream-skills attribution · no-redistribution note |
| LICENSE-CONTENT | CC BY 4.0 (skill methodology, wordlists, docs) |
---
Most bug-hunting Claude setups are either too generic (one big "security" prompt) or too fragmented (you bookmark 30 disclosed reports and re-read them every engagement). Neither scales past the second target.
This bundle was built and validated through authorized engagements that exposed different capability gaps:
Bug-bounty engagement — surfaced four gaps a starter 3-skill stack could not close:
1. No hypothesis discipline — drafts written before validation → wasted hours, hurt validity ratio 2. No per-program reporting tactics — VRT defaults auto-downgraded P3-worthy findings to P4 3. No engagement coordination — findings, evidence, and submission IDs scattered across folders 4. No evidence hygiene — screenshots leaked cookies and victim PII
External red-team engagement — exposed five additional gaps that bug-bounty defaults made worse:
1. Conservative defaults retracted real findings — WAPT mindset stopped tests early on defended targets where red-team continuation would have surfaced bypass chains → redteam-mindset
2. No mid-engagement situational awareness — client SOC patched confirmed SQLi within 30 min; external attacker locked 14 accounts during a live test session — both invisible without explicit detection methodology → mid-engagement-ir-detection
3. No enterprise-platform attack chains — M365 + Entra ID, on-prem SharePoint, Cisco SSL VPN, vCenter, and 7 Android APKs all needed current 2024-2026 CVE knowledge and platform-specific tradecraft → m365-entra-attack, okta-attack, hunt-sharepoint, hunt-aspnet, hunt-ntlm-info, vmware-vcenter-attack, enterprise-vpn-attack, apk-redteam-pipeline
4. No client-facing deliverable format — bug-bounty report templates don't fit enterprise red-team where output is a 50KB+ MD + DOCX with embedded screenshots → redteam-report-template
5. No post-credential escalation model — when recon yielded credentials (AWS keys, JWTs, GCP JSON), it was unclear what they granted or how to escalate → cloud-iam-deep
The per-class hunt- skills address gap-zero ("what should I look for in webapps"*) — the original 24 codifying patterns from 681 disclosed HackerOne reports, with 20+ framework/surface skills added by the community v3 expansion — Claude knows the actual chain templates real triagers paid for, not abstract OWASP Top 10. The enterprise-platform and red-team-tradecraft layers address what bug-bounty alone cannot: external red-team engagements against monitored enterprise targets.
---
hunt-fintech-graphql shipped; hunt-healthcare-fhir, hunt-gov-compliance still openscope.md from program texthunt-* skills with newer disclosed reports (re-run public-skills-builder)citrix-netscaler-deep, f5-bigip-attack, ad-cs-attack (AD Certificate Services)
ApiSmart unifies leading LLM, image, and video models through one OpenAI-compatible API. Use one key to switch models, simplify billing, and improve reliability with automatic failover.
ThreatWatch360 is an AI-powered offensive-security platform: continuous Attack Surface Management, AI-assisted penetration testing, brand protection, dark-web monitoring, and Cyber Threat Intelligence in one platform. Validated findings with proof-of-concept and business-impact prioritization — signal over alert fatigue.
---
Operational tradecraft accumulated across bug-bounty engagements and authorized pentests, codified into Claude skills. Platform-agnostic — slot into any engagement workflow you already use, or none.
Author: ElementalSoul · GenAI Security Research
Sister project: Claude-OSINT — paired skills for the recon phase that this bundle picks up after. Its two recon skills (offensive-osint, osint-methodology) are canonically maintained here and re-exported there, so the two are byte-identical. Installing both is safe: each bundle's installer (install.sh on macOS/Linux, install.ps1 on Windows) records a manifest, the script skips re-copying an identical skill, and --uninstall keeps any skill the other bundle still owns — uninstalling one never breaks the other.
Vendored foundation: shuvonsec/claude-bug-bounty — methodology, validation, reporting, payload library (8 of 83 skills + 15 slash commands)
Generator tool used (not vendored): shuvonsec/public-skills-builder — used to scaffold per-class skills from H1 disclosed reports
Inspirations:
trailofbits/skills — skill-authoring disciplinetrilwu/secskills — subagent patternThis project is dual-licensed:
.py, .sh, and other source files are MIT; *.md documentation, wordlists, regex catalogs, and rubrics are CC BY 4.0.
Reuse the content freely — including commercially — as long as you credit
Sachin Sharma / Claude-BugHunter** and link back to this repository. SeeNOTICE for upstream-skills attribution.
---
"Give Claude the right skill and it stops being a chatbot. It becomes an operator."
→ →
 →
 →
 →
 →
 →
 →