Autumn-27/ScopeSentry
ScopeSentry-Cyberspace mapping, subdomain enumeration, port scanning, sensitive information discovery, vulnerability scanning, distributed nodes
About Autumn-27/ScopeSentry
Autumn-27/ScopeSentry is an open-source project on GitHub, mainly written in Go. ScopeSentry-Cyberspace mapping, subdomain enumeration, port scanning, sensitive information discovery, vulnerability scanning, distributed nodes It currently holds 1,763 stars and 335 forks with 89 open issues, and was last pushed on 2026-08-23 (repository created 2024-02-27).
Project Overview
Git Homed tracks it on the Today's Trending board, currently at rank #97 with 28 new stars today.
GitHub Repository Details
README
English | 中文
Introduction
Scope Sentry is a tool with functions such as asset mapping, subdomain enumeration, information leakage detection, vulnerability scanning, directory scanning, subdomain takeover, crawler, and page monitoring. By building multiple nodes, users can freely choose nodes to run scanning tasks. When new vulnerabilities emerge, it can quickly check whether the concerned assets have related components.Distributed Implementation Reference Articles: https://mp.weixin.qq.com/s/xfgRxUjljoQ8KzacblktxA
Server Recommendation: lightnode
Discord:
Language
Server:python - FastApiScan:go
Front-end:vue - vue-element-plus-admin
Website
- Official Website: https://www.scope-sentry.top
- Github: https://github.com/Autumn-27/ScopeSentry
- Scanner source code: https://github.com/Autumn-27/ScopeSentry-Scan
- UI source code: https://github.com/Autumn-27/ScopeSentry-UI
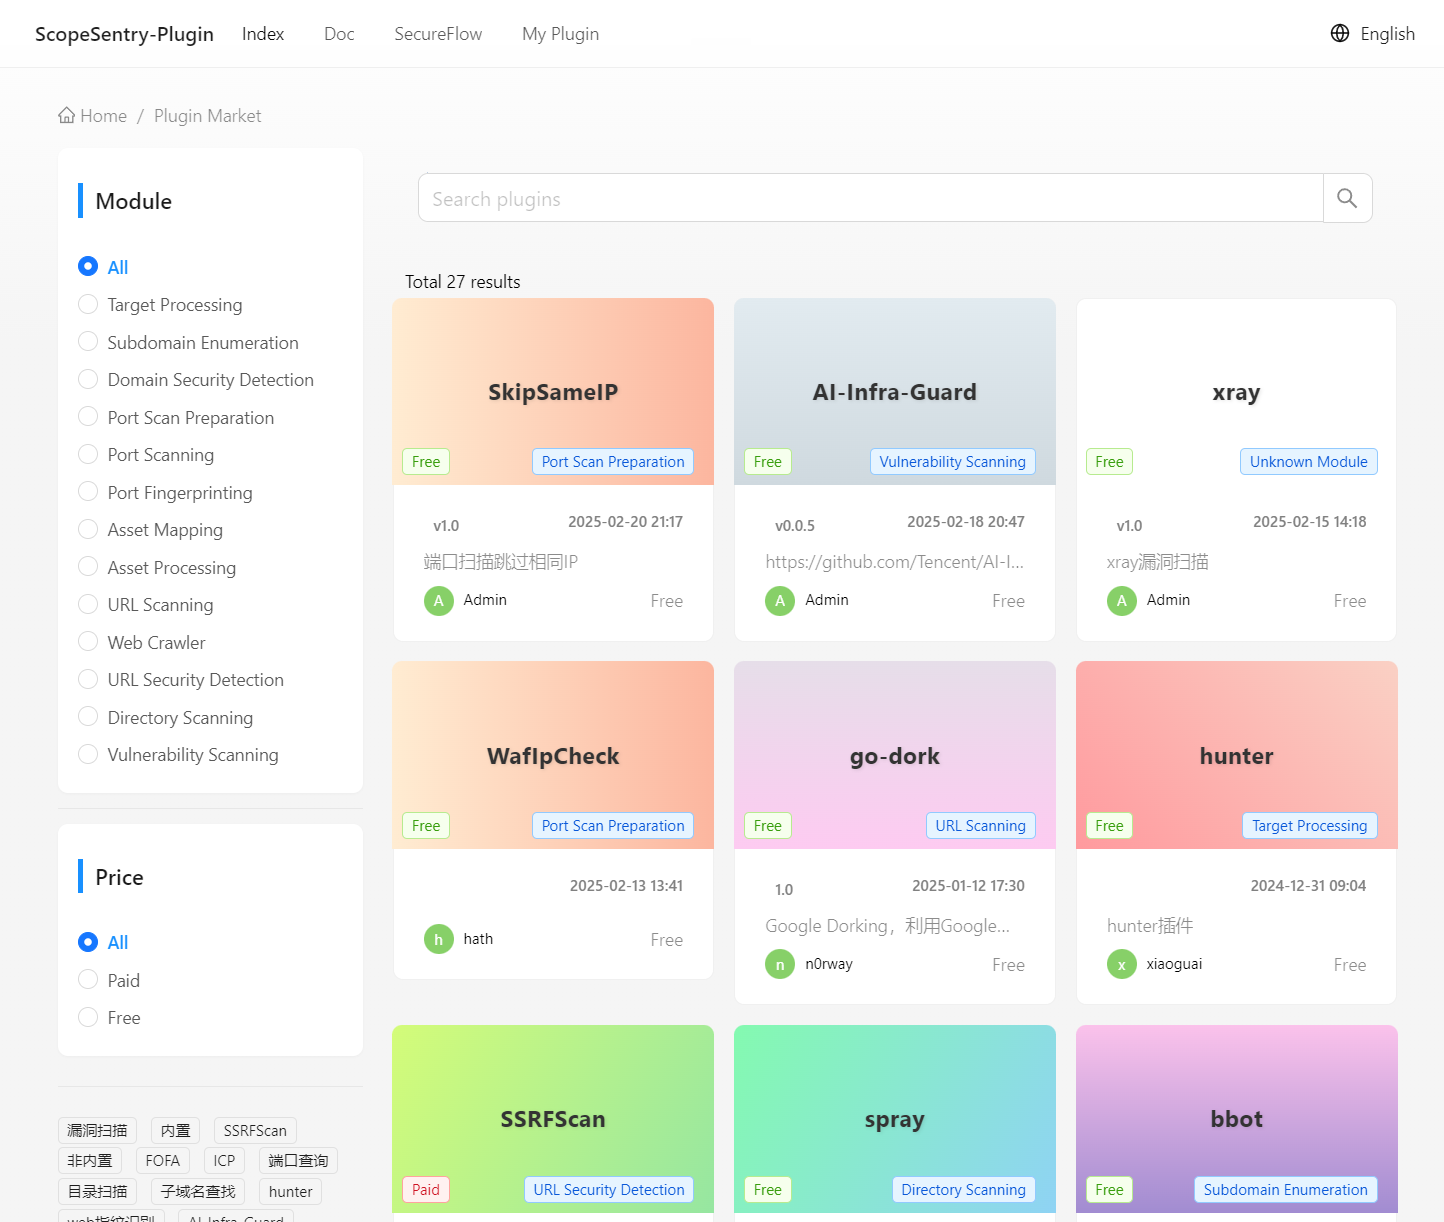
- Plugin Market: Plugin Market
- Plugin Template:https://github.com/Autumn-27/ScopeSentry-Plugin-Template
Install
git clone https://github.com/Autumn-27/ScopeSentry.git
cd ScopeSentry
Change the MongoDB and Redis account passwords in the. env file.
docker-compose -f single-host-deployment.yml up -d
After running, there will be four containers: mongodb, redis, scope-sentry (server), and scopesentry-scan (scan). By default, there will be one scanning node.
View the initial user password and the secondary verification password of the plug-in
```docker logs scope-sentry
Add new nodes(Optional)
git clone https://github.com/Autumn-27/ScopeSentry-Scan.git
cd ScopeSentry-Scan/build
Edit the connection information for MongoDB and Redis in the .env file. NodeName is the node name, and each node name should be unique (if it is empty, it will be randomly generated, and you can change the name in the web interface).
docker-compose -f scan-docker-compose.yml up -d ```Plugin Flowchart
Current Features
- Plugin System (Add any tool through extension)
- Subdomain Enumeration
- Subdomain Takeover Detection
- Port Scanning
- Asset Identification
- Directory Scanning
- Vulnerability Scanning
- Sensitive Information Leakage Detection
- URL Extraction
- Crawler
- Page Monitoring
- Custom WEB Fingerprint
- POC Import
- Asset Grouping
- Multi-Node Scanning
- Webhook
To Do
- Weak Password Cracking
Installation
Communication
Discord:
Screenshots
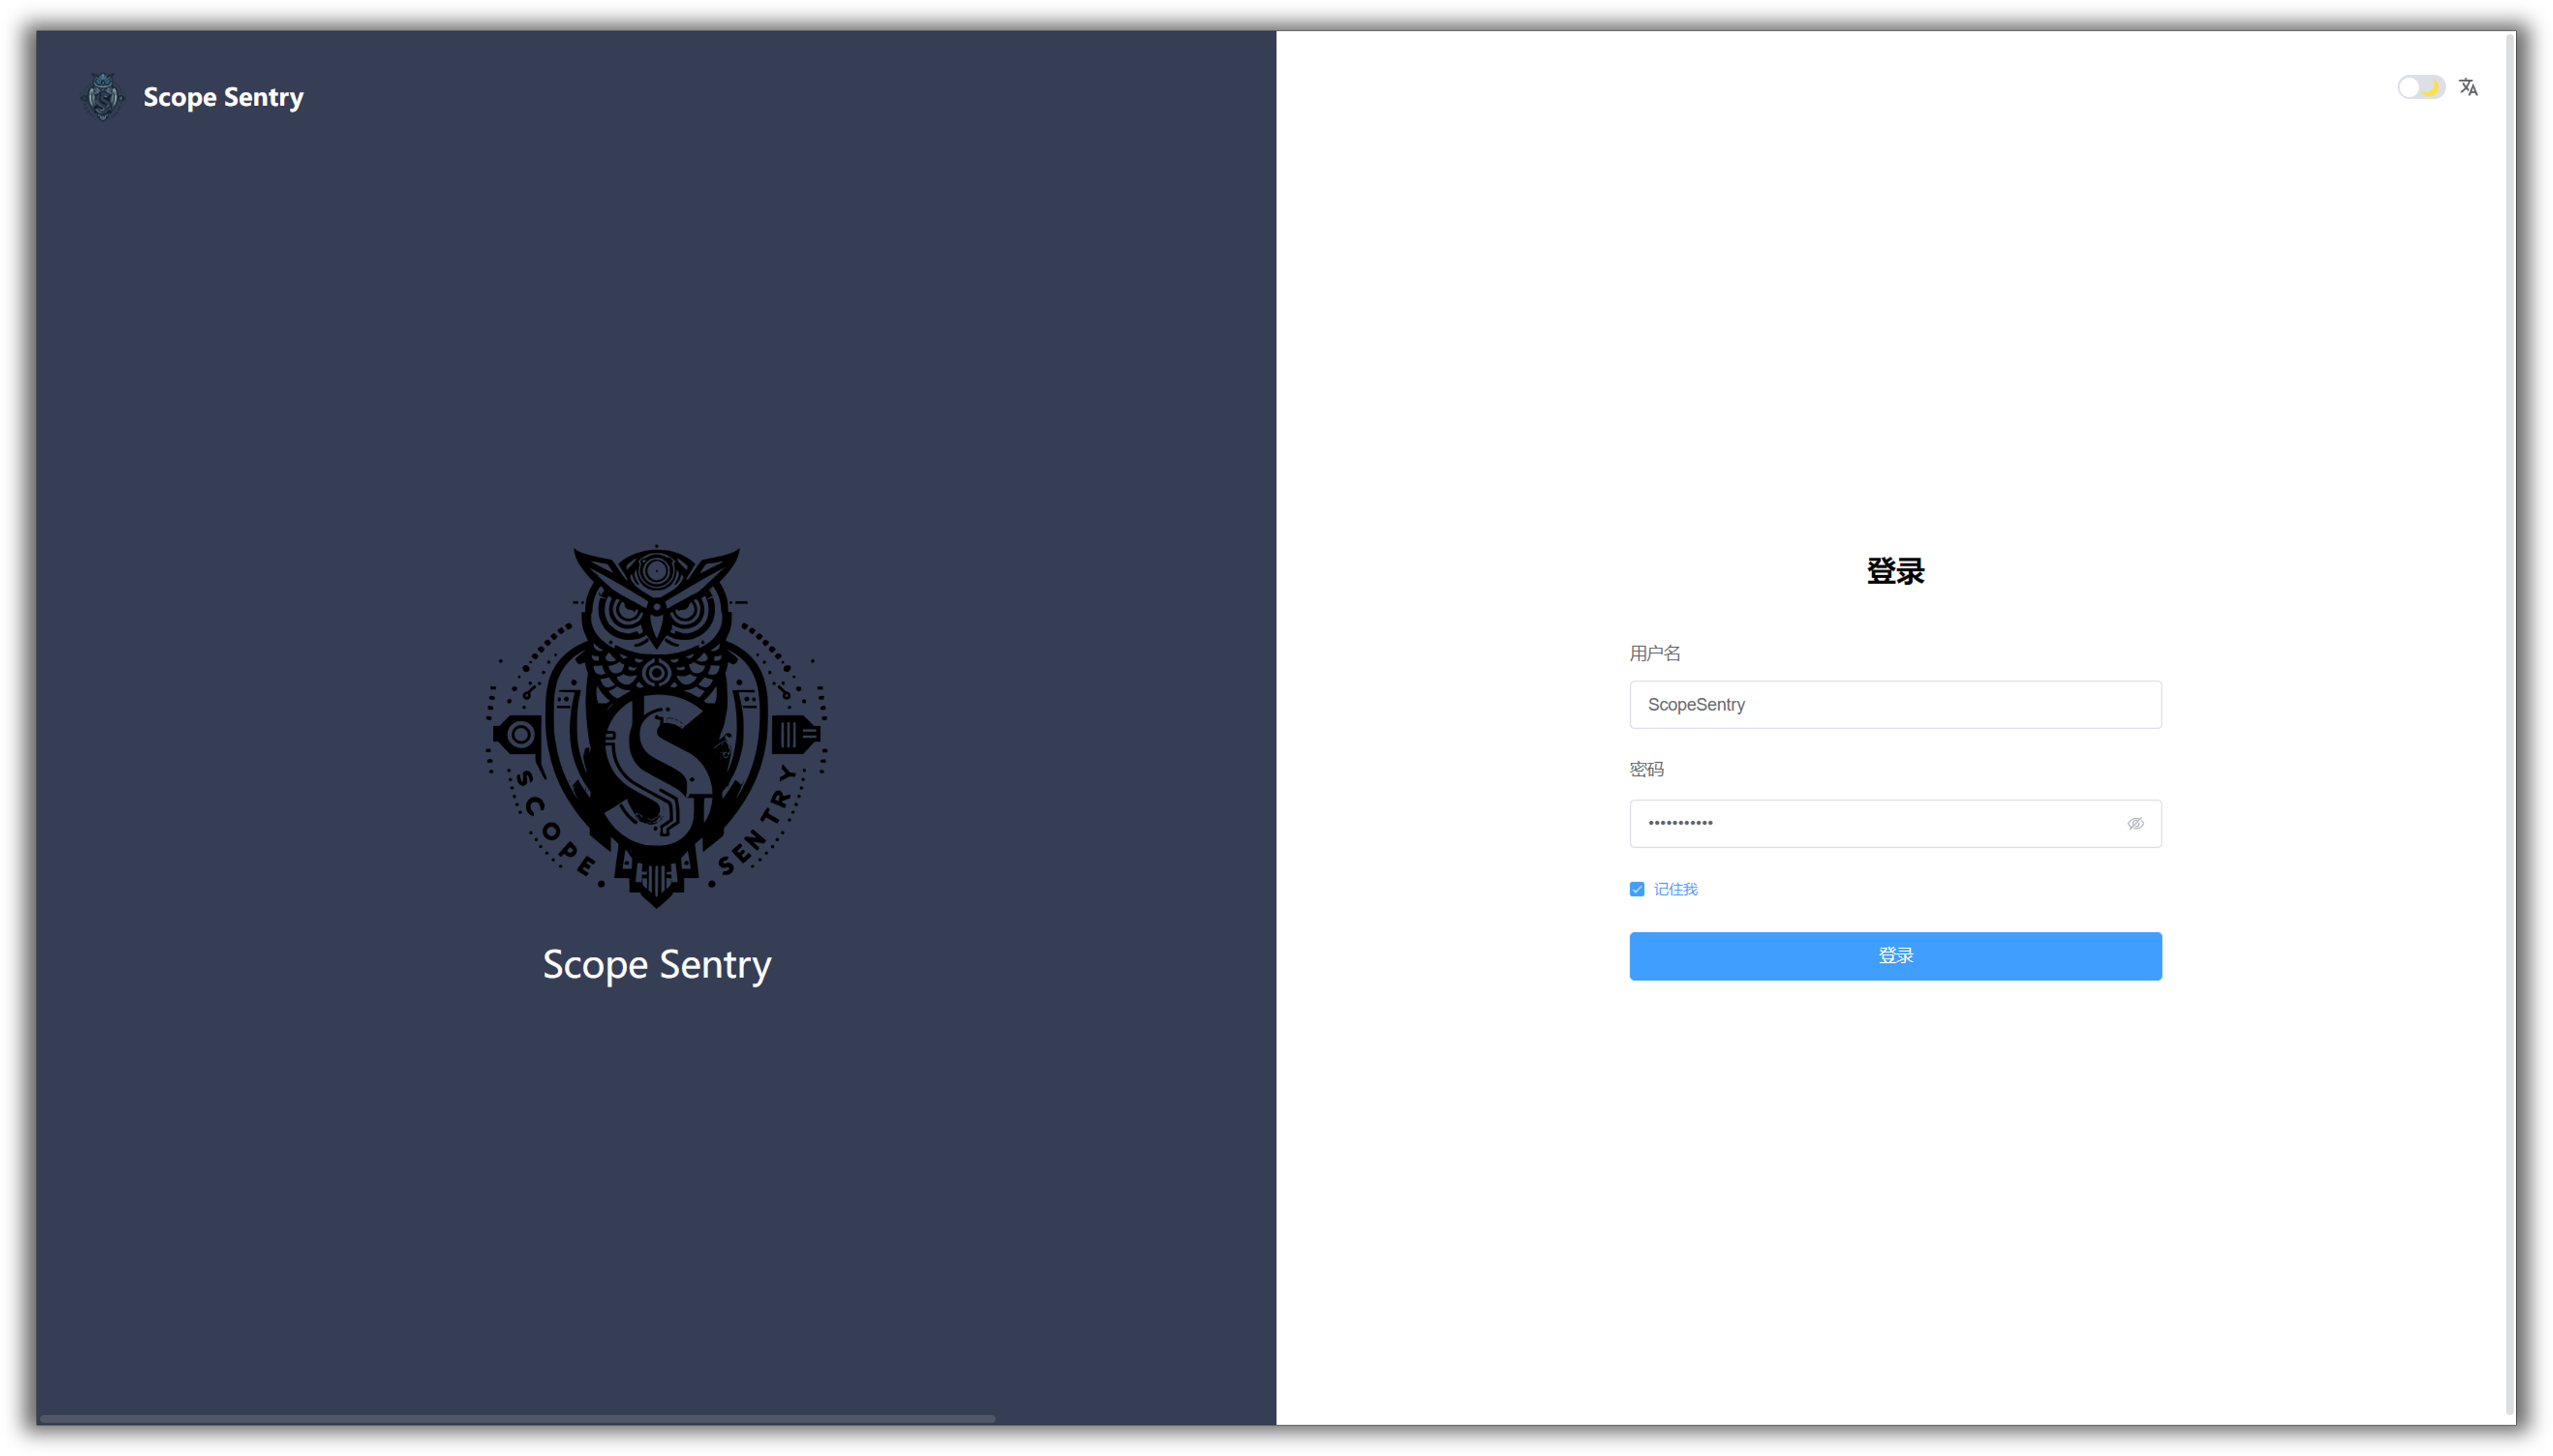
Login
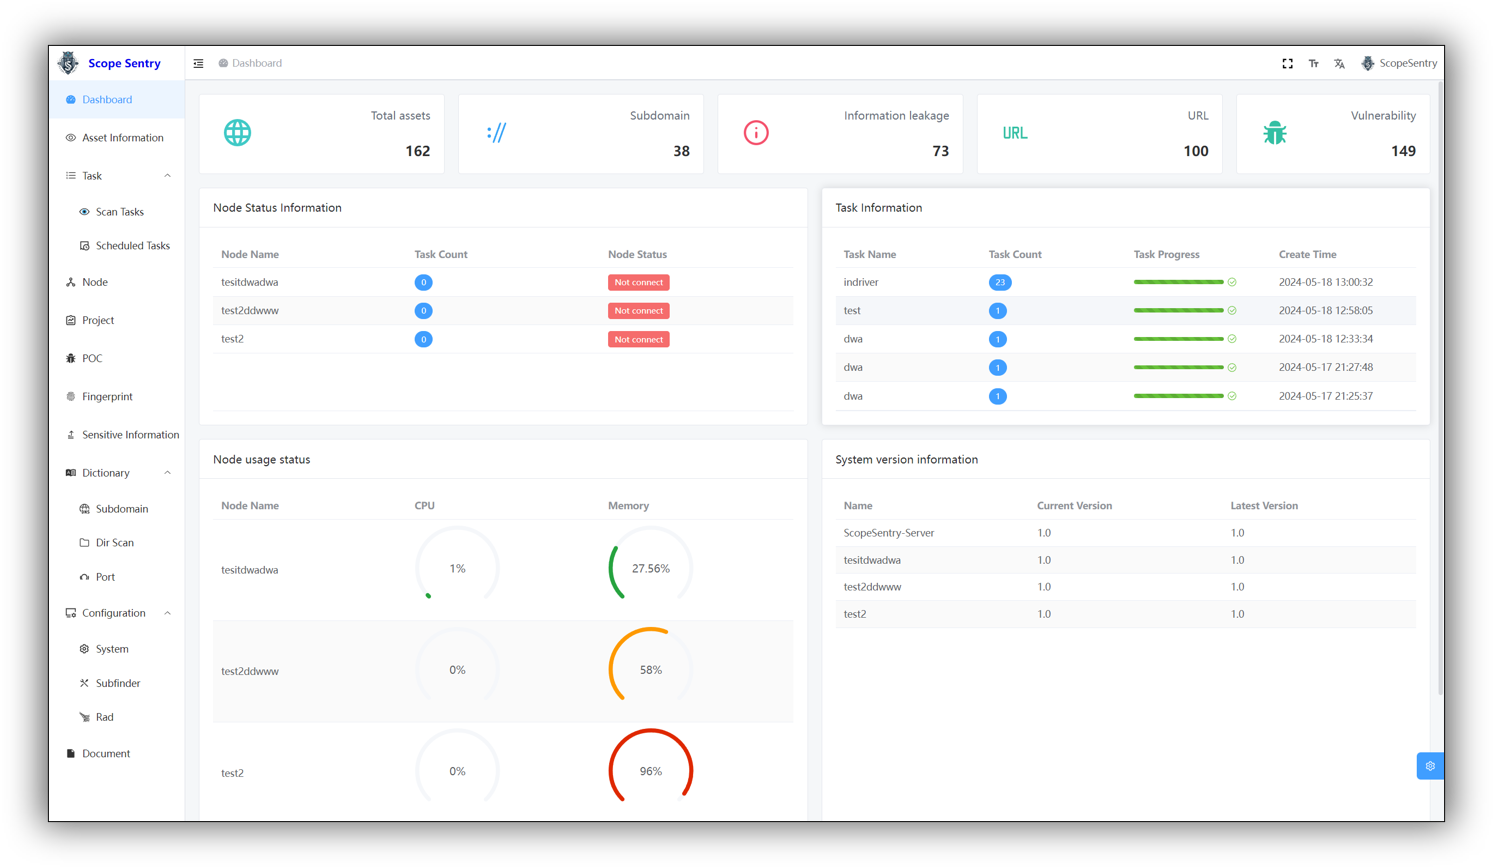
Homepage Dashboard
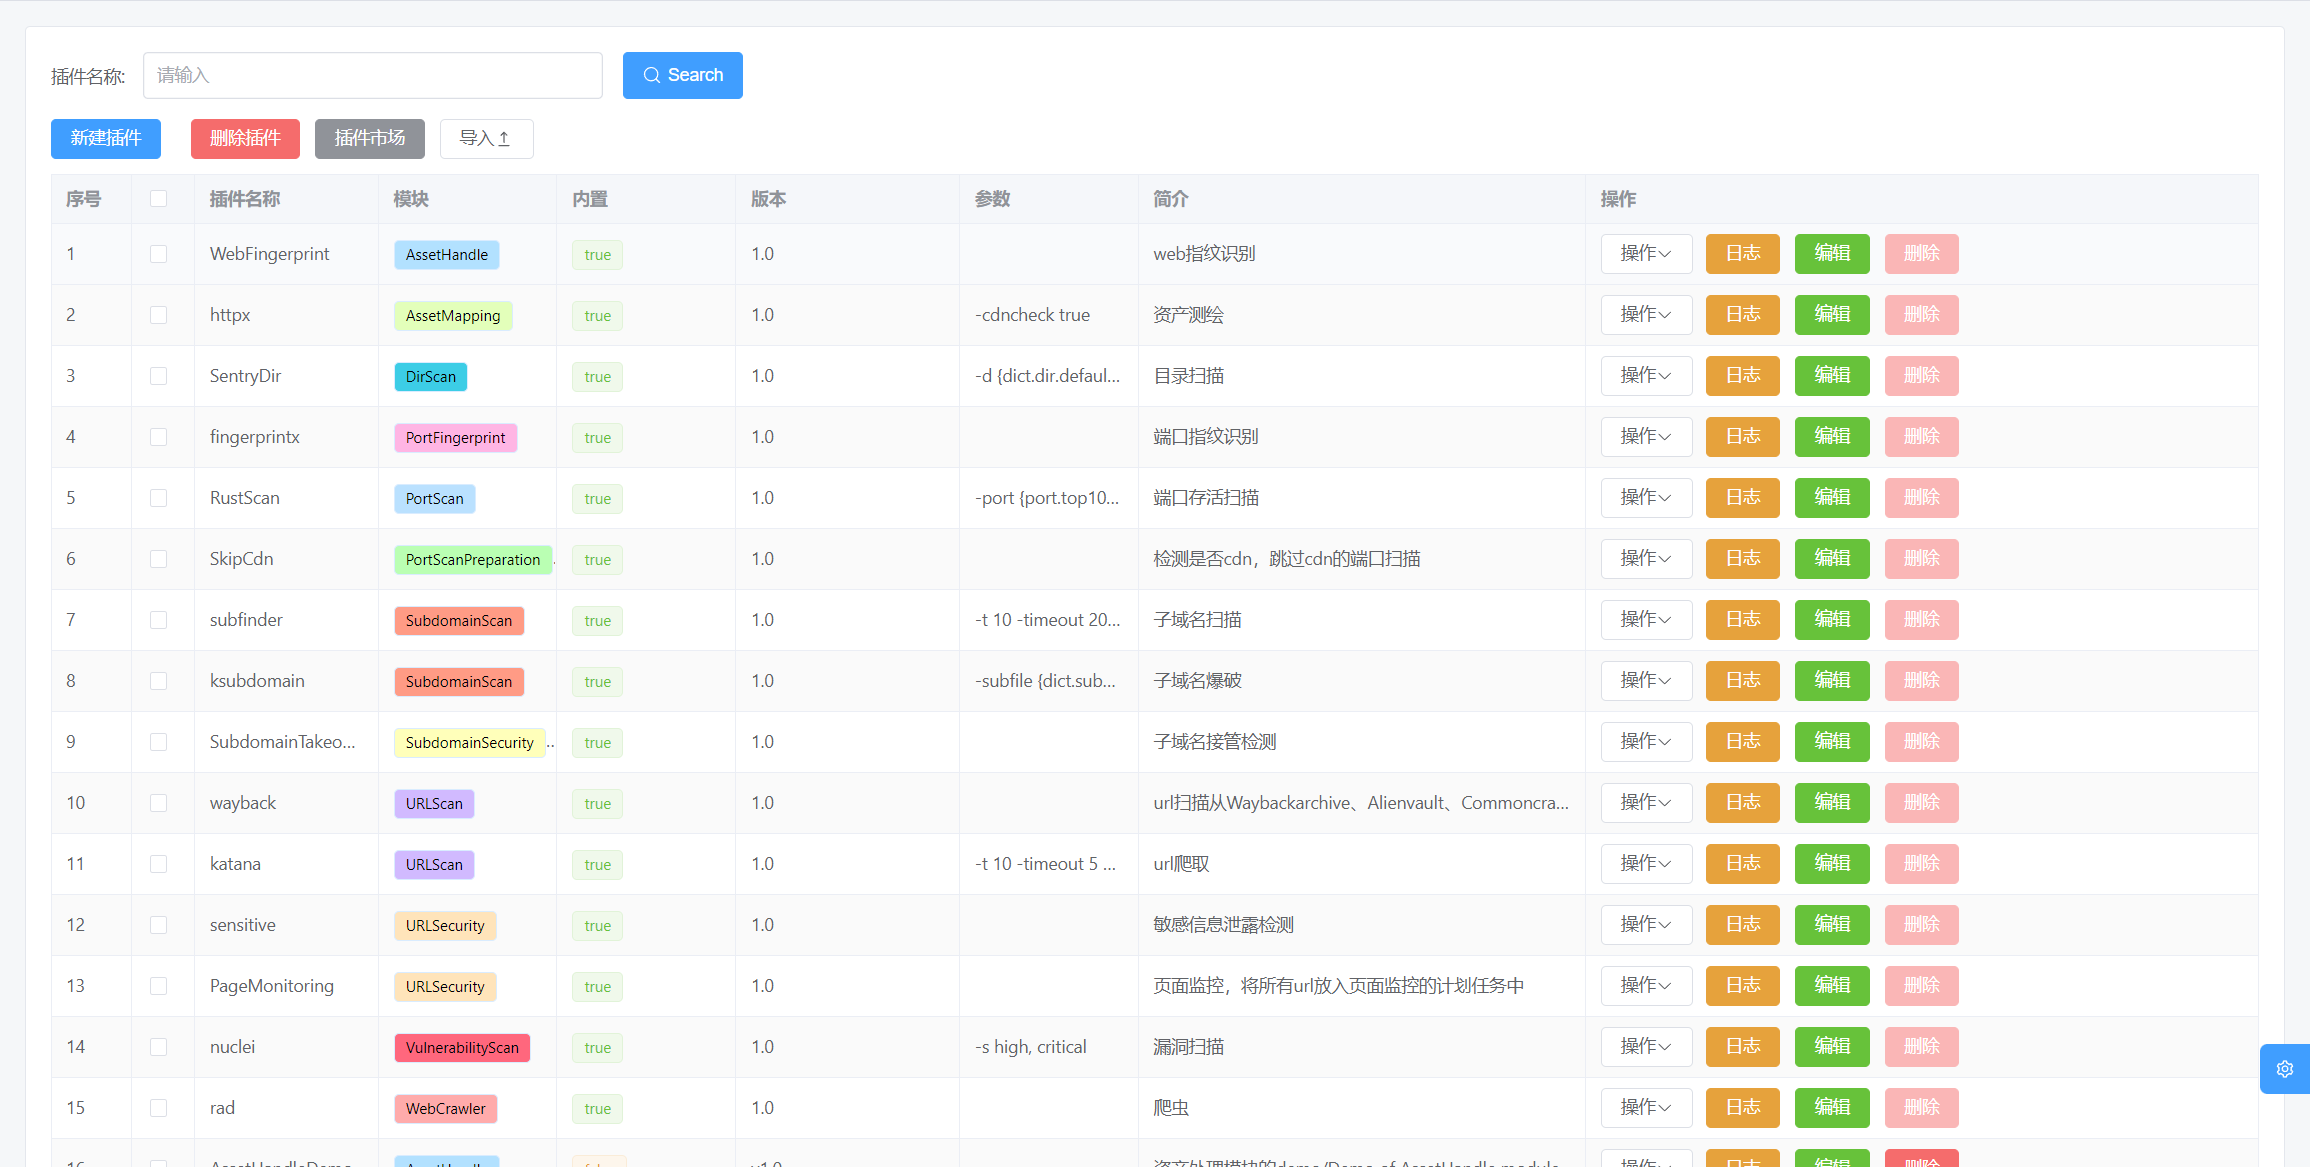
Plugin System
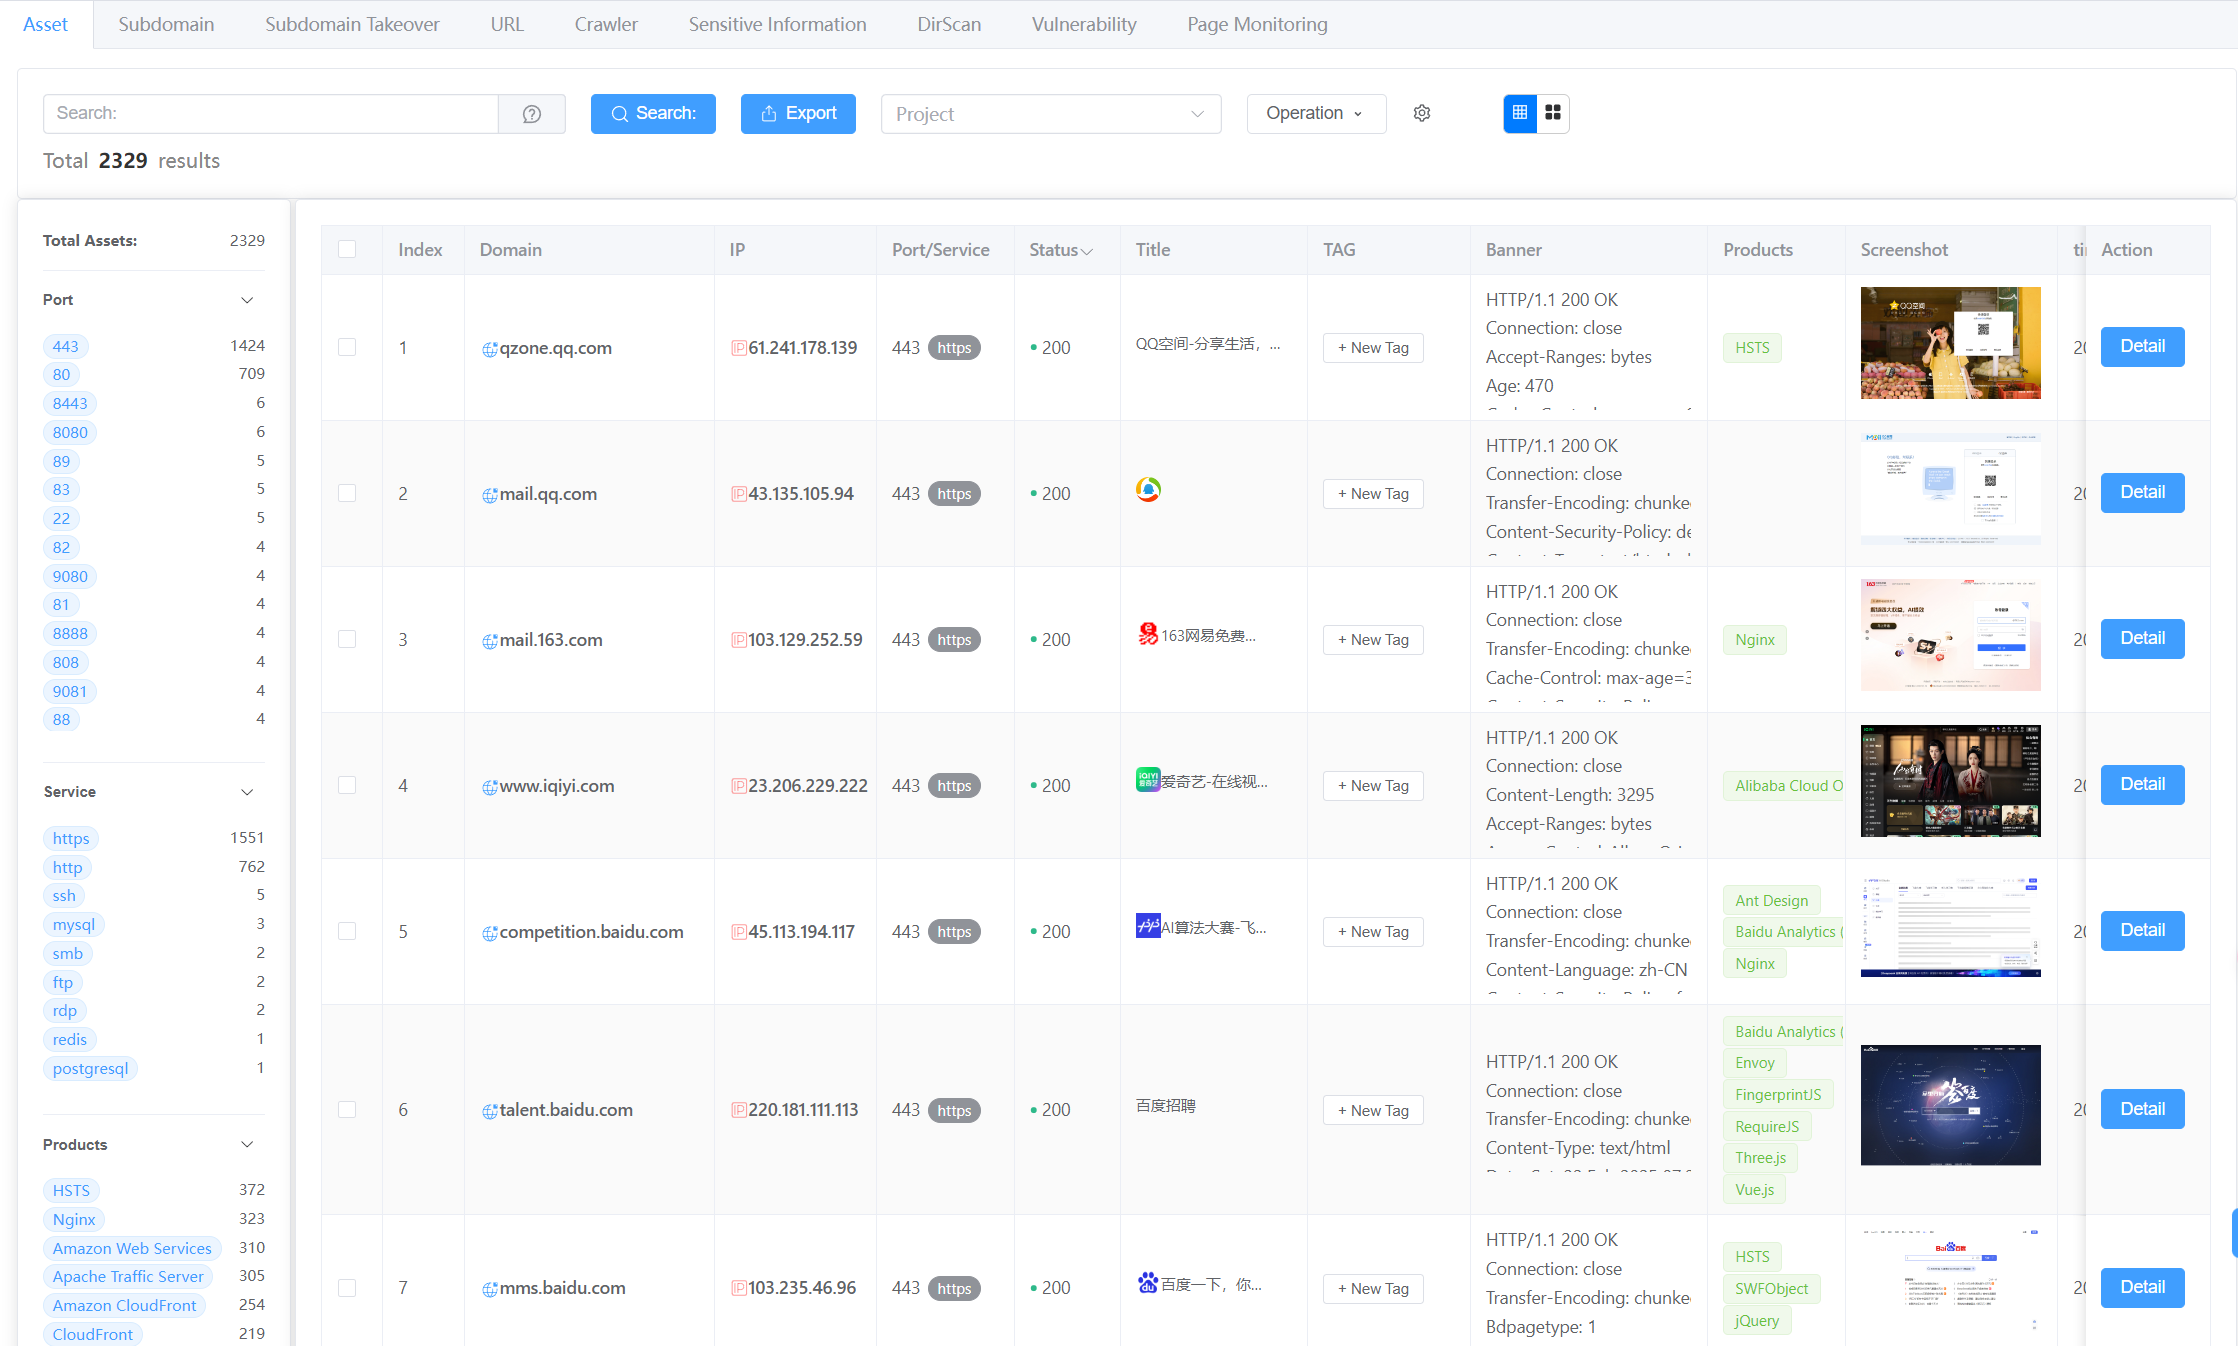
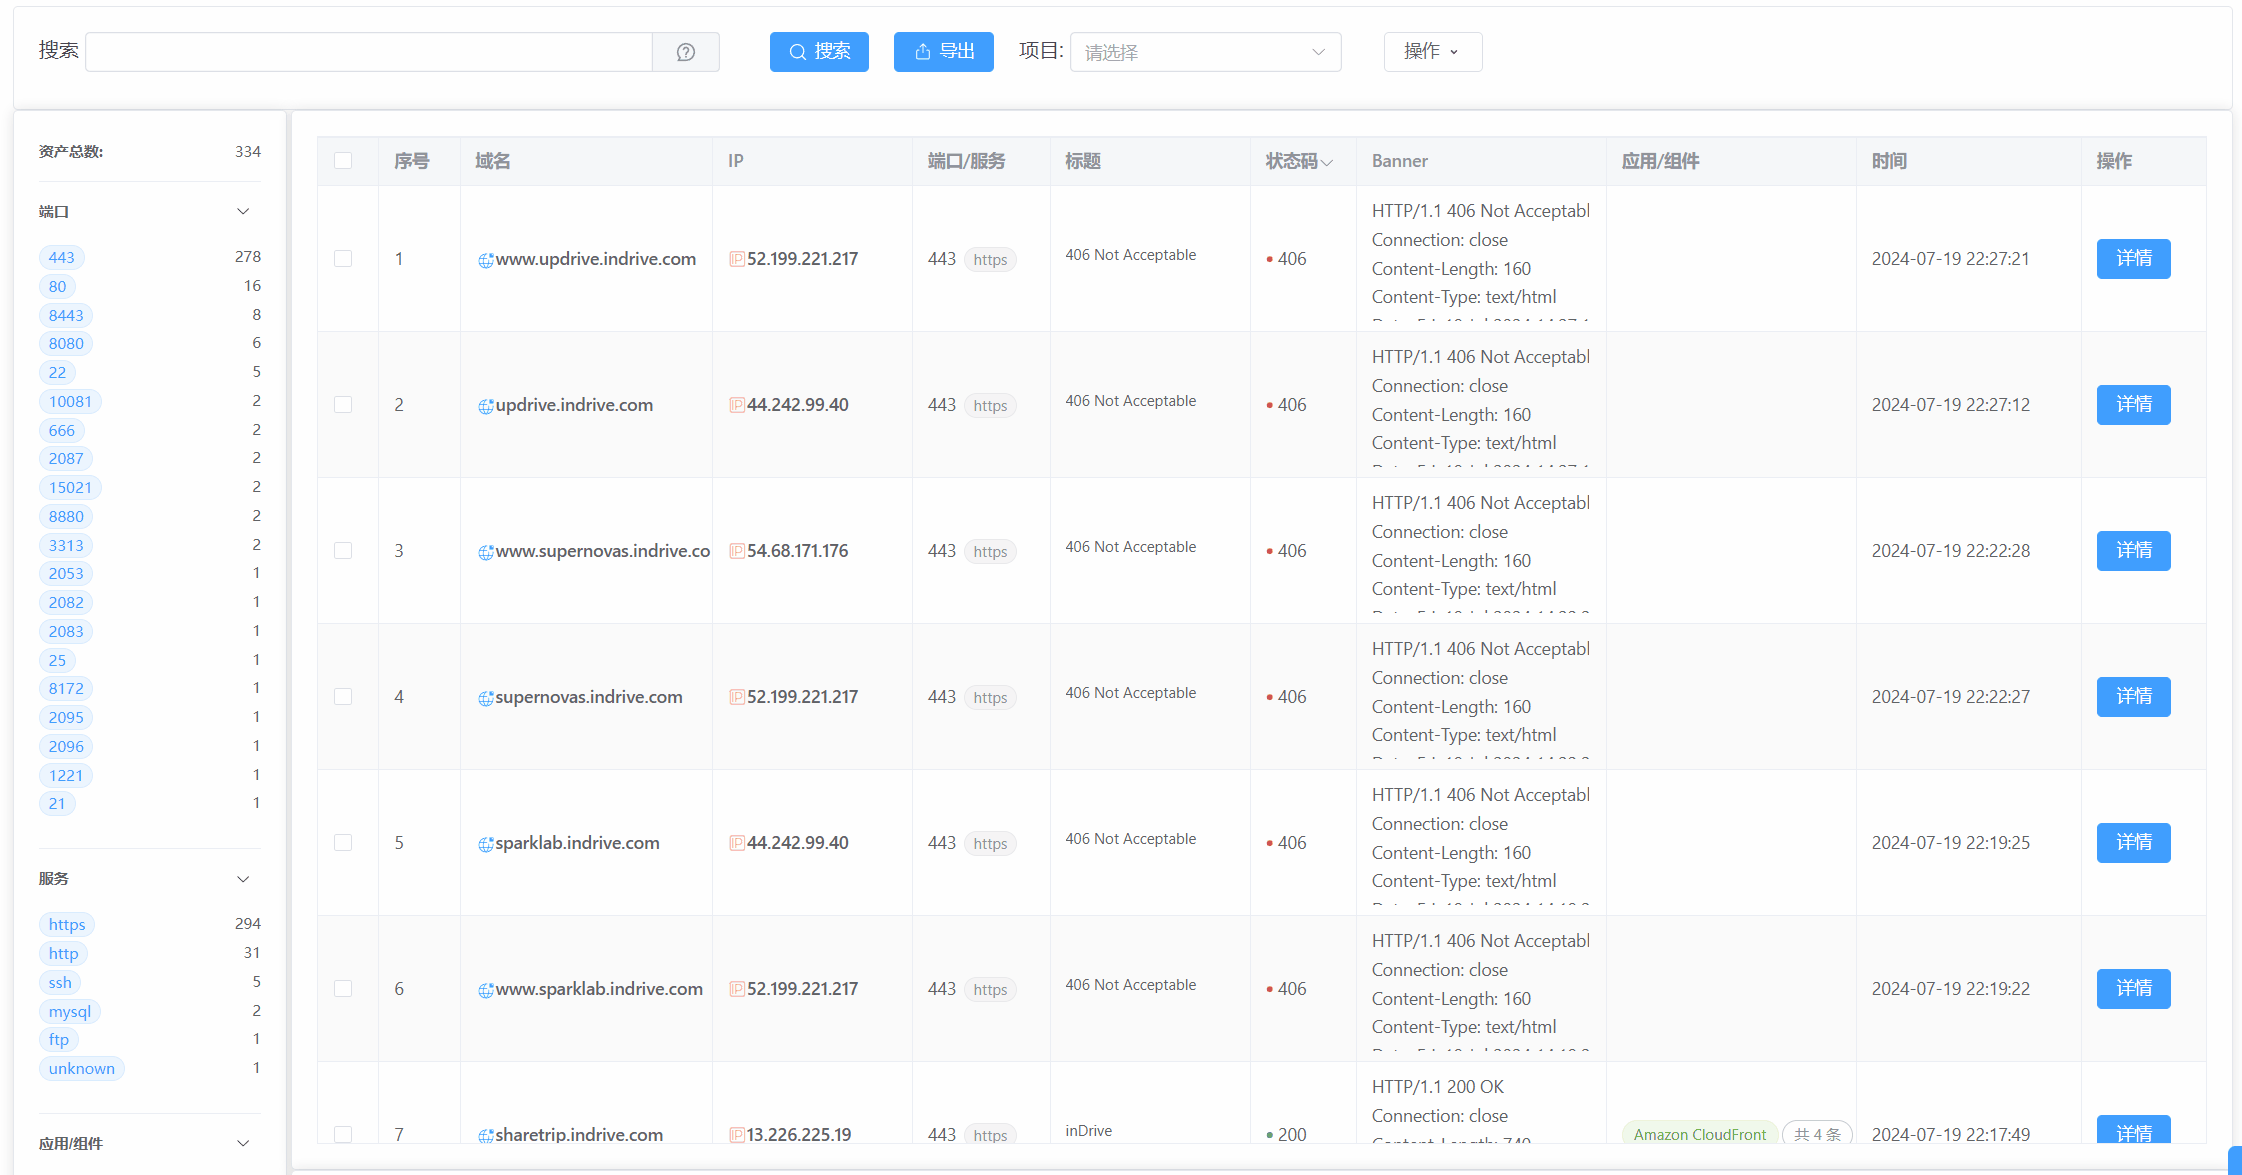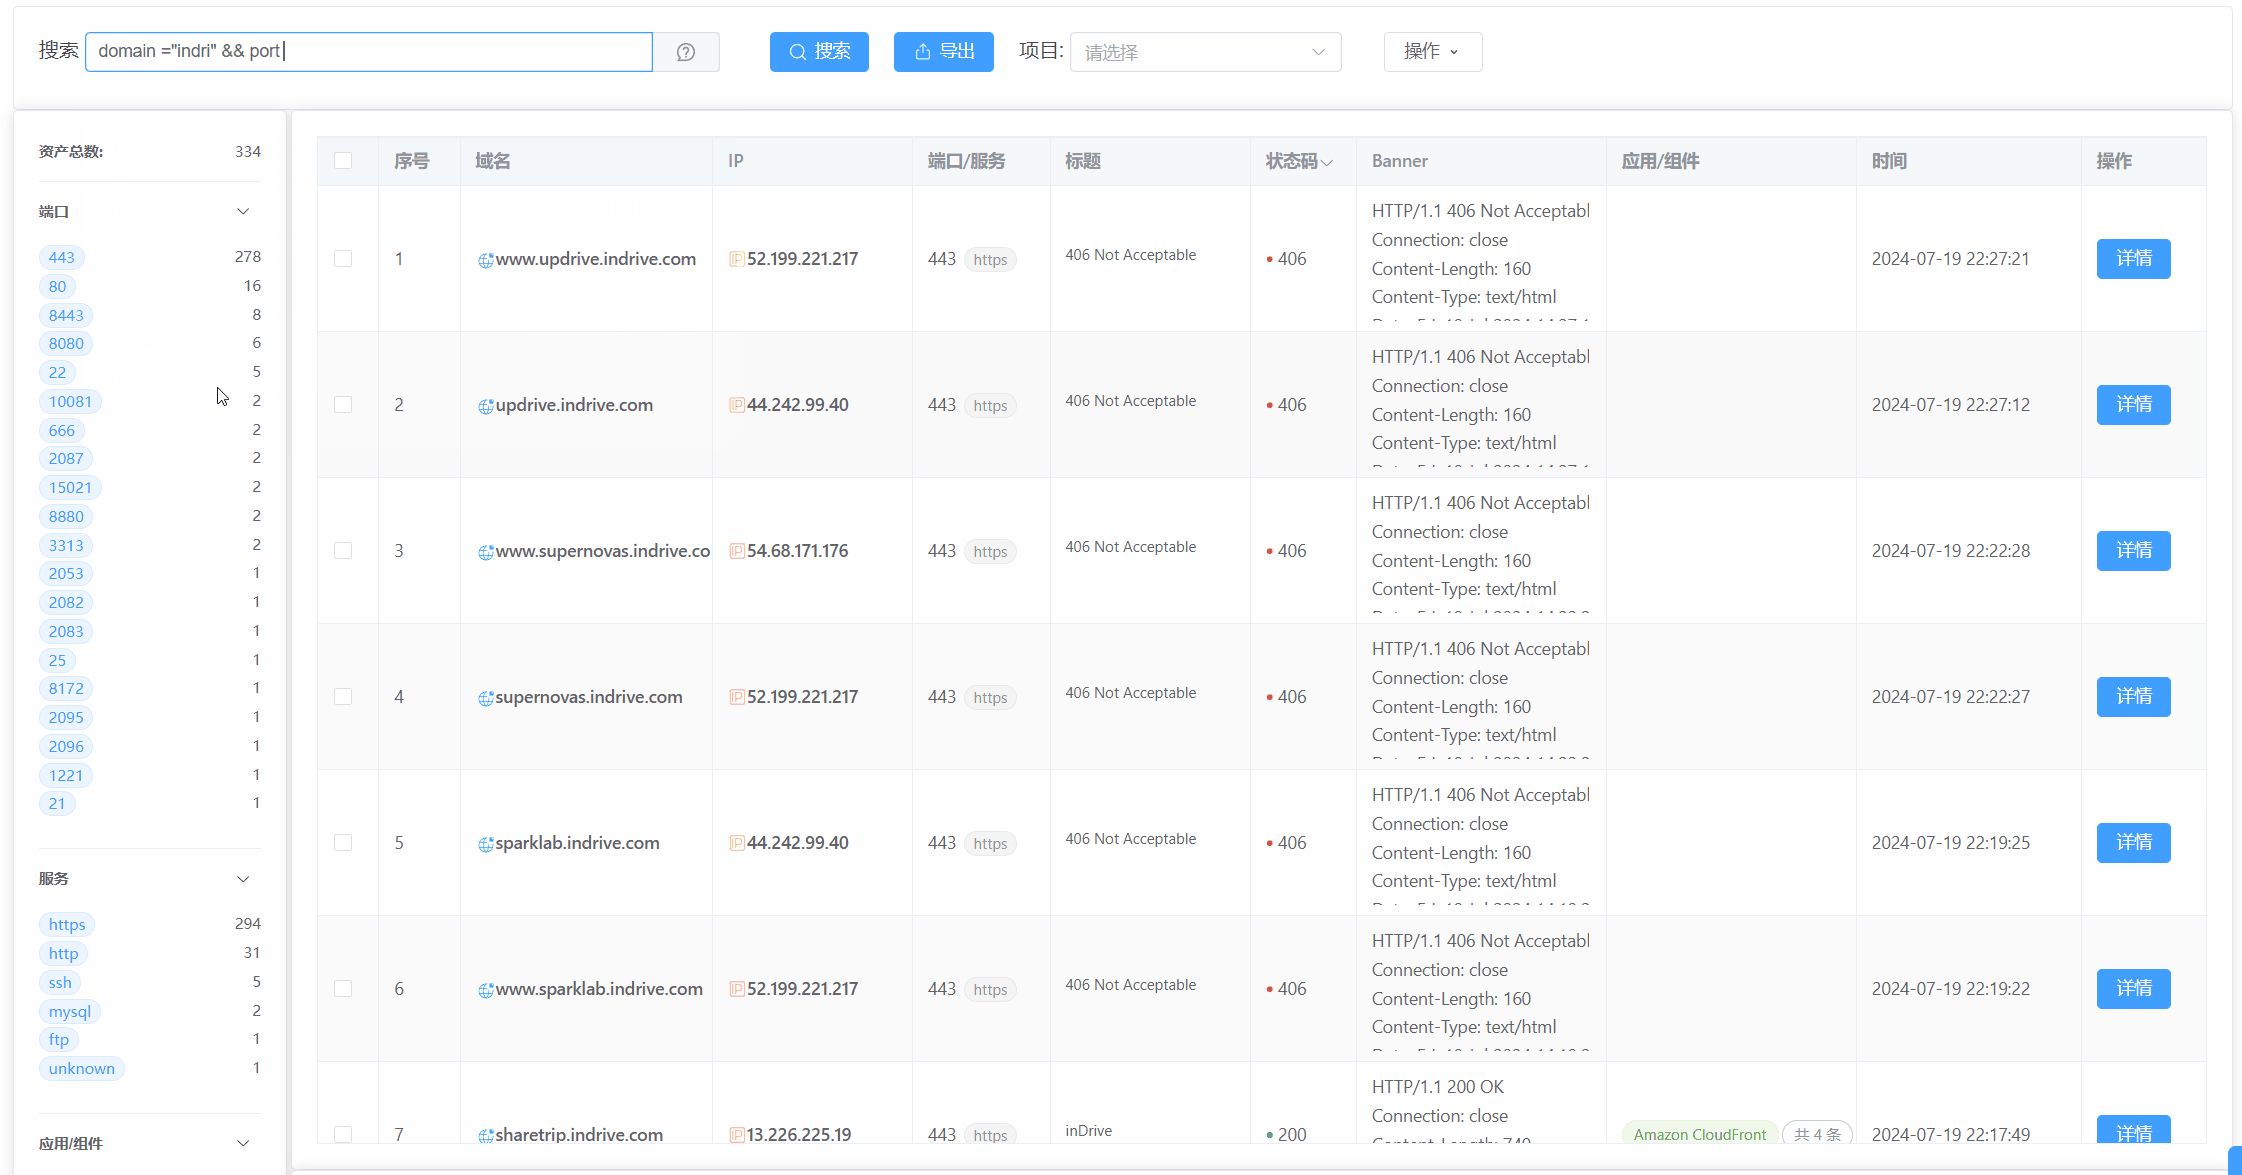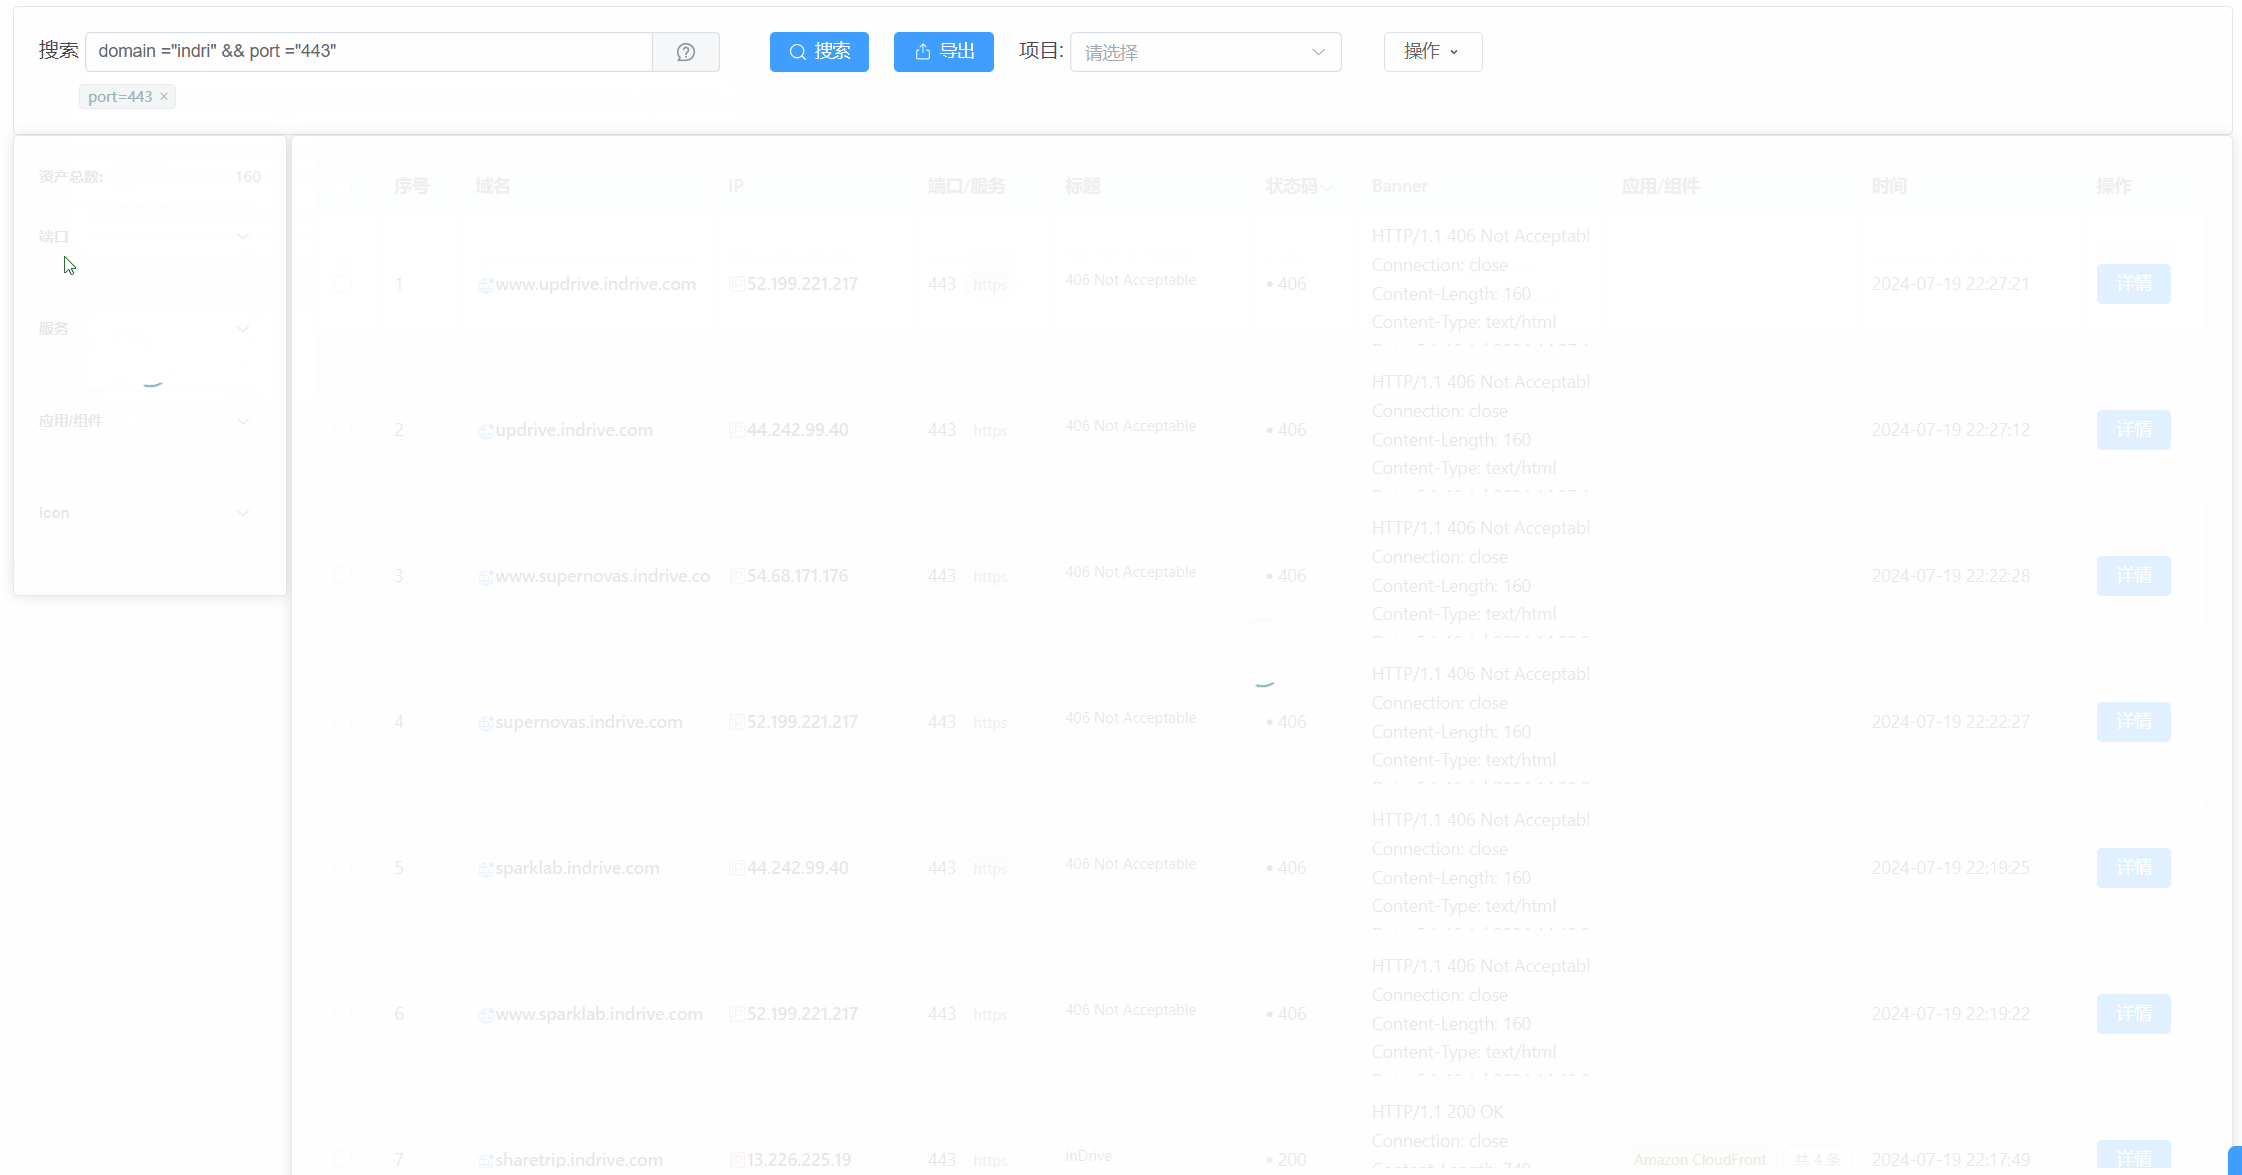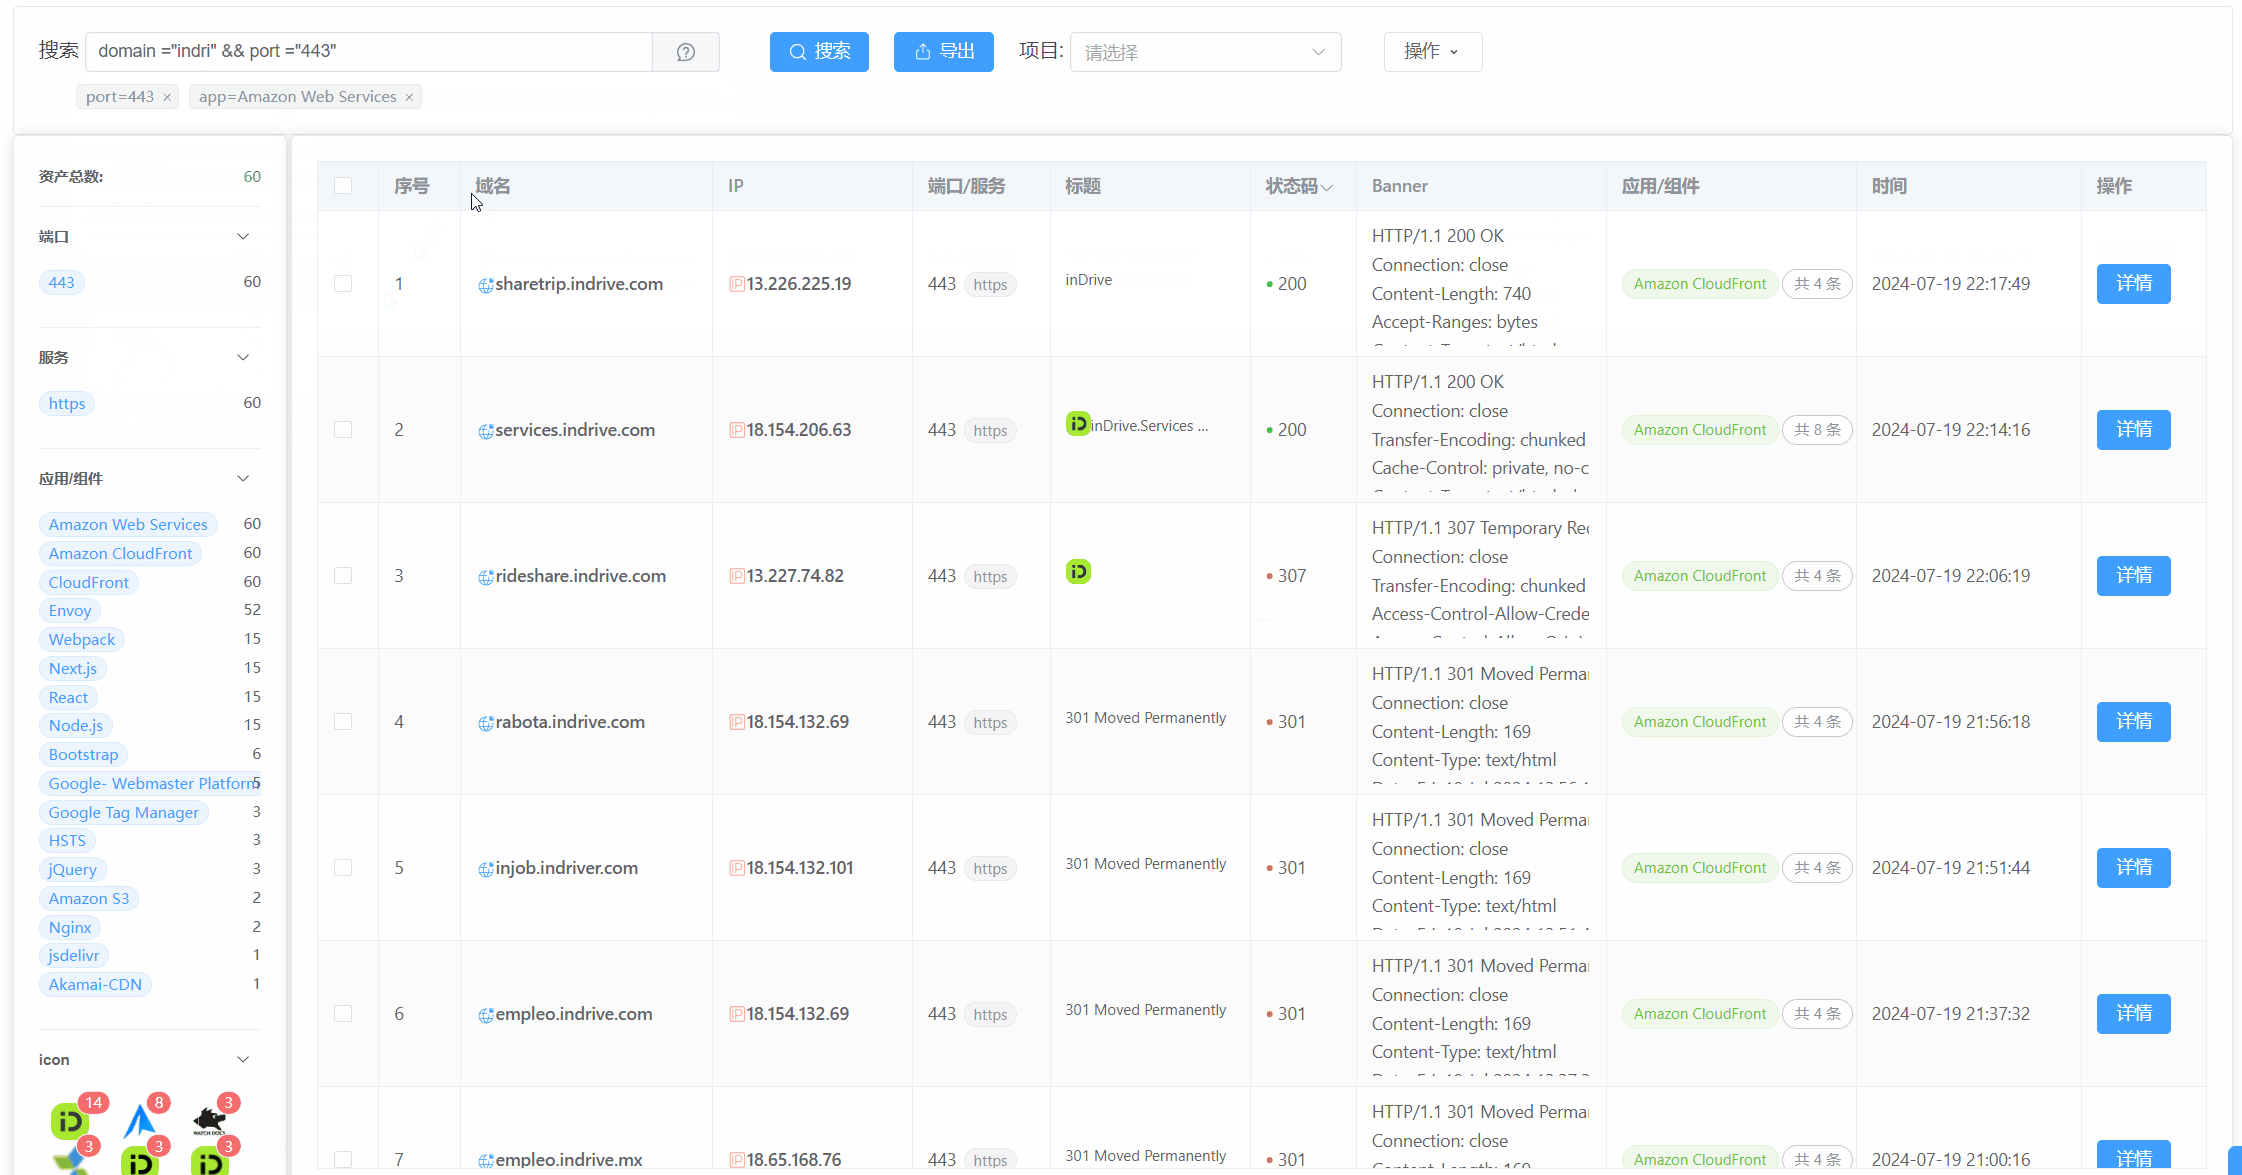
Asset Data
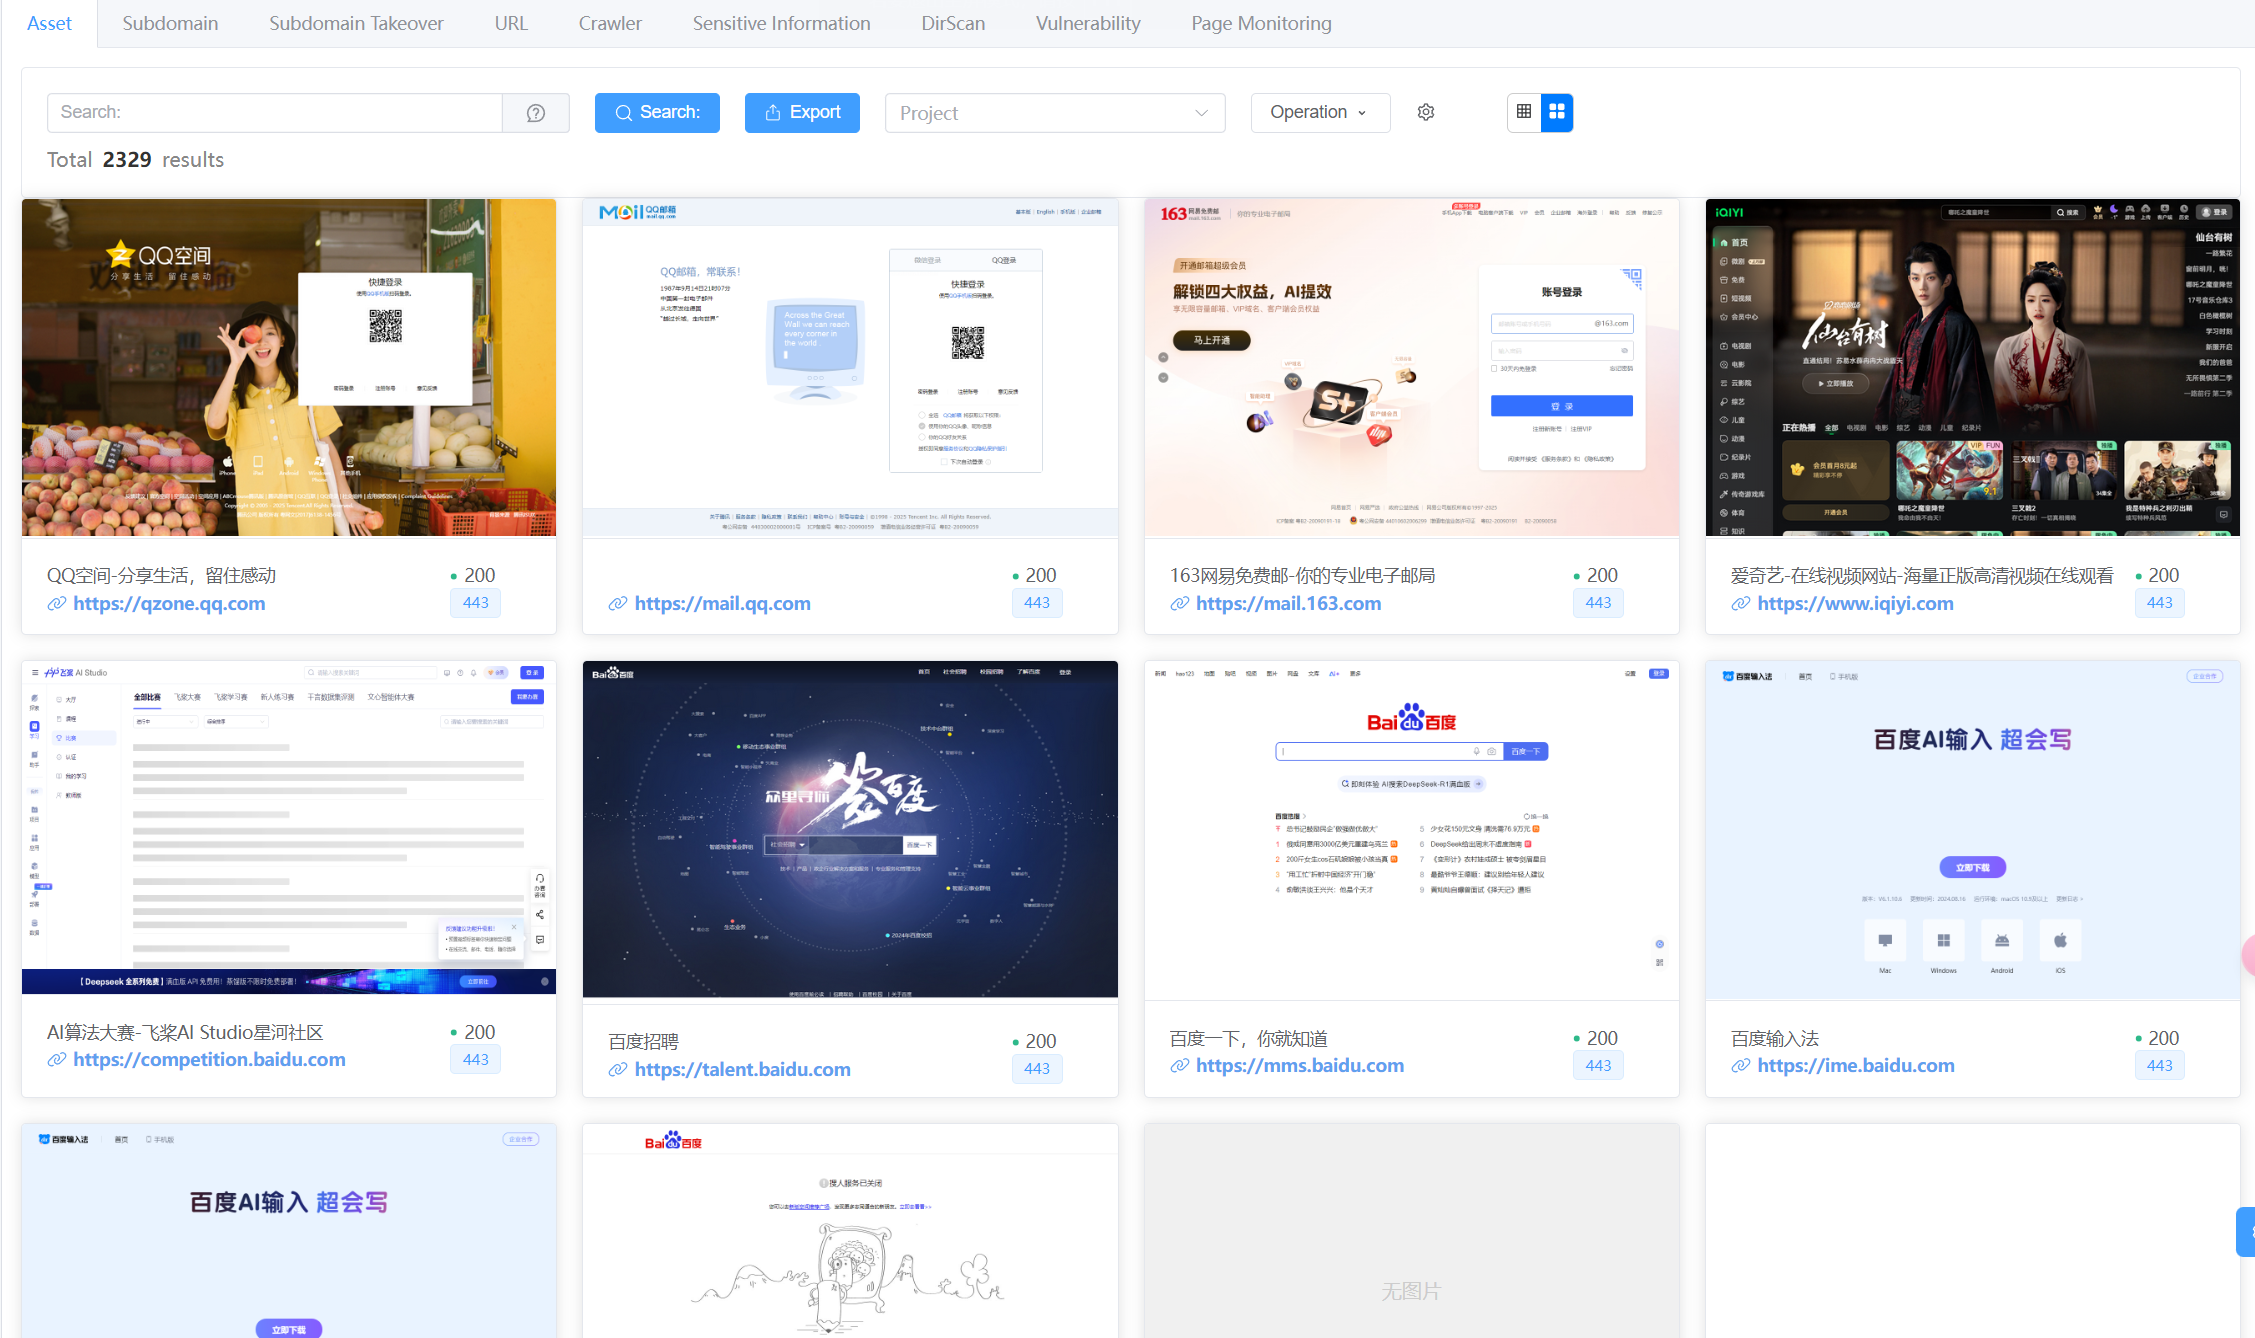
Assets
Quick syntax search:
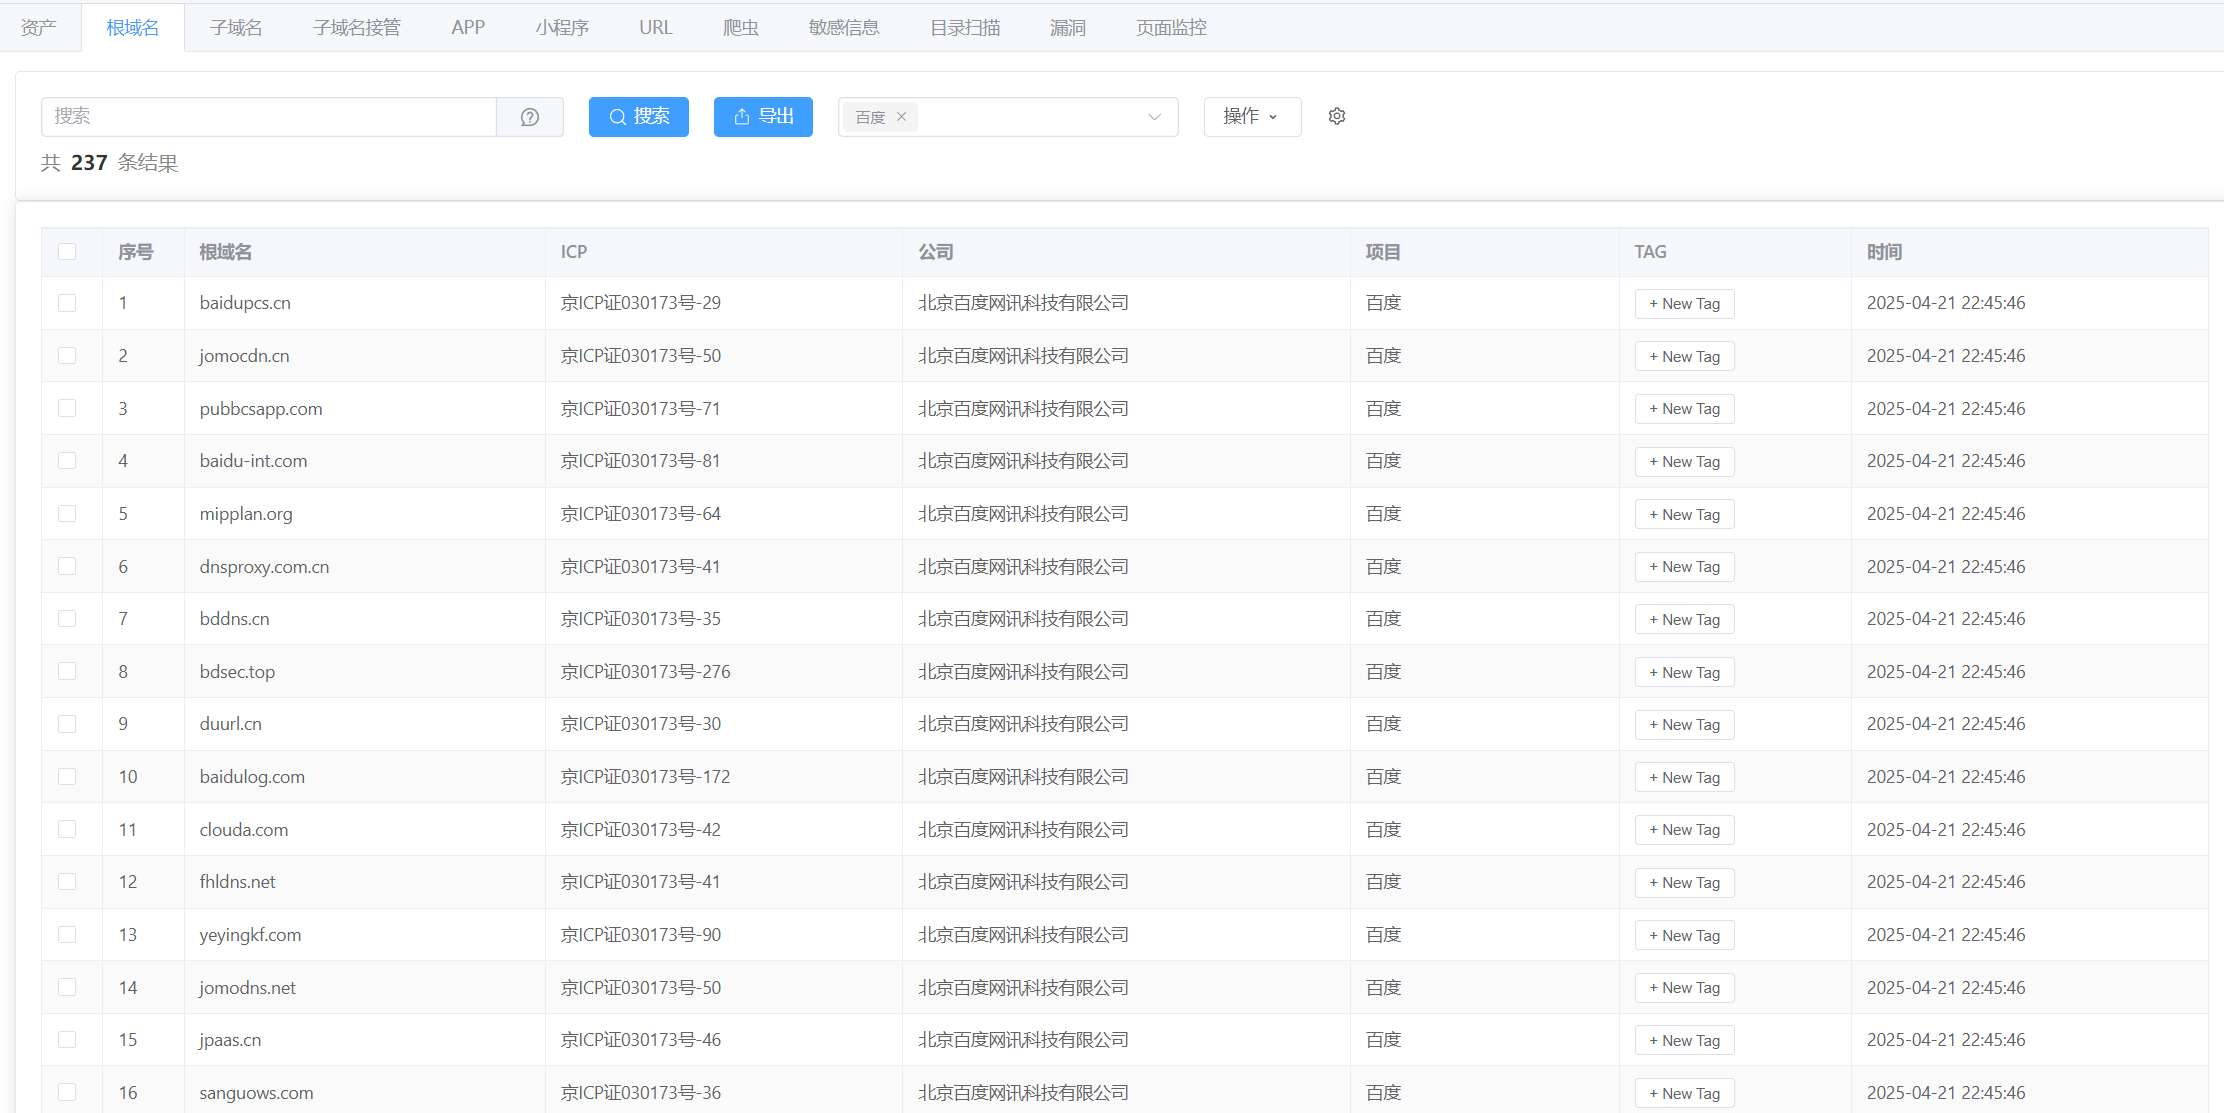
Root Domain
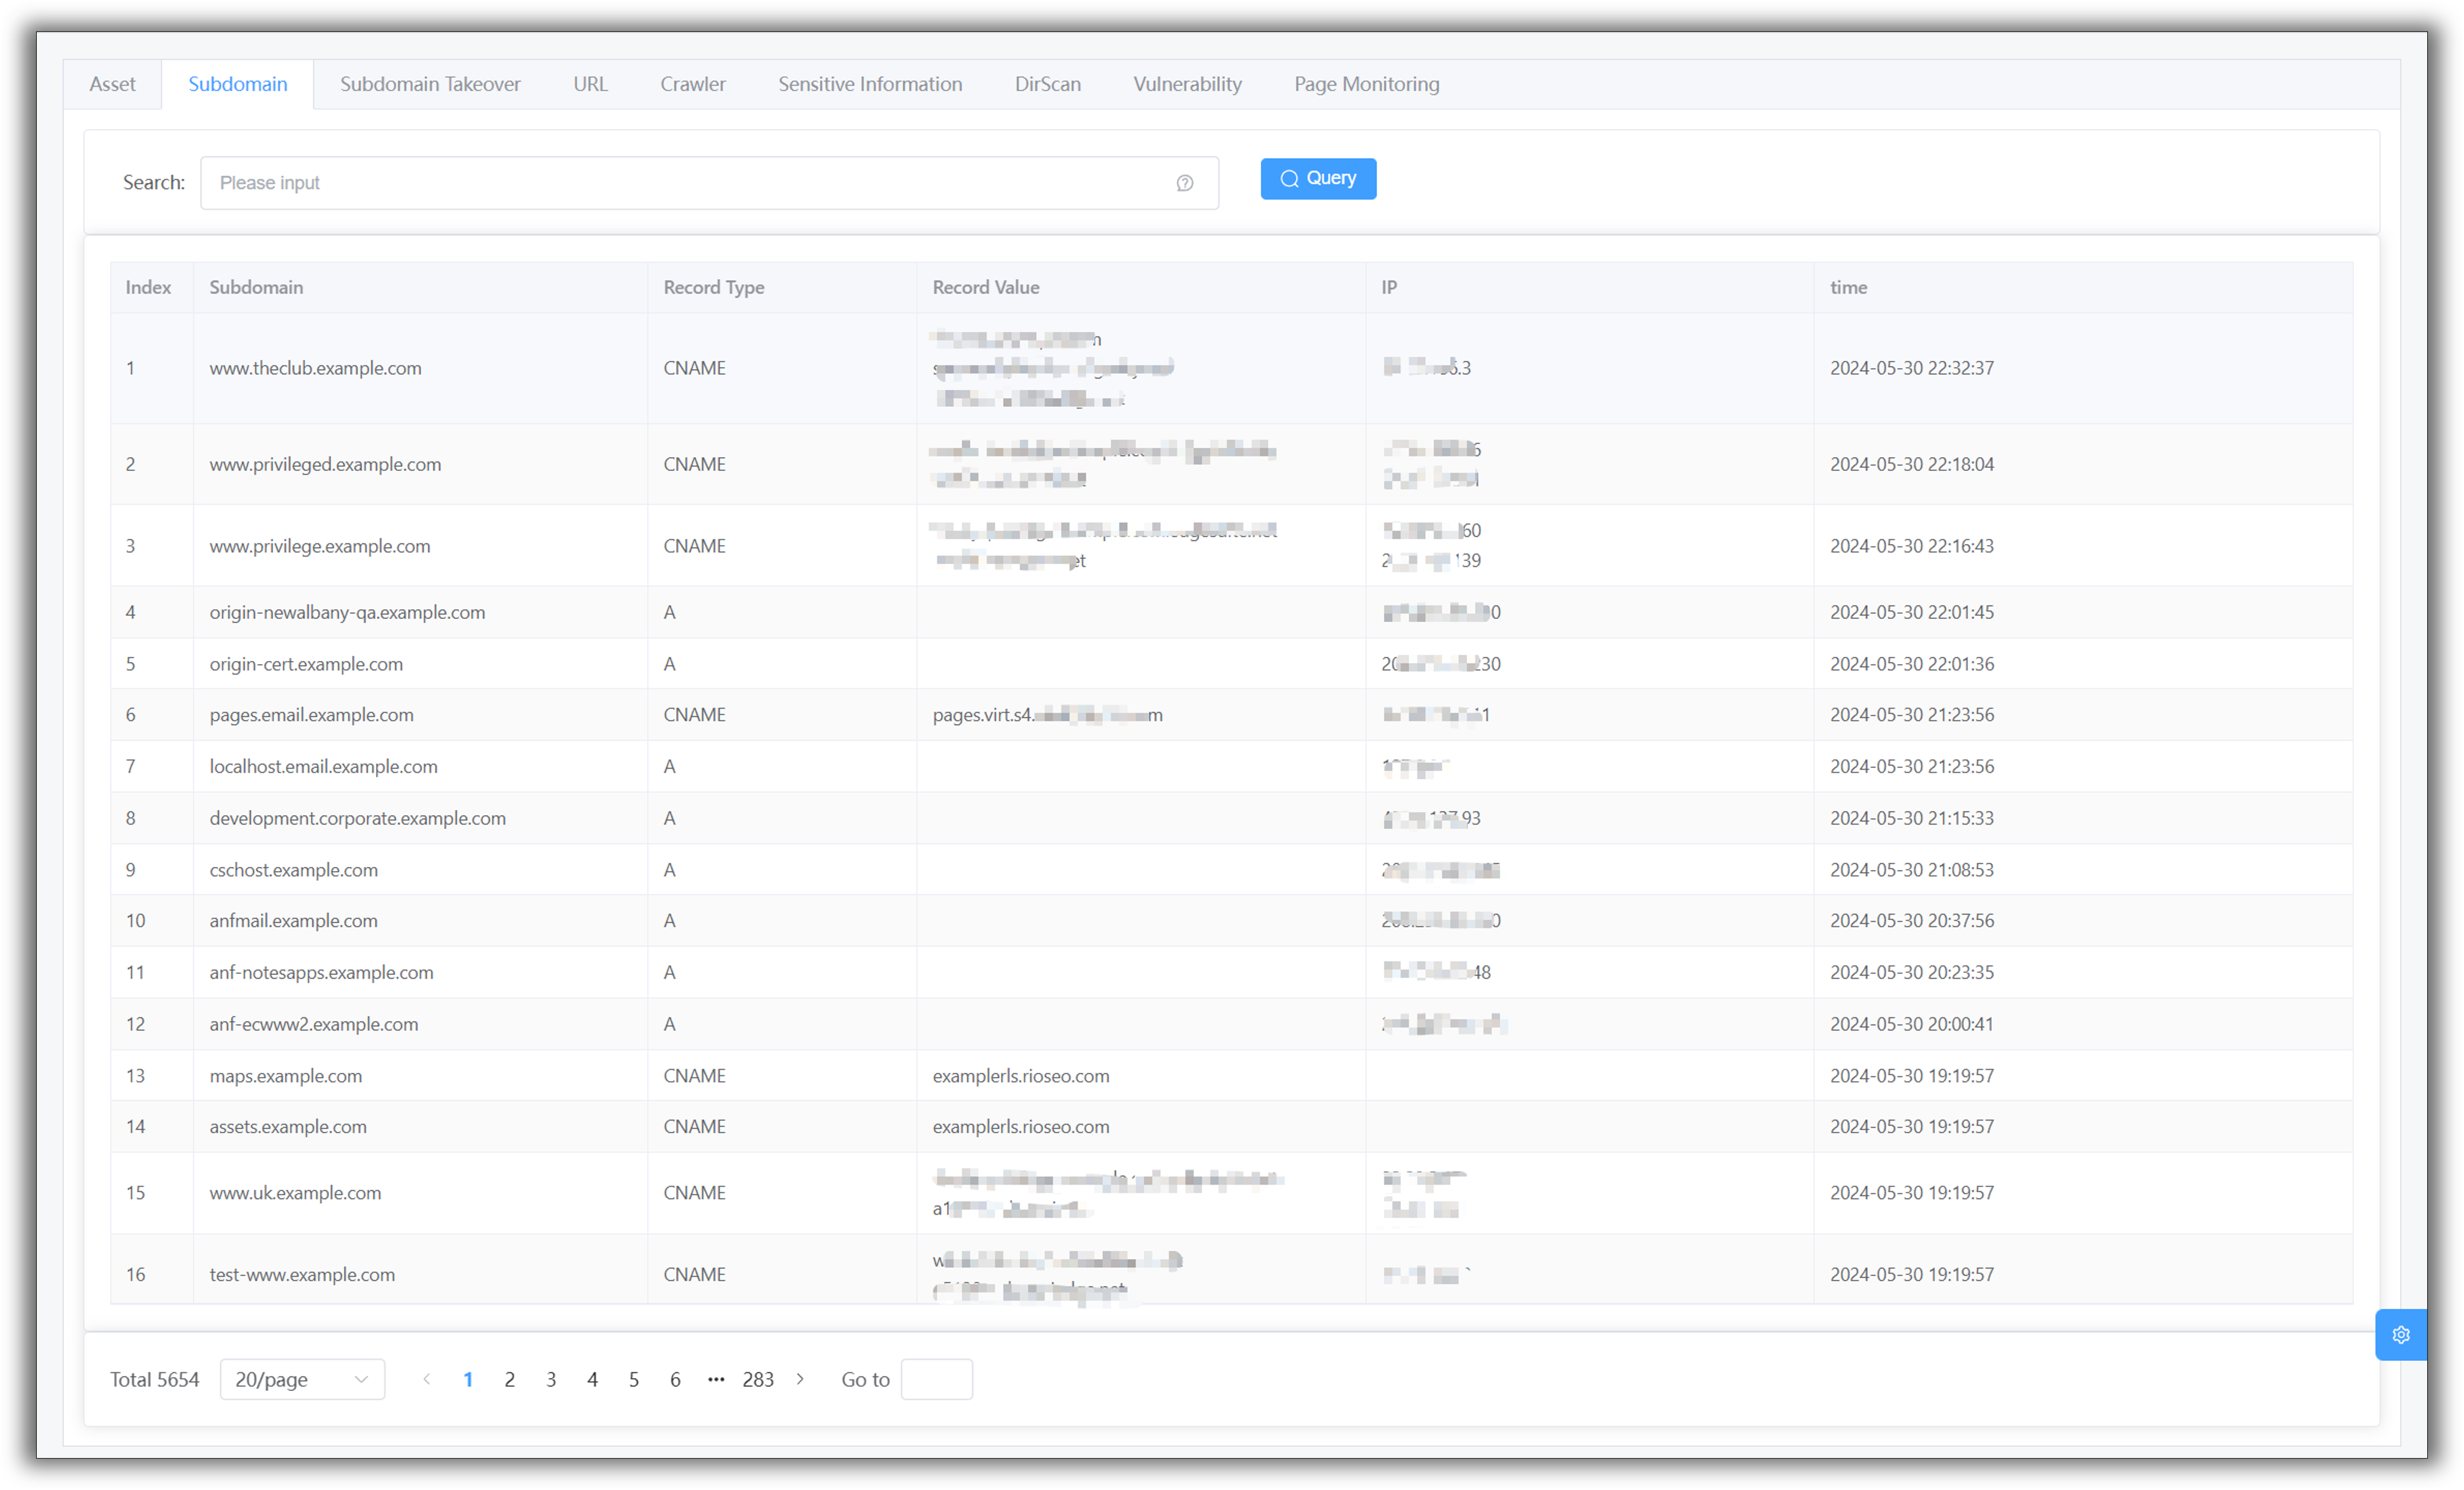
Subdomains
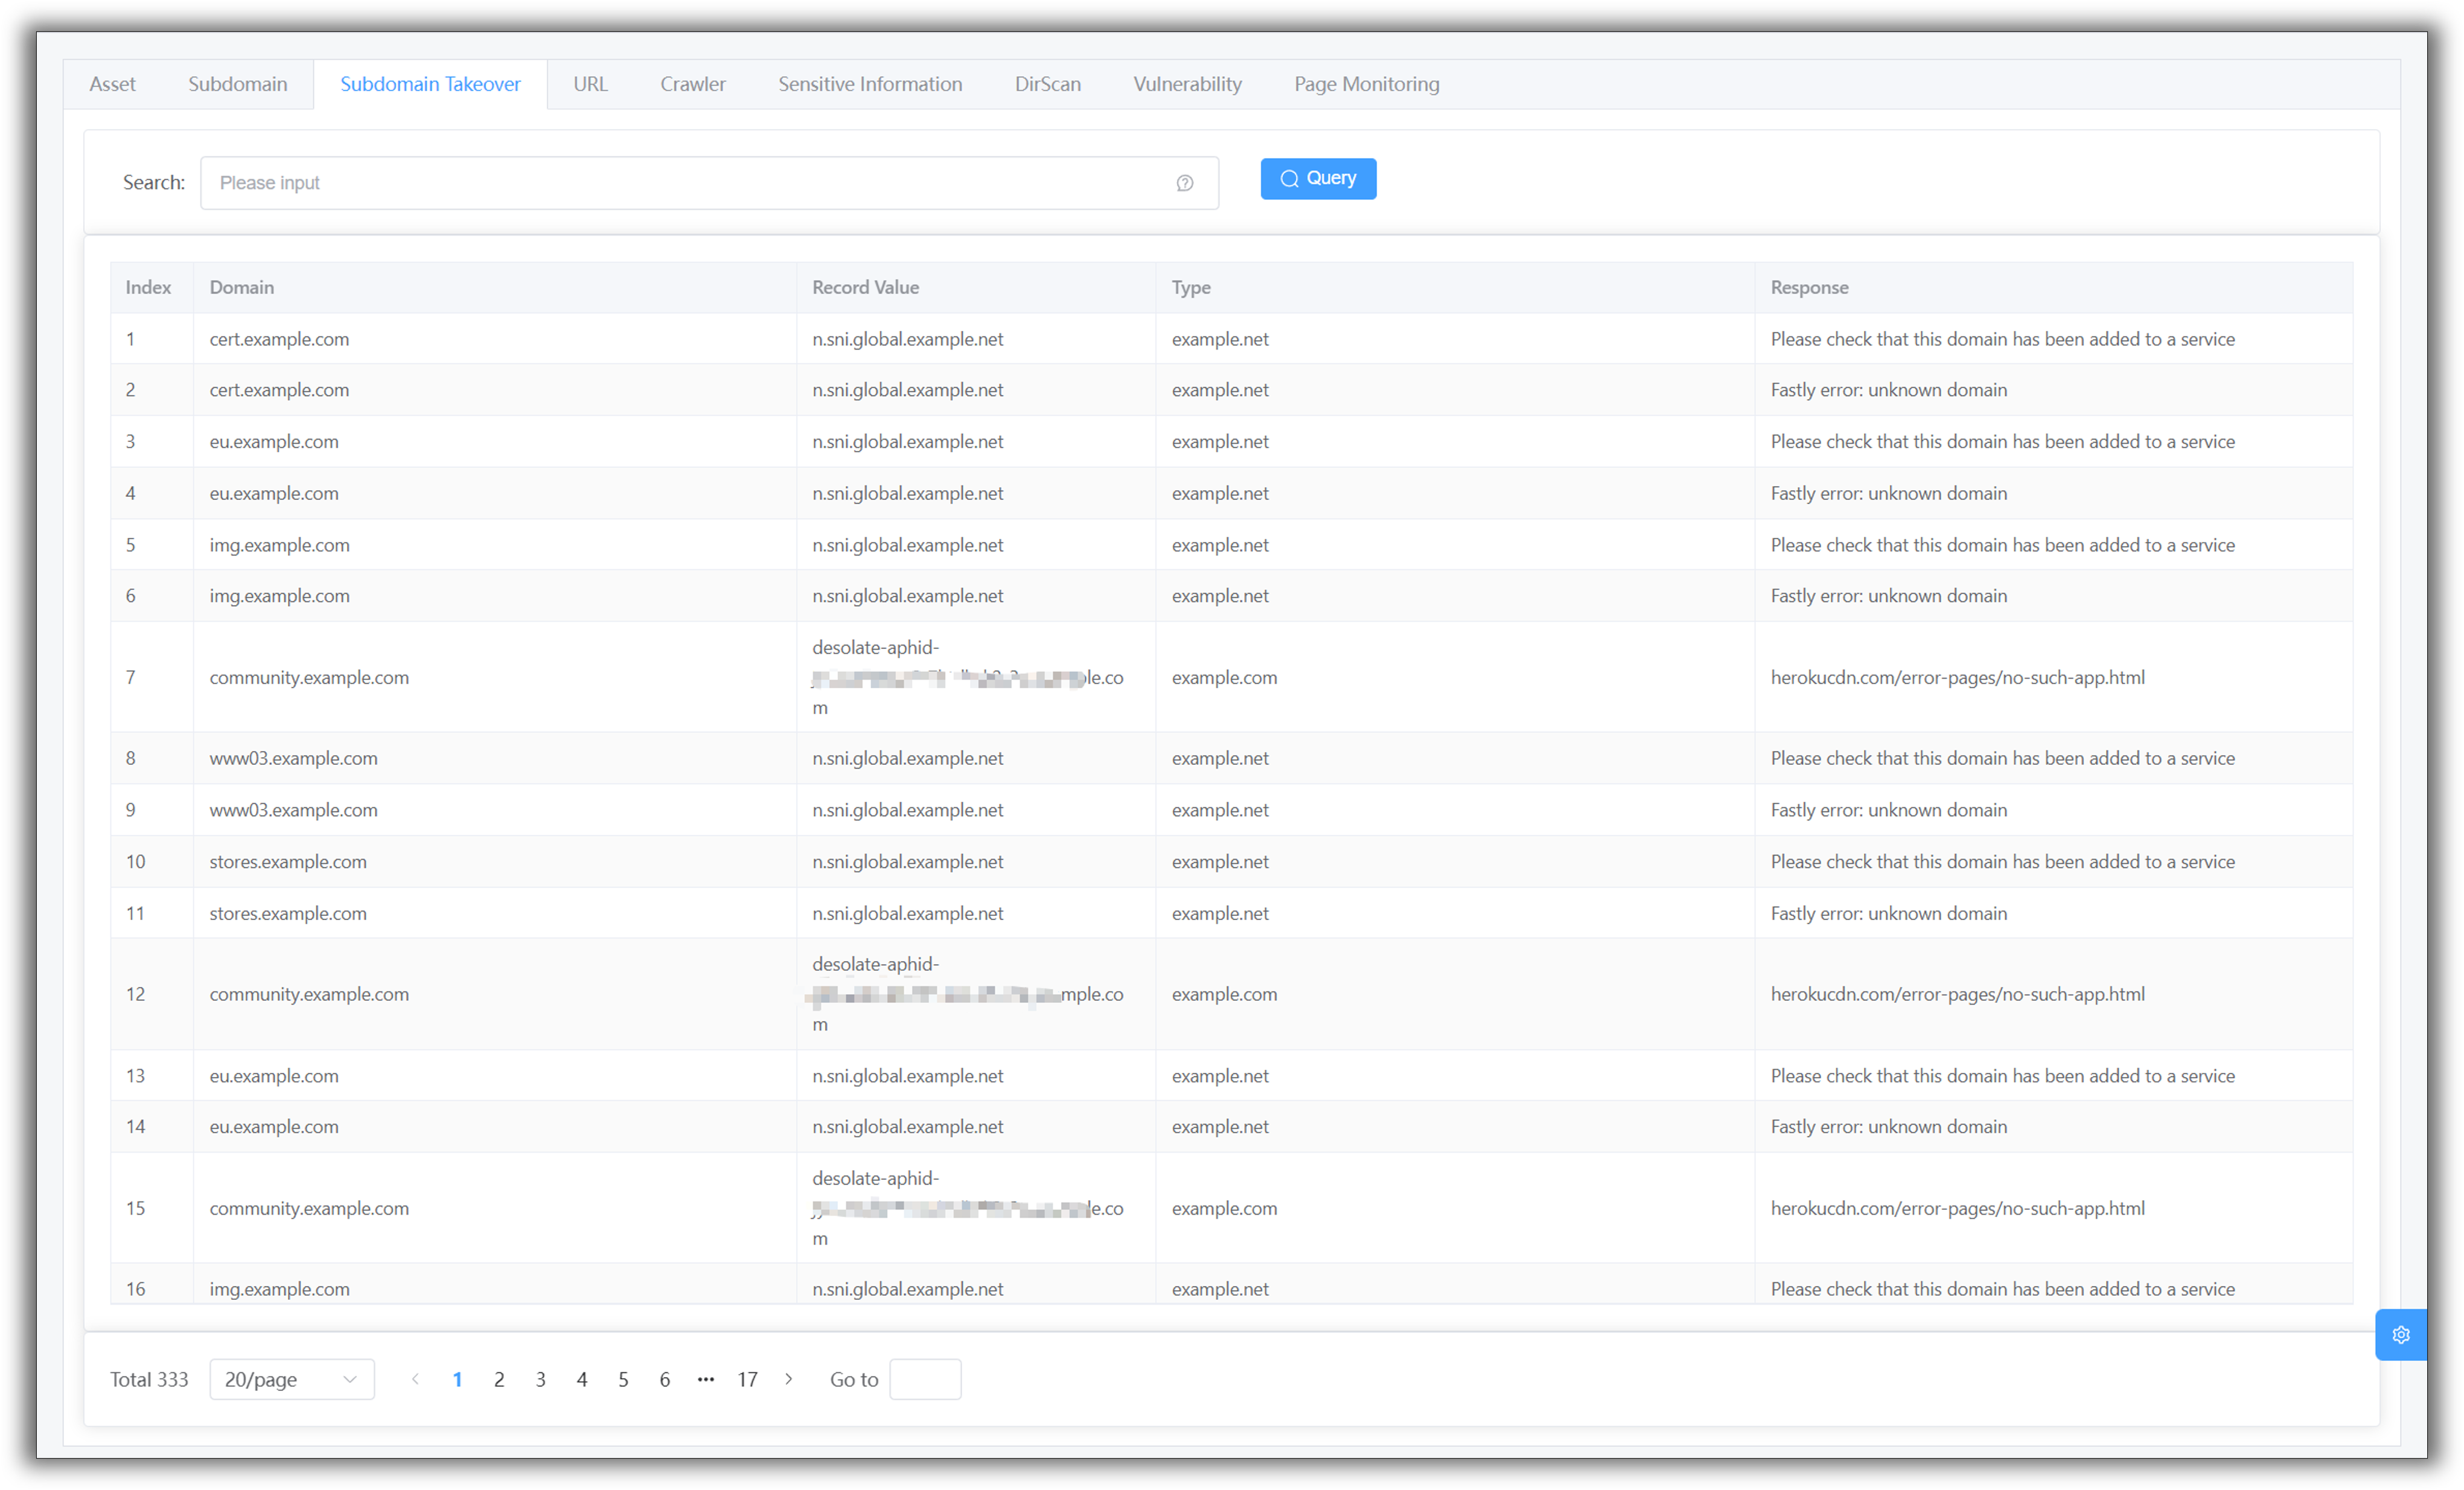
Subdomain Takeover
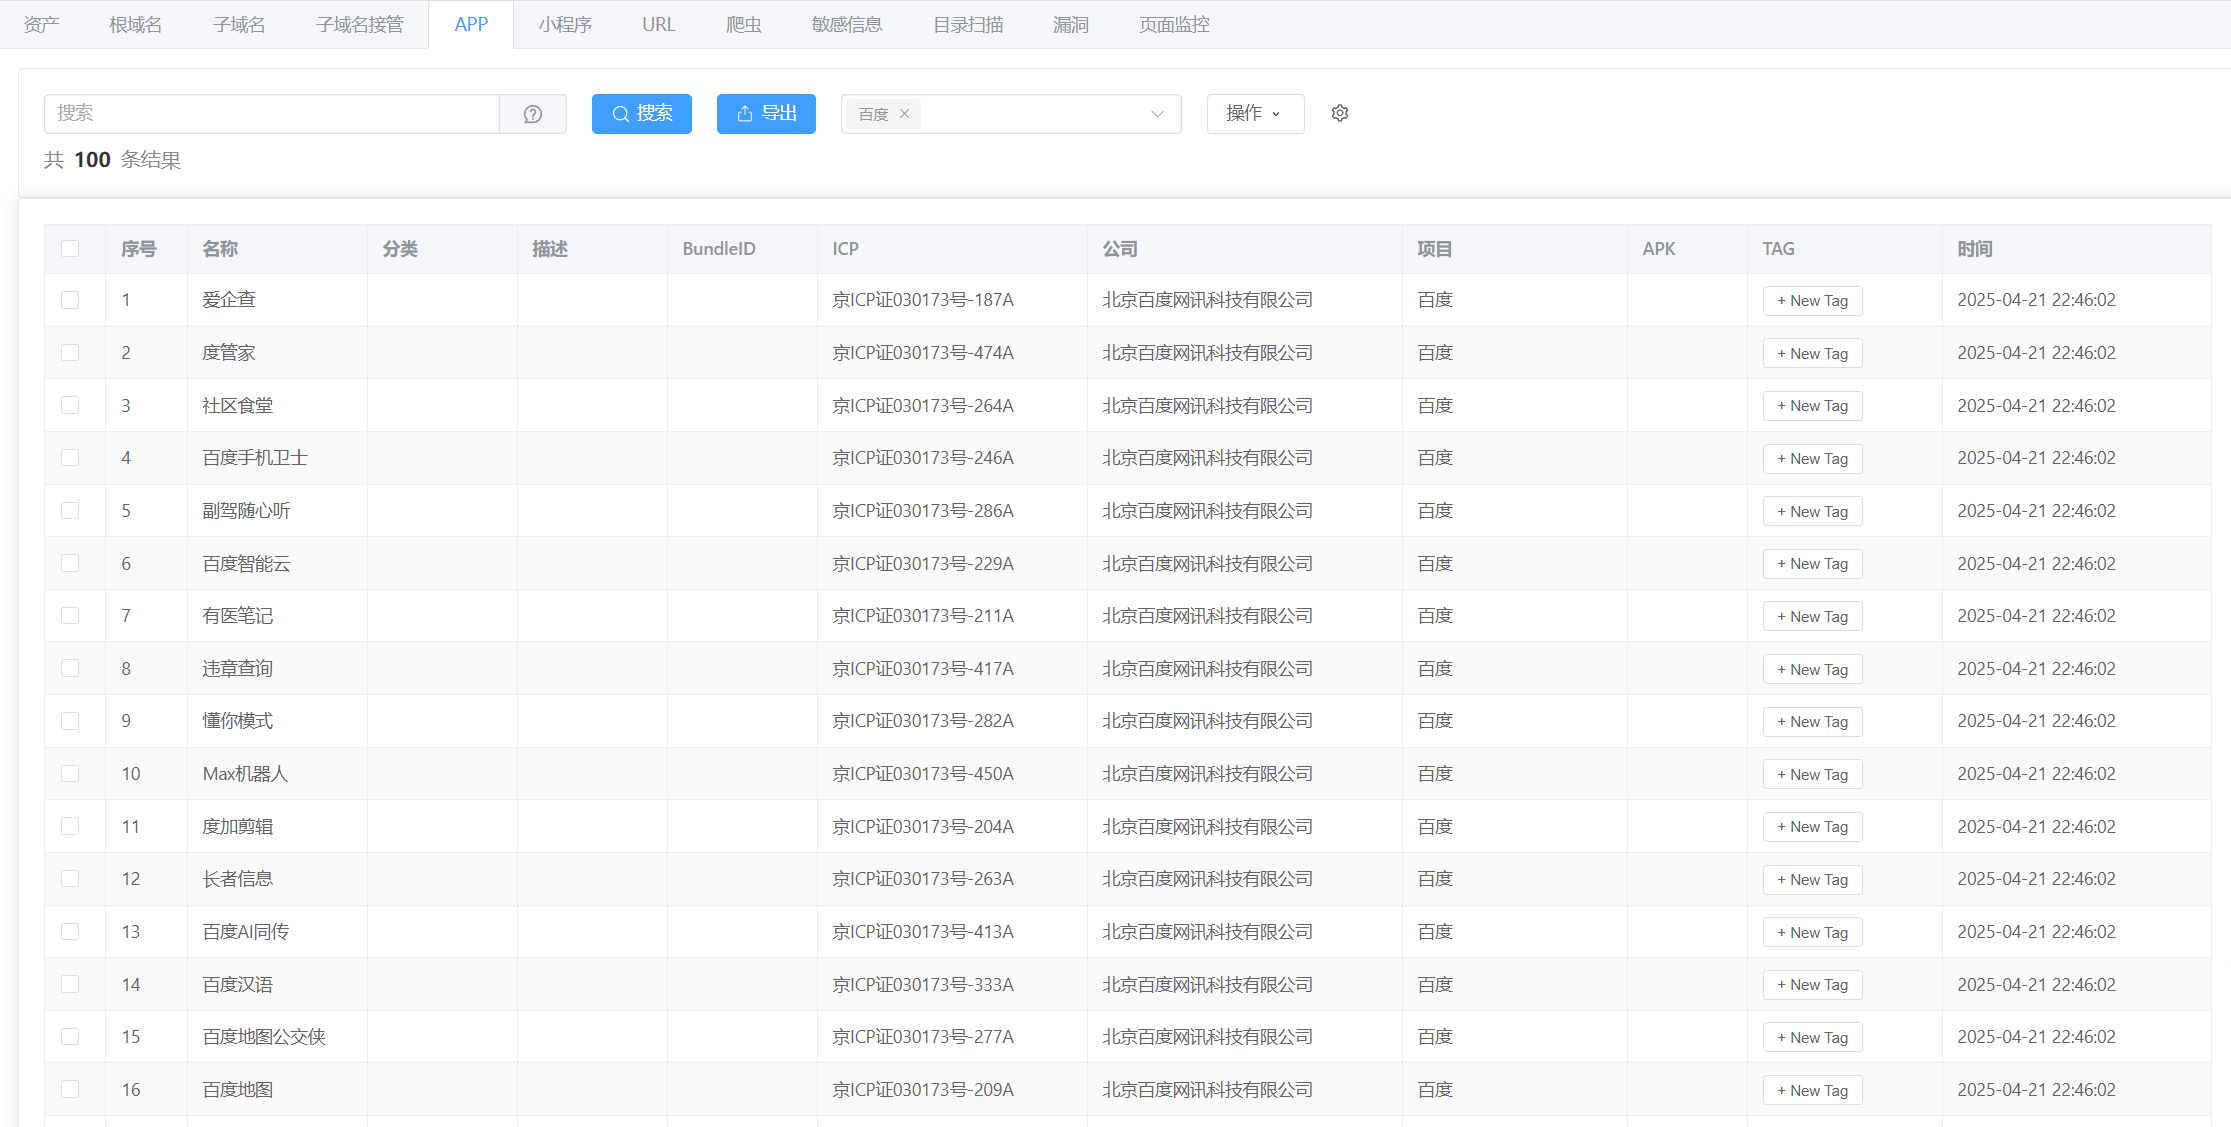
APP
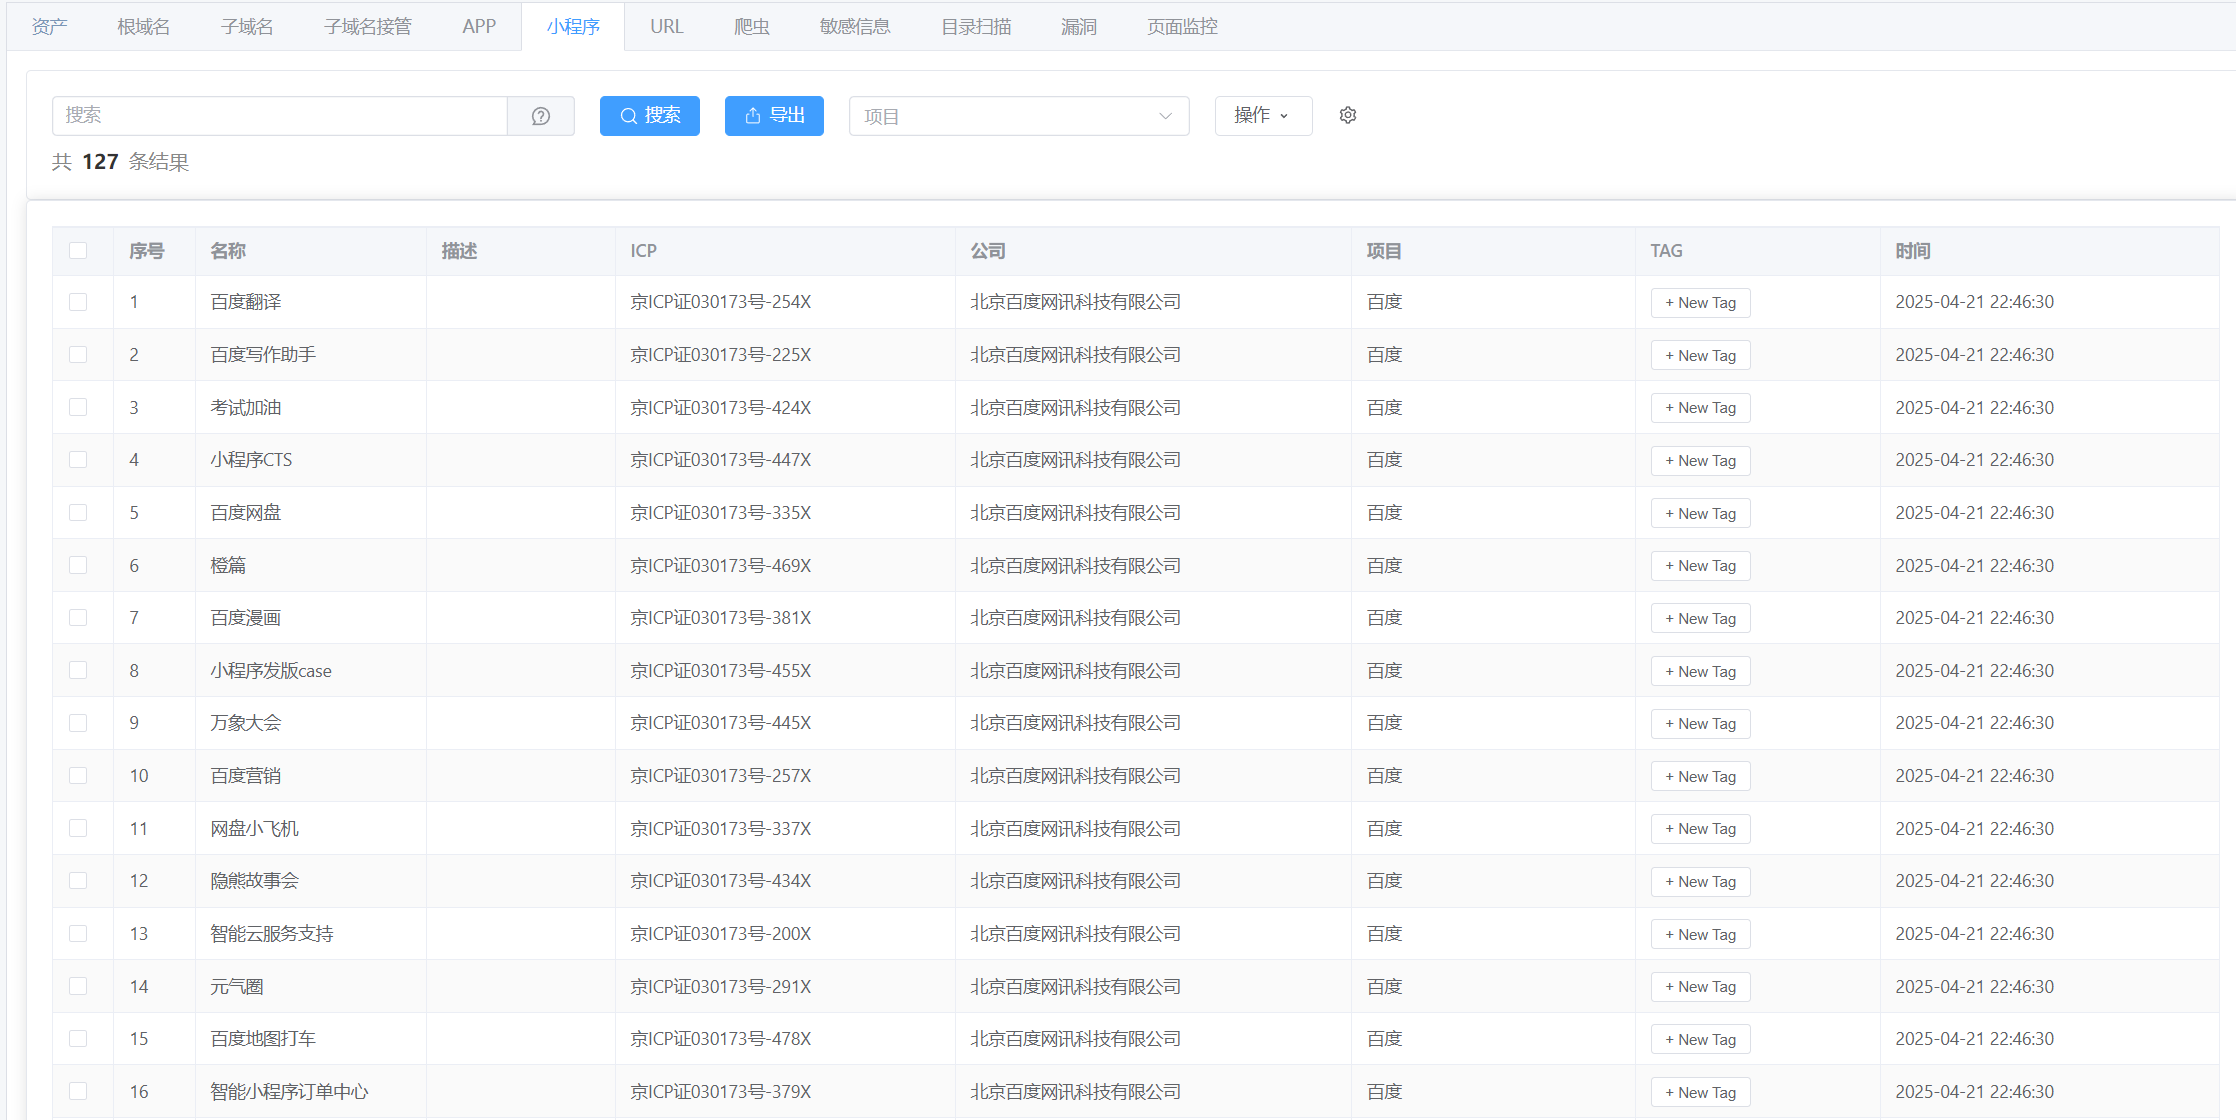
小程序
URL
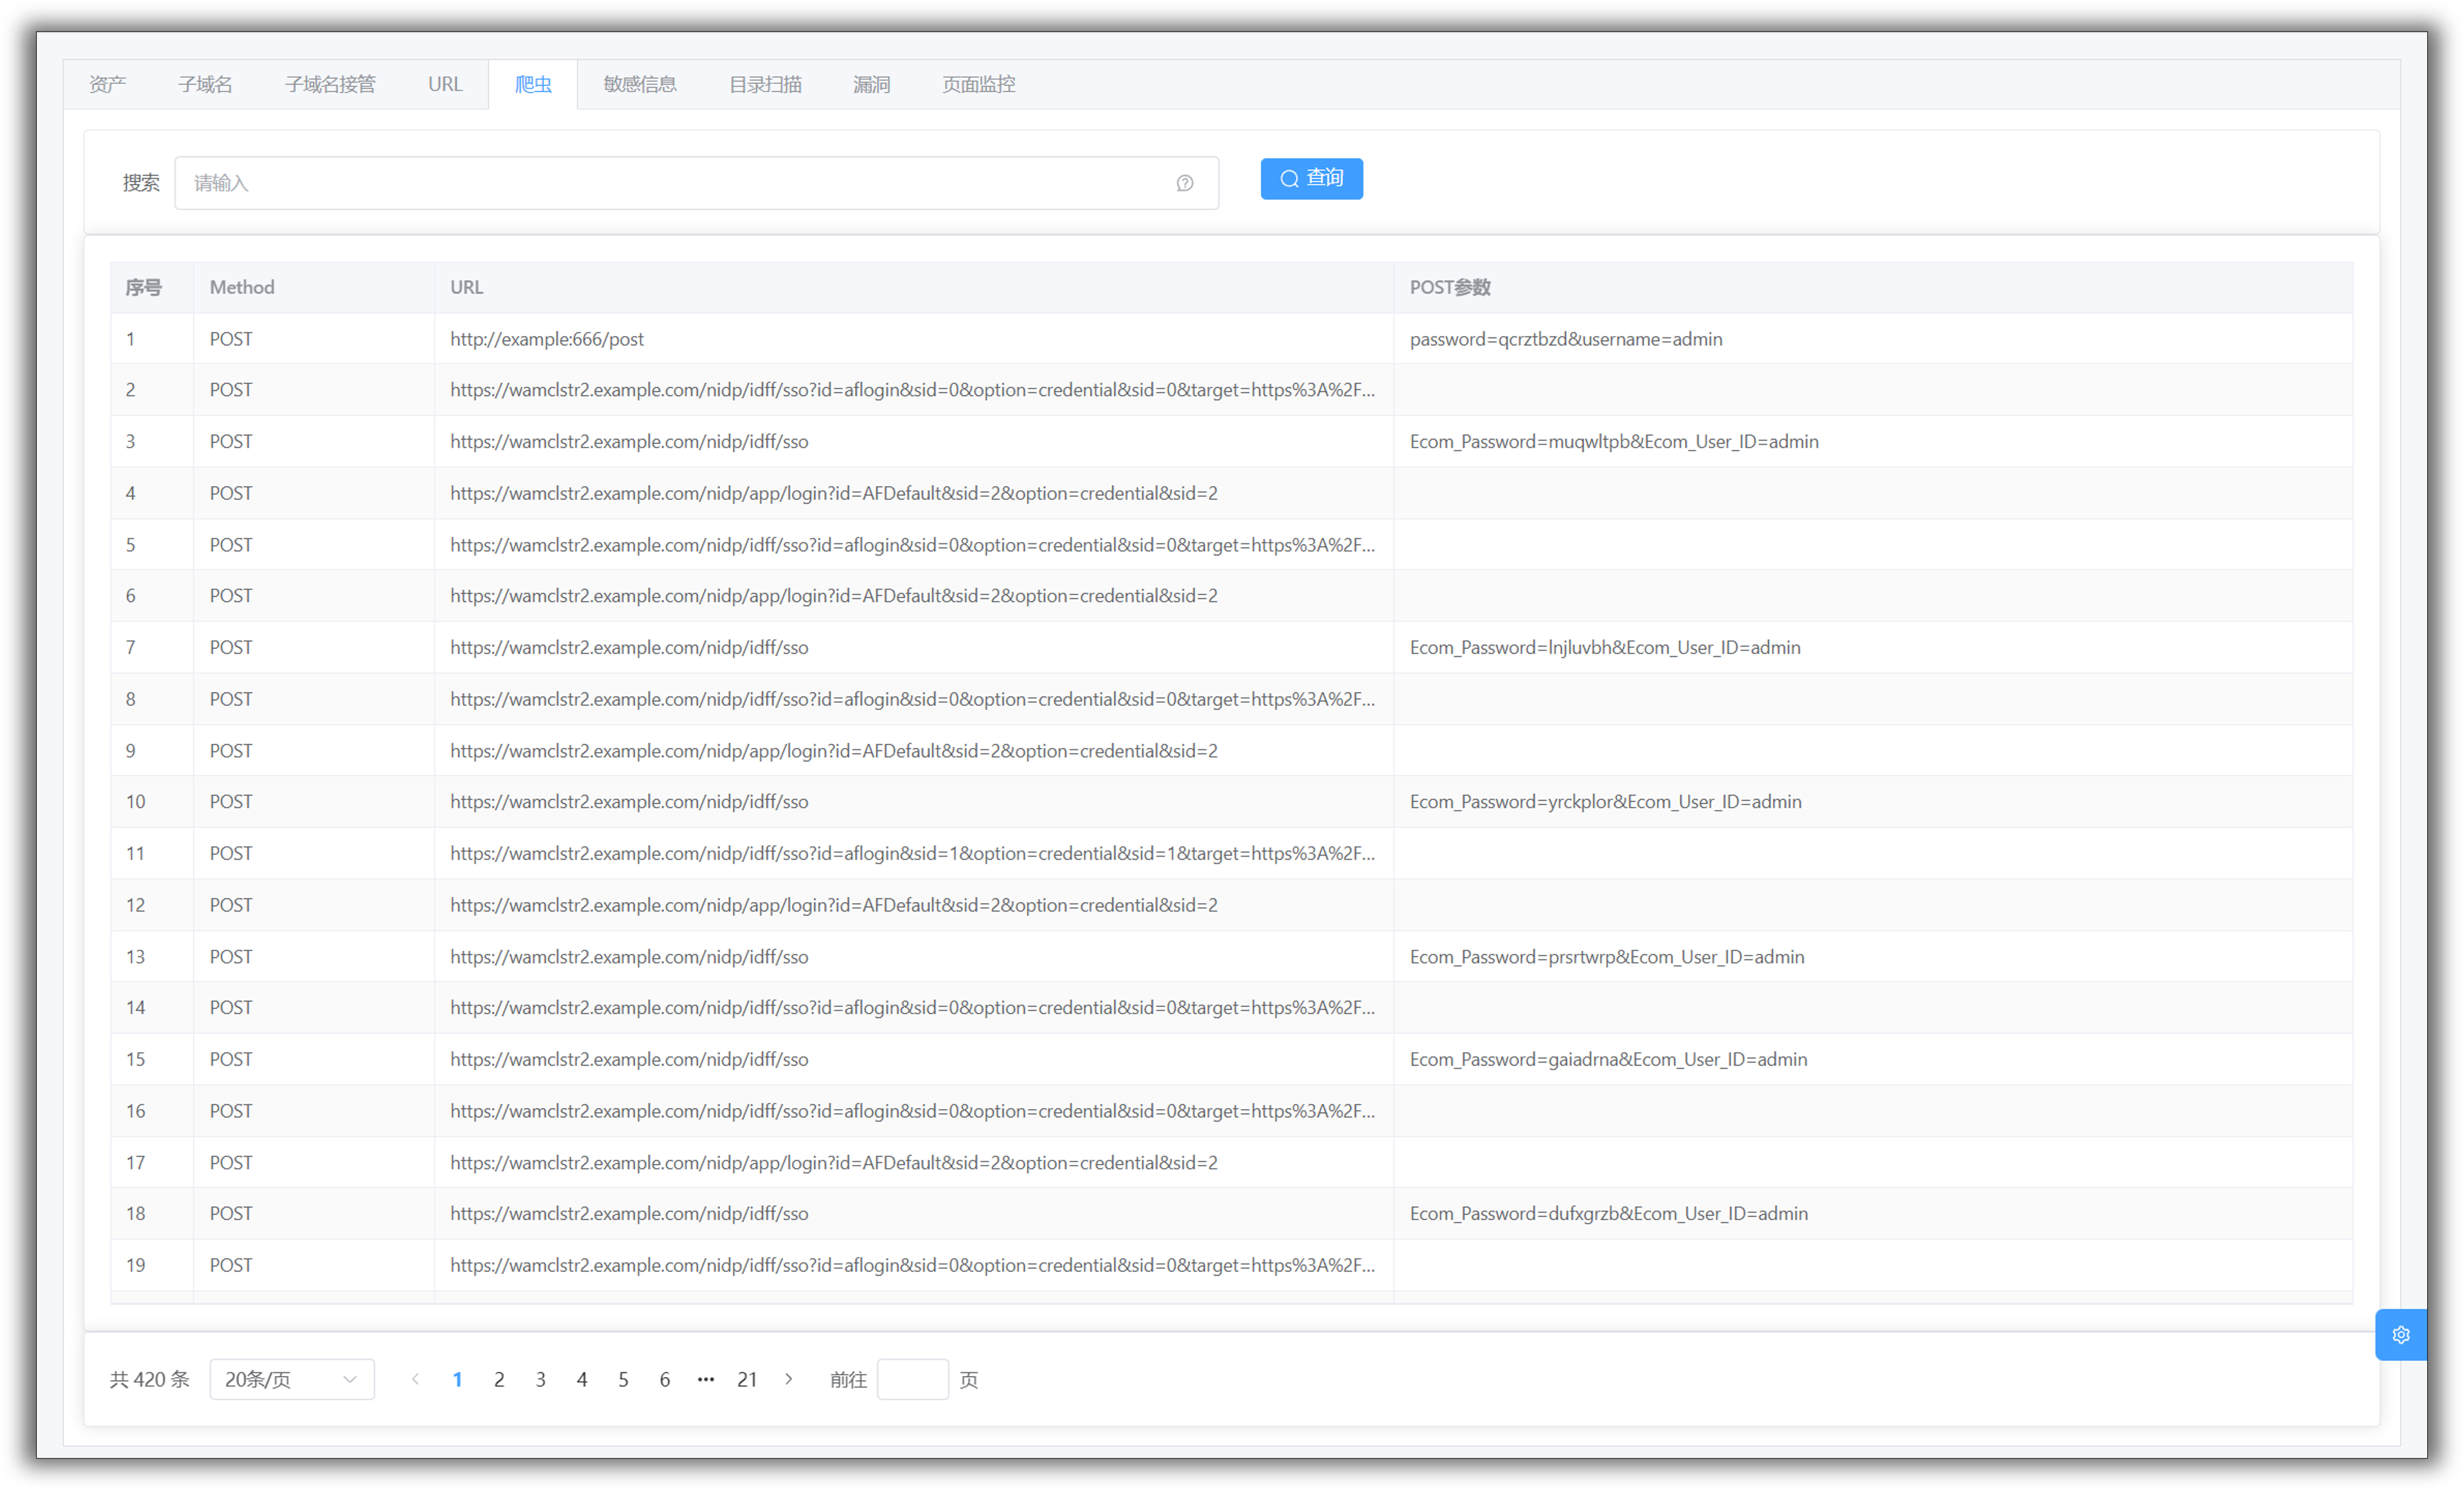
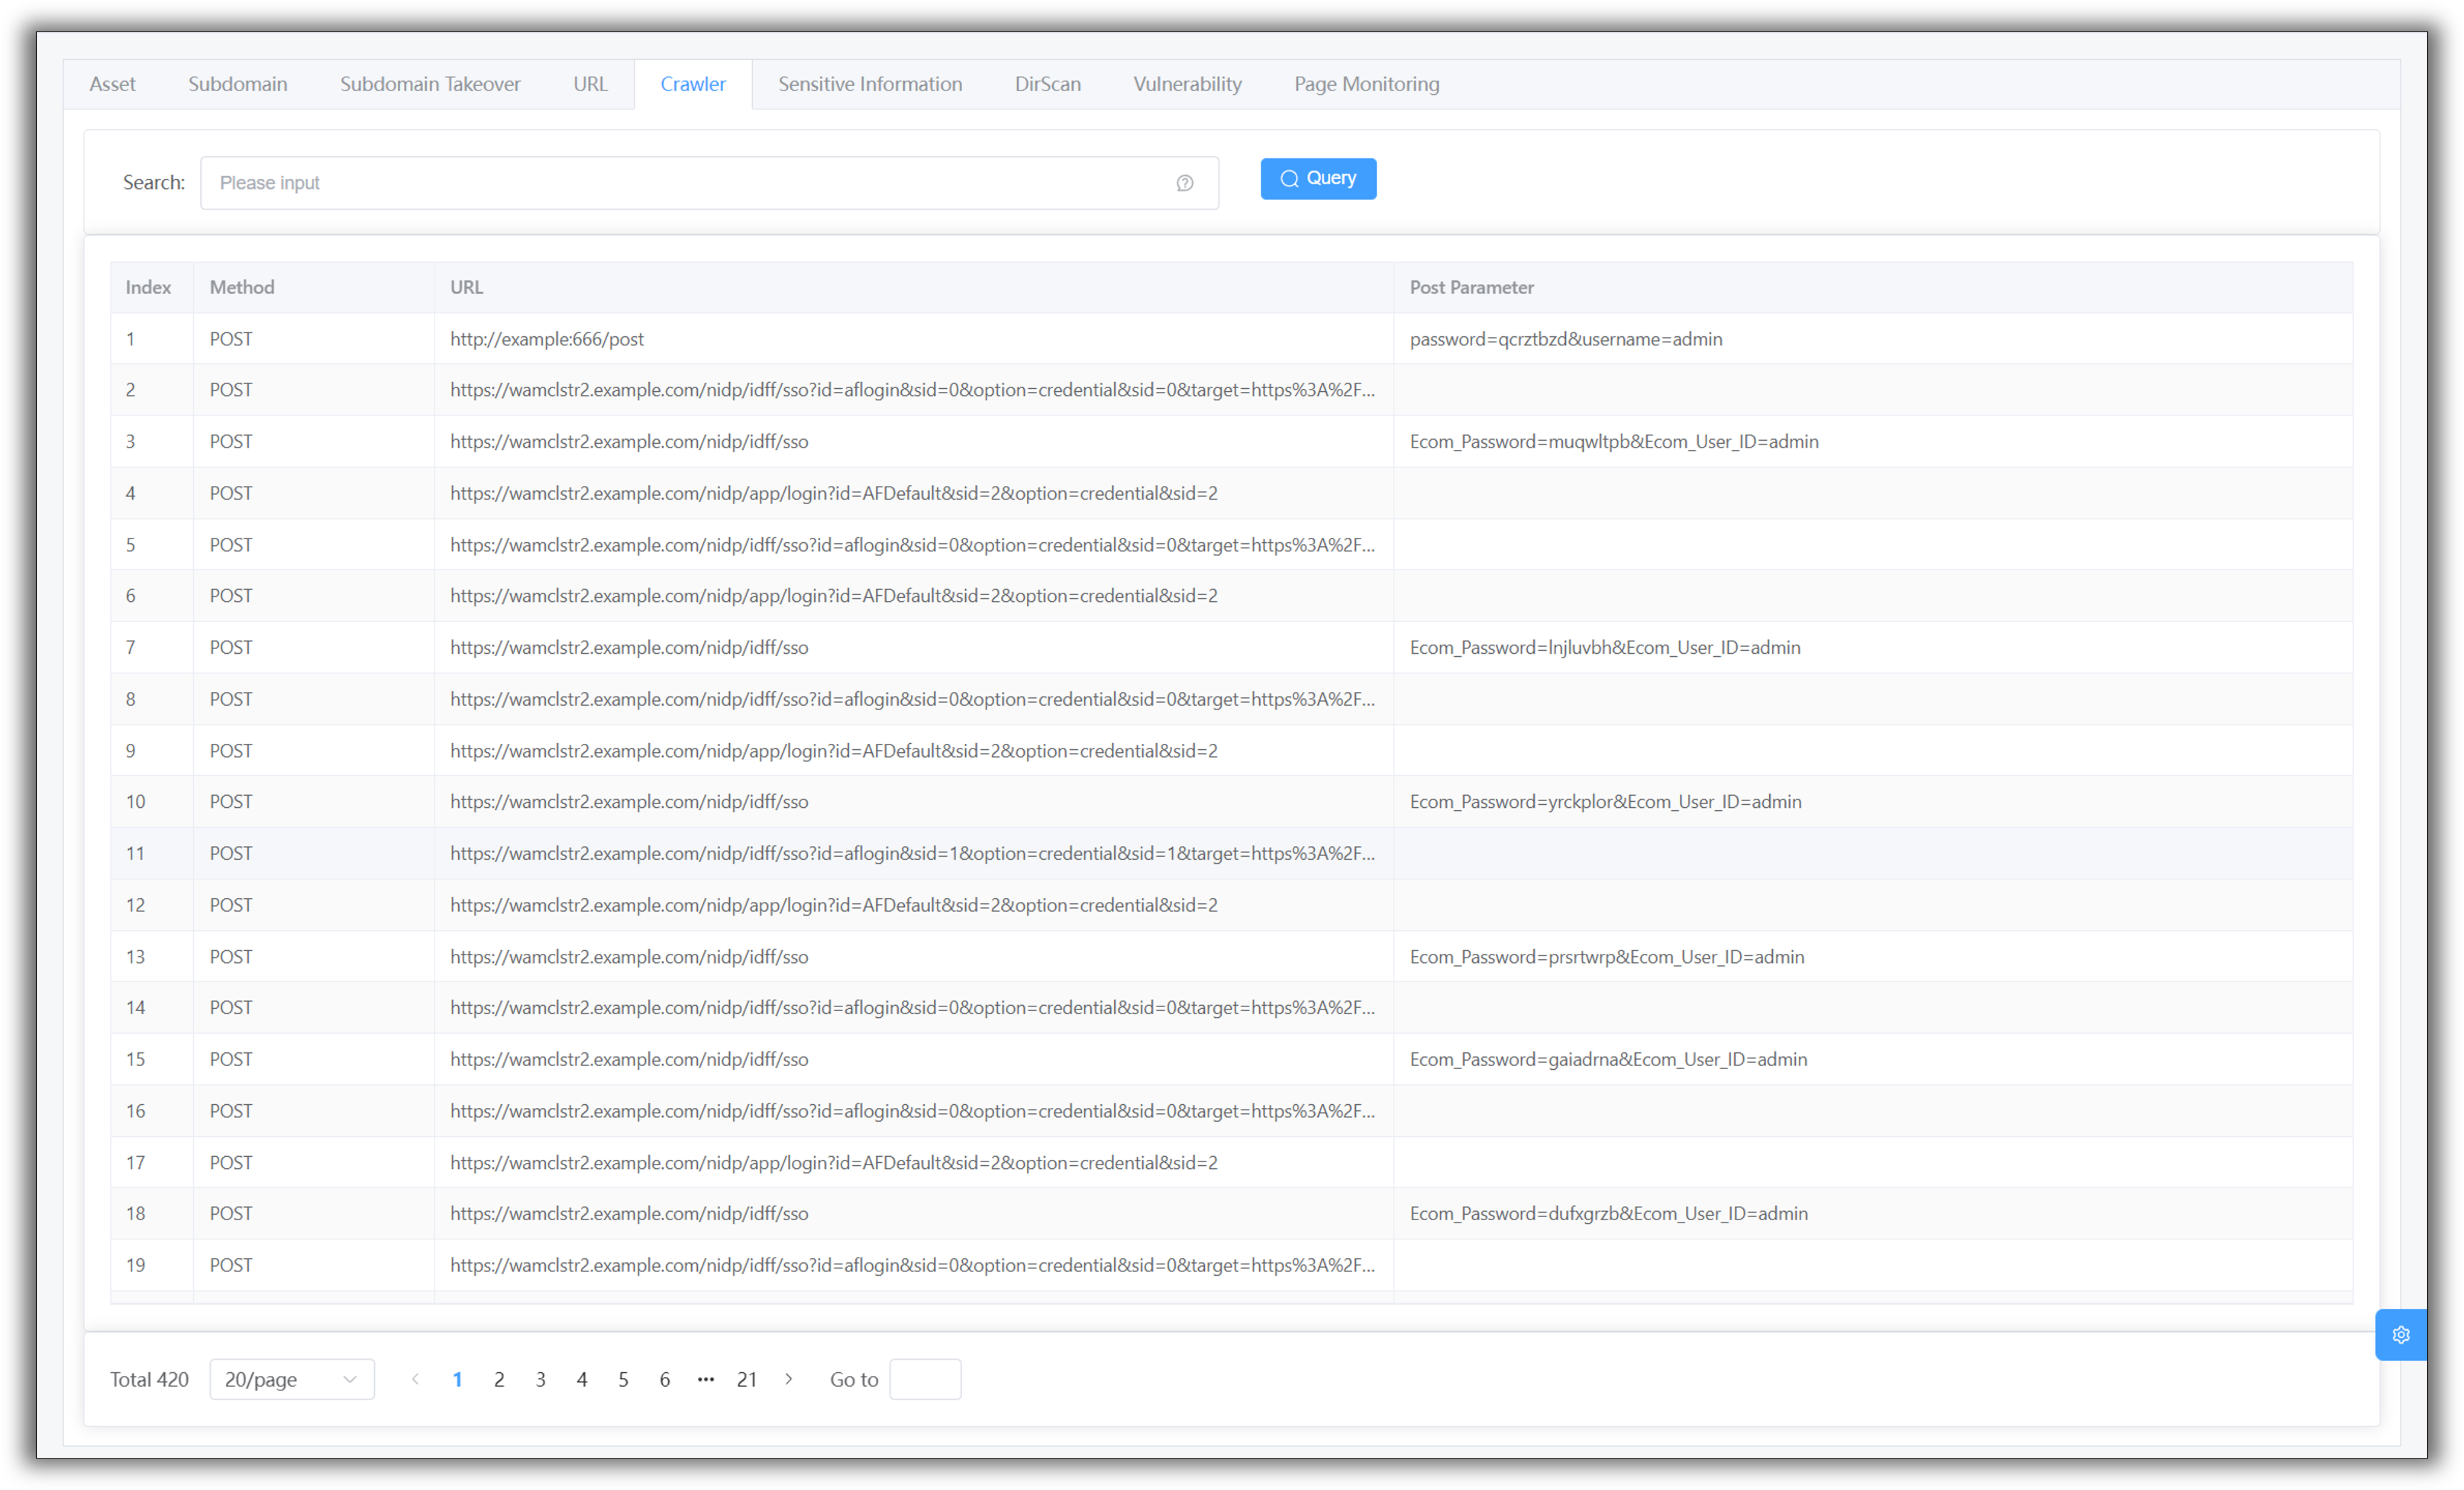
Crawler
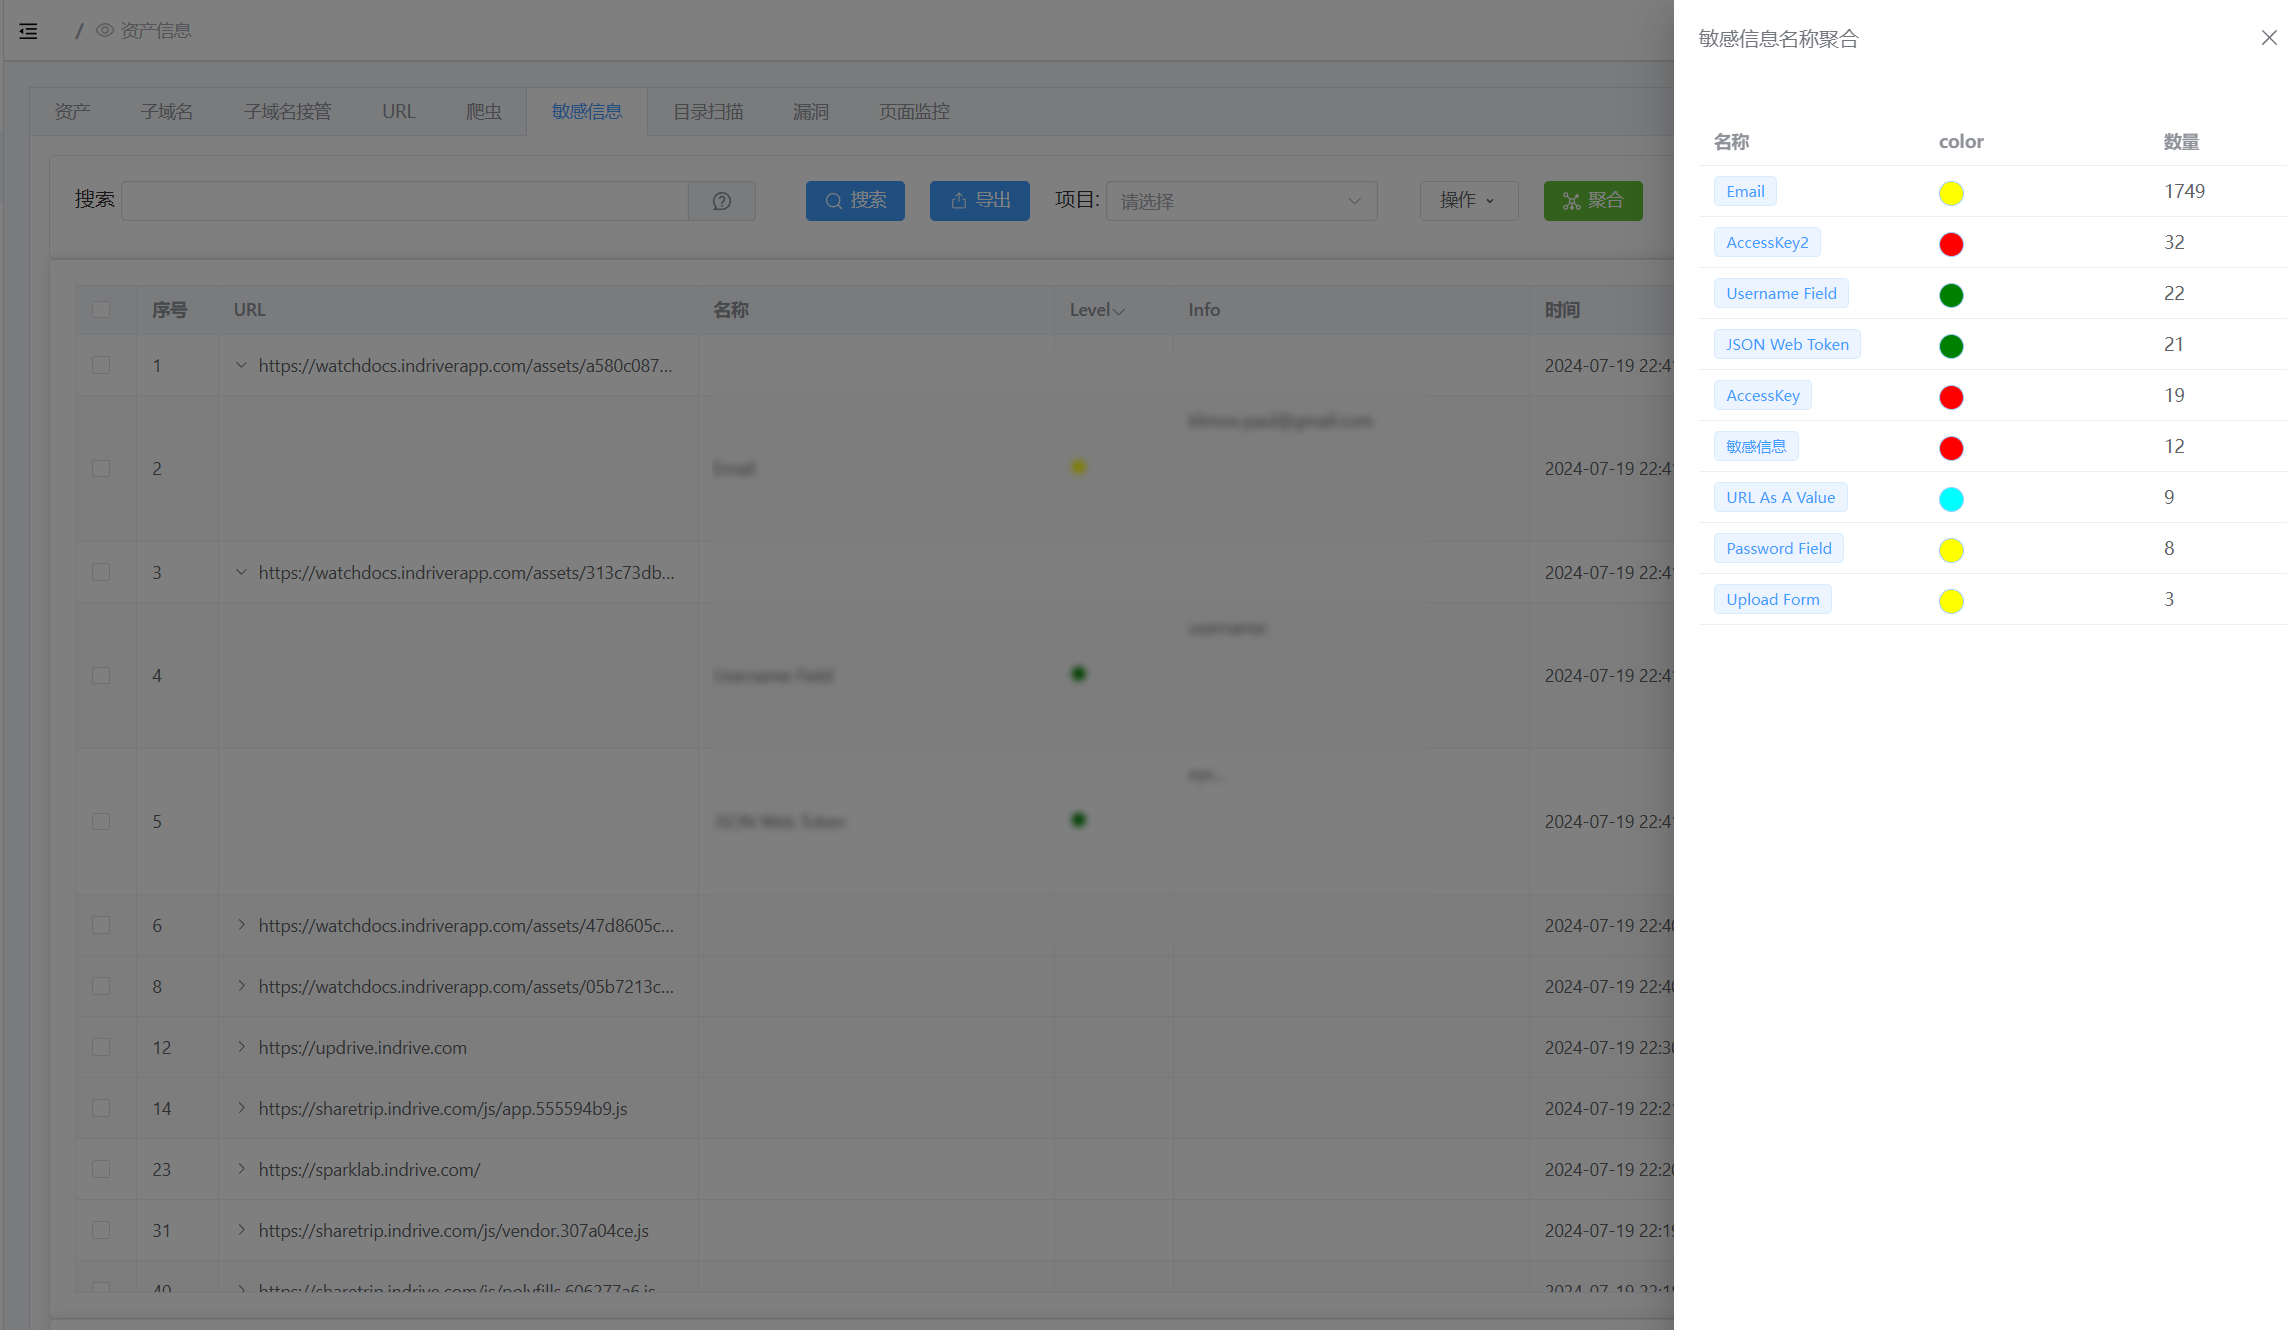
Sensitive Information
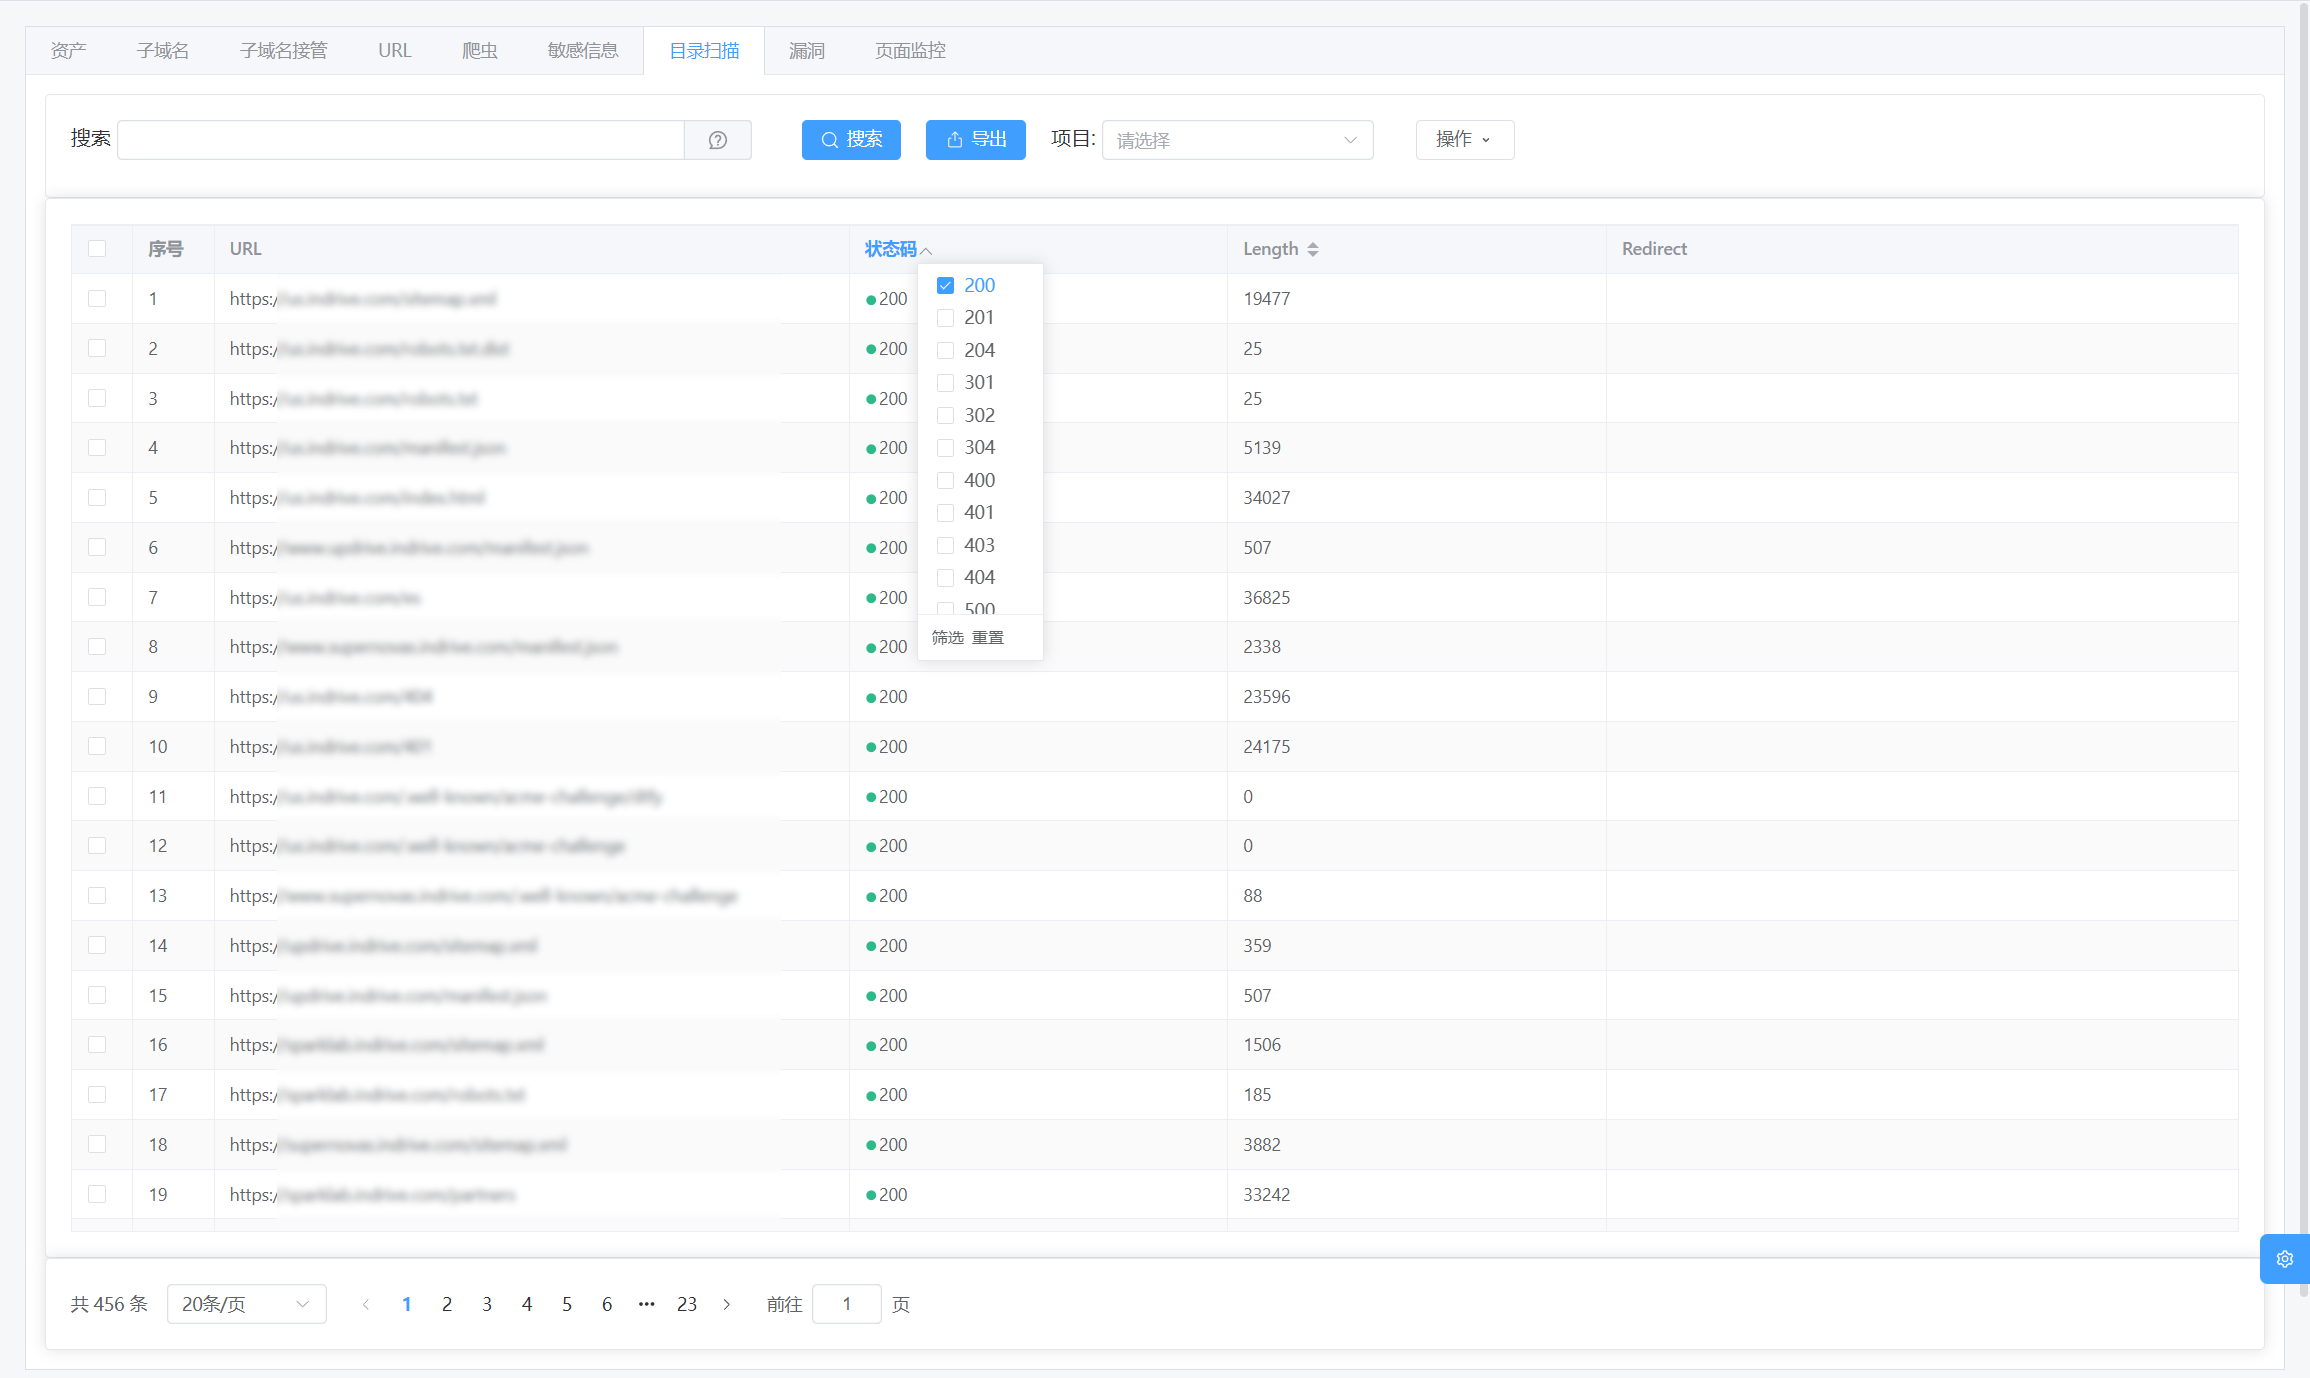
Directory Scanning
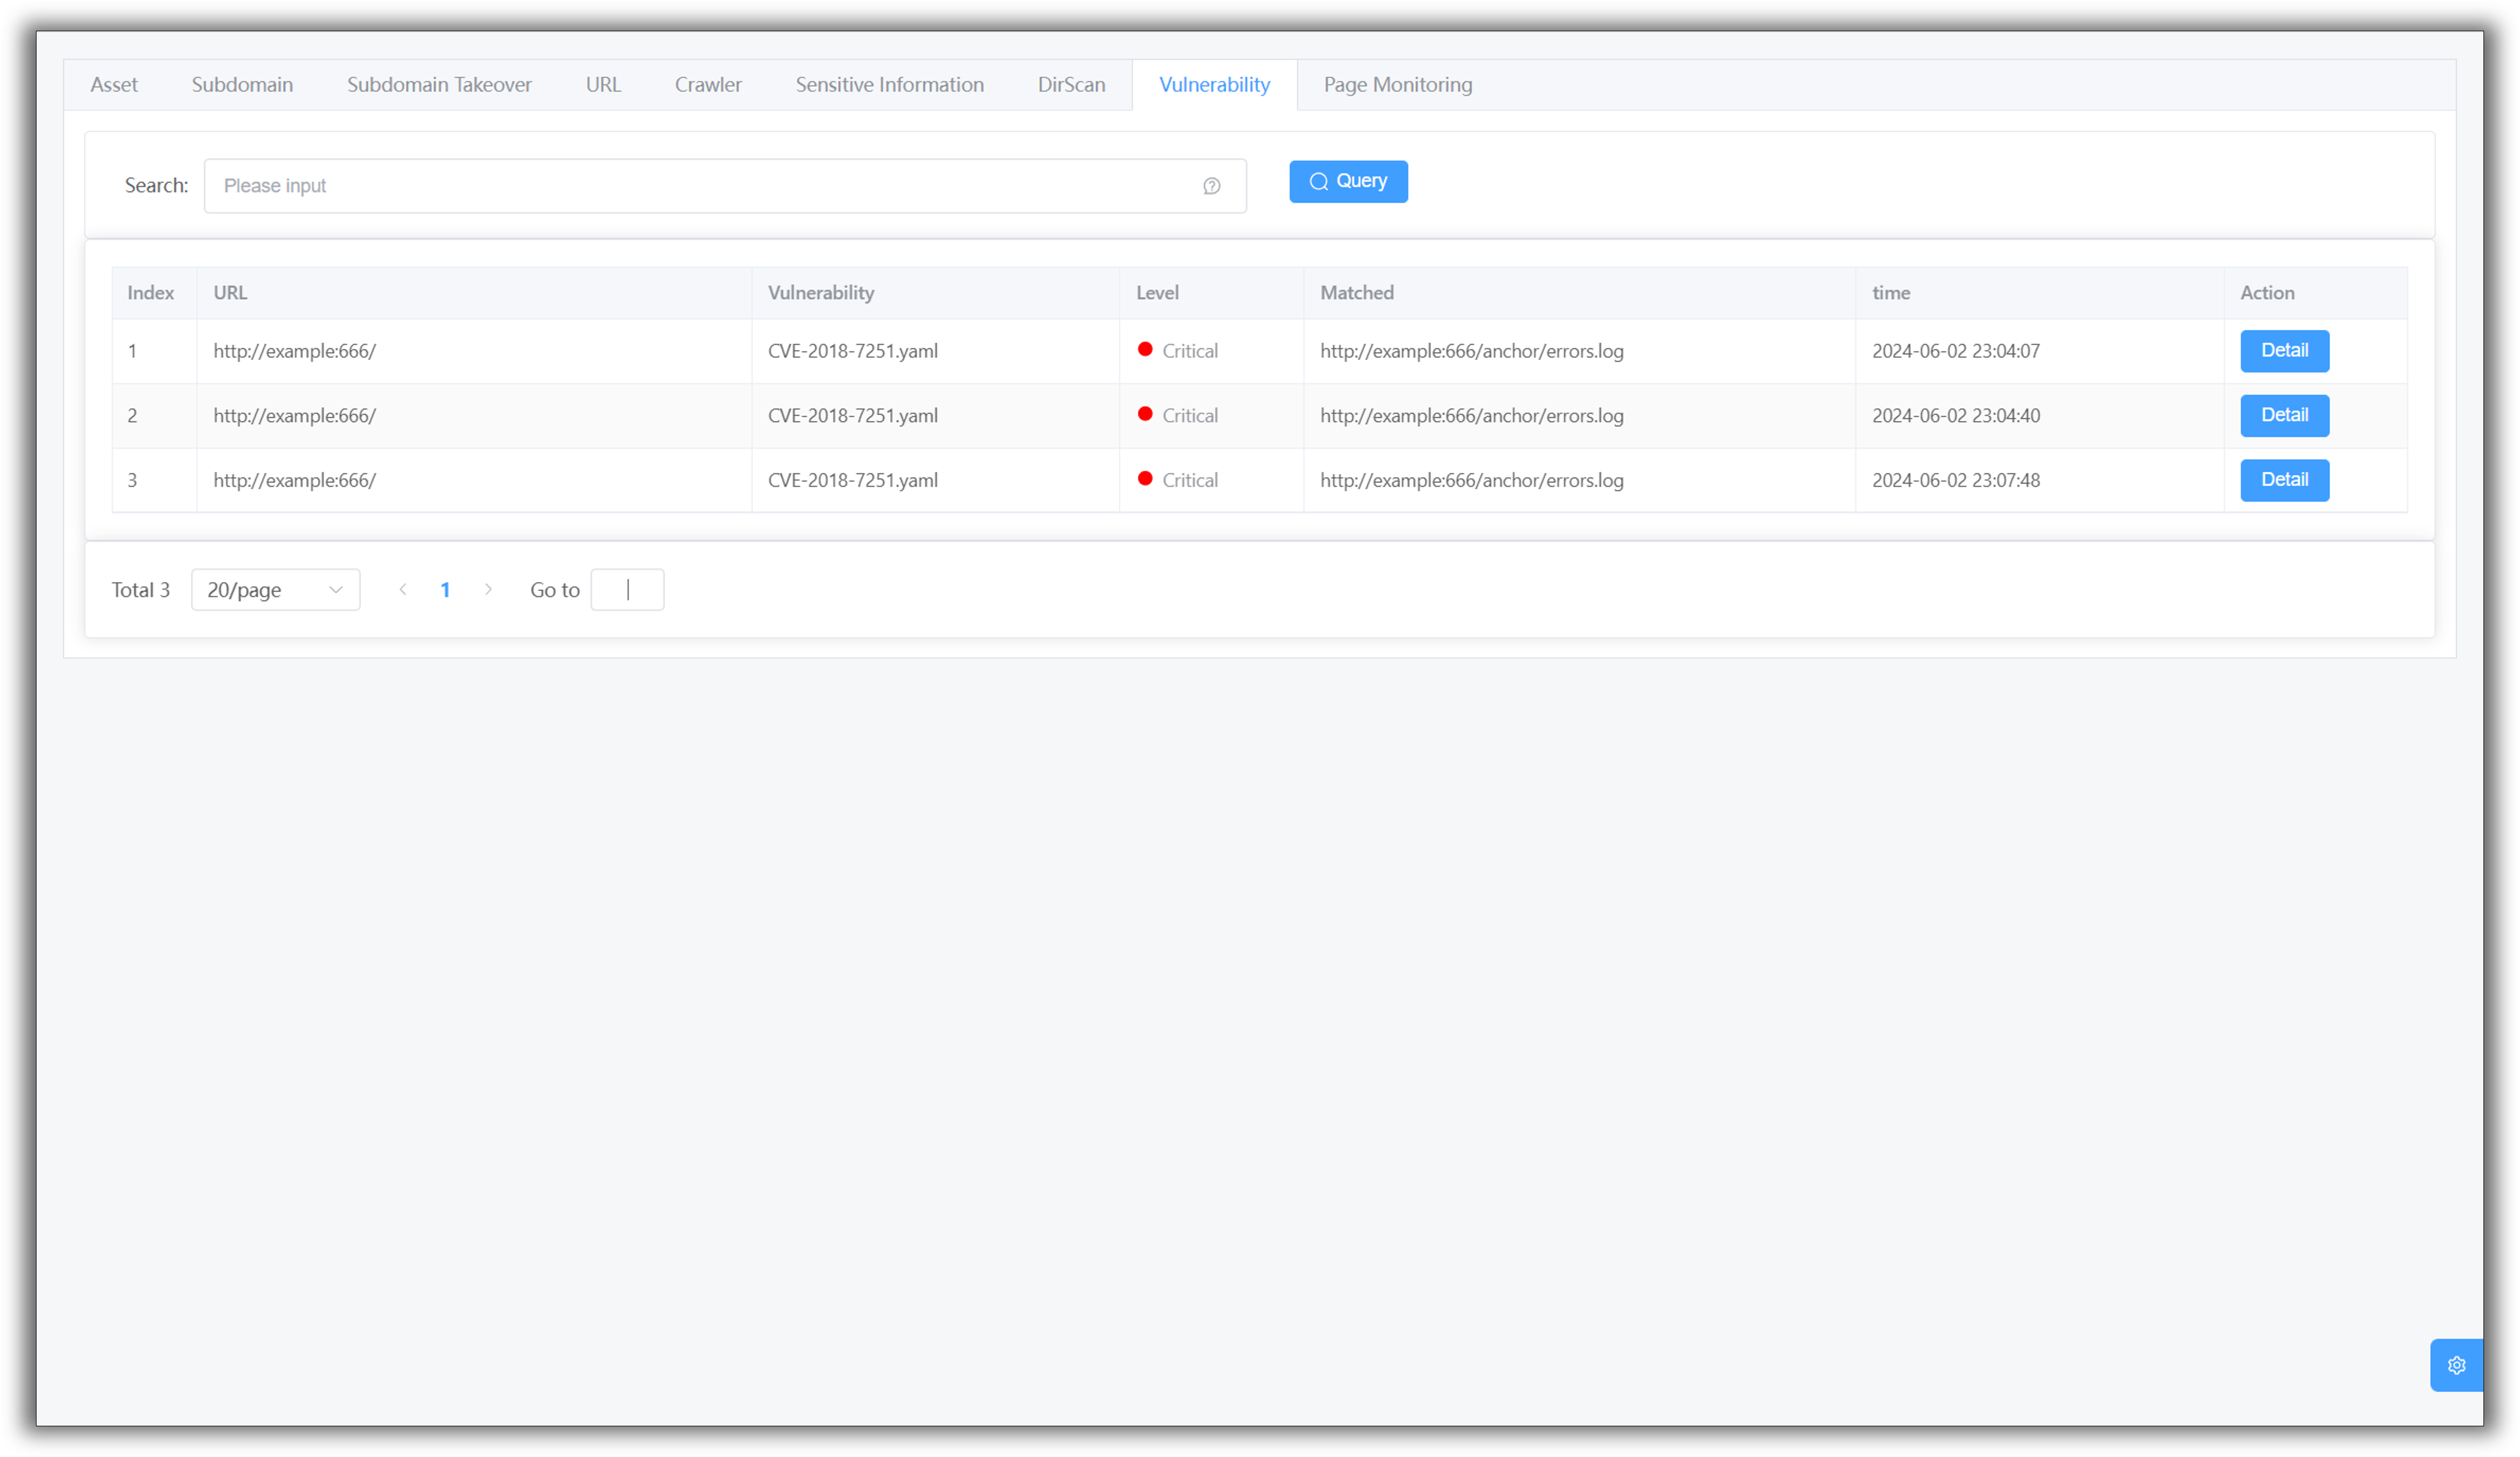
Vulnerabilities
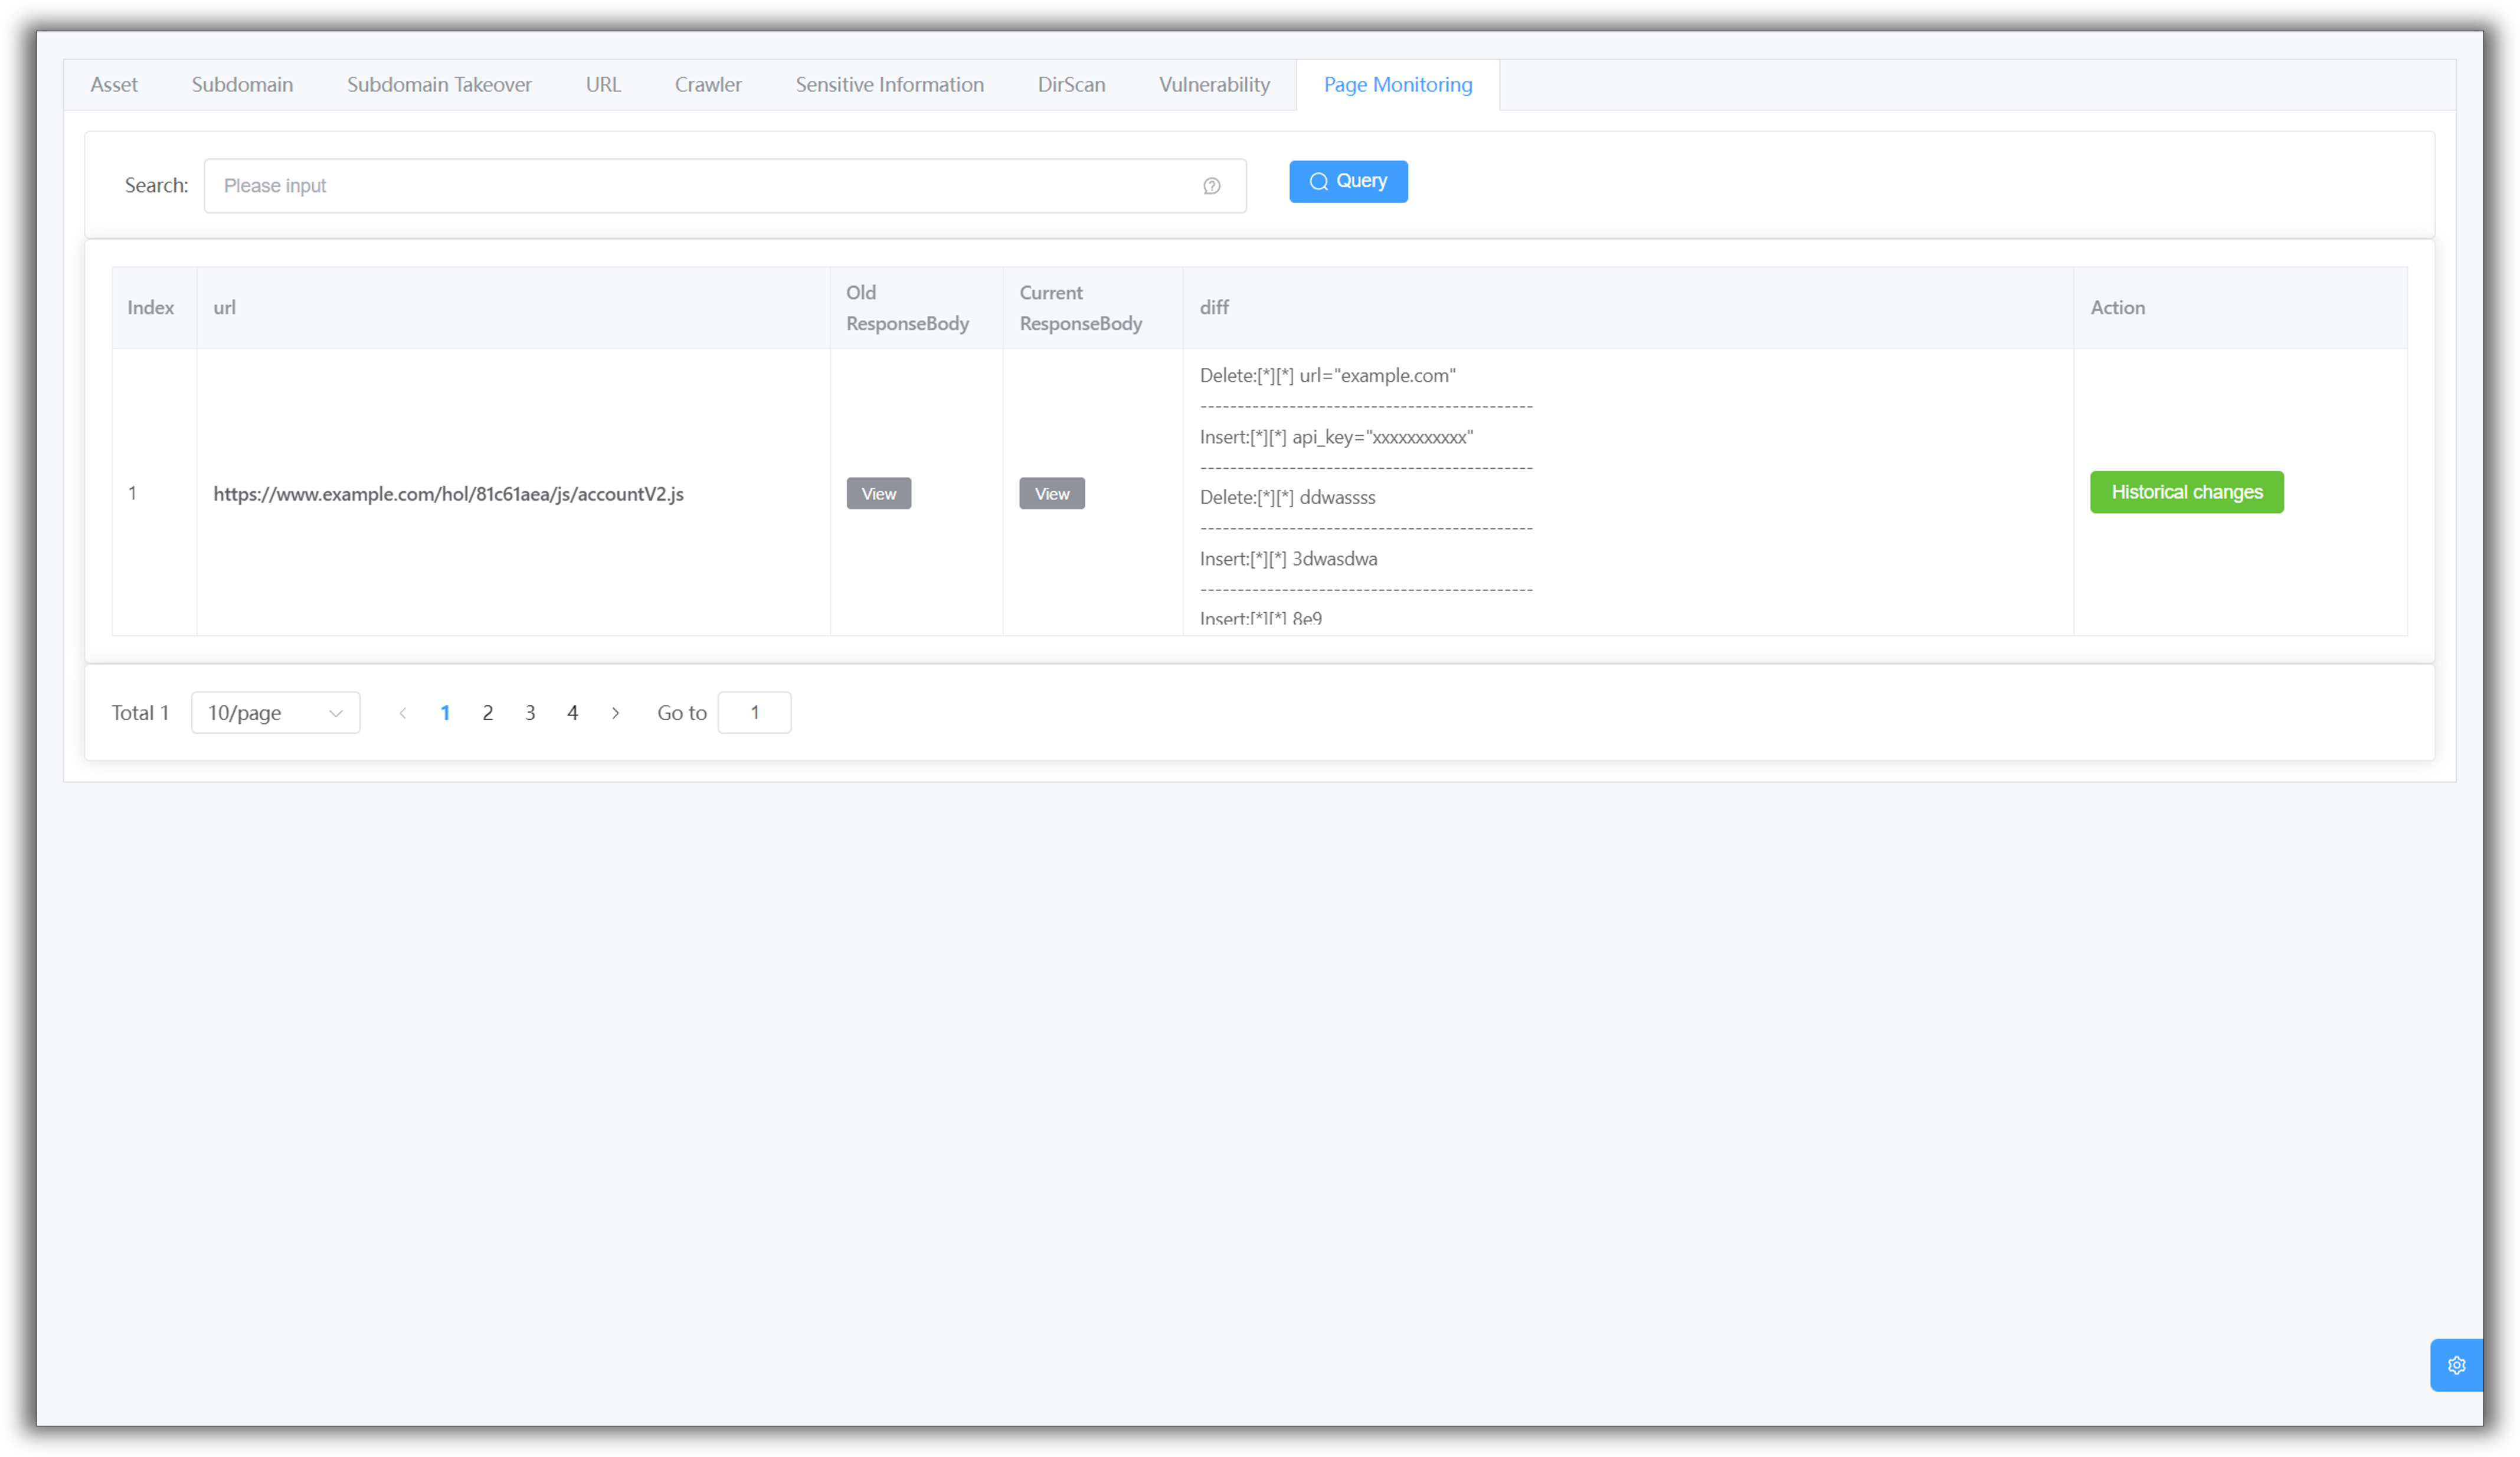
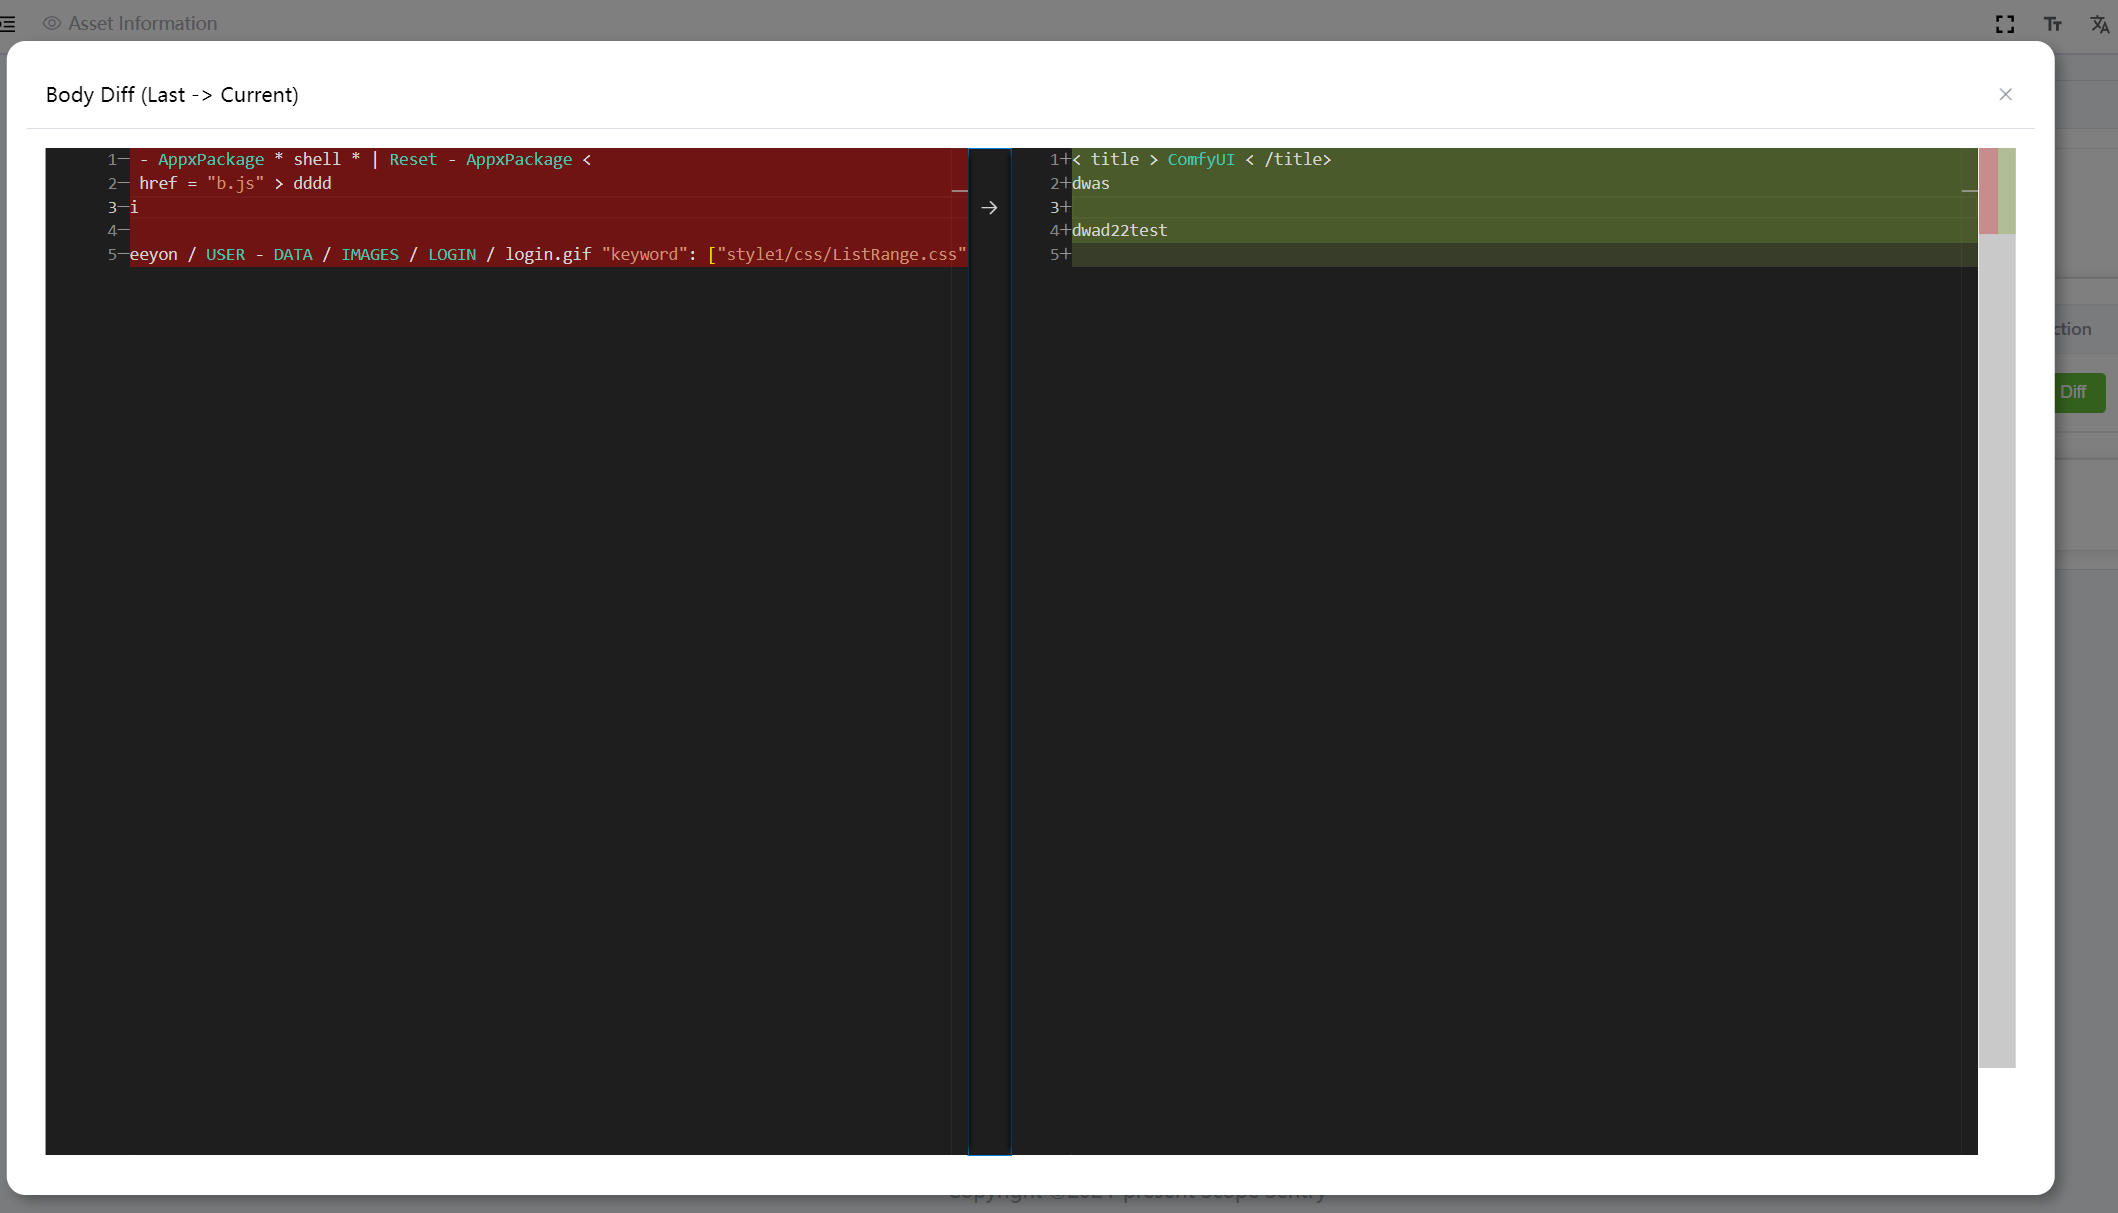
Page Monitoring
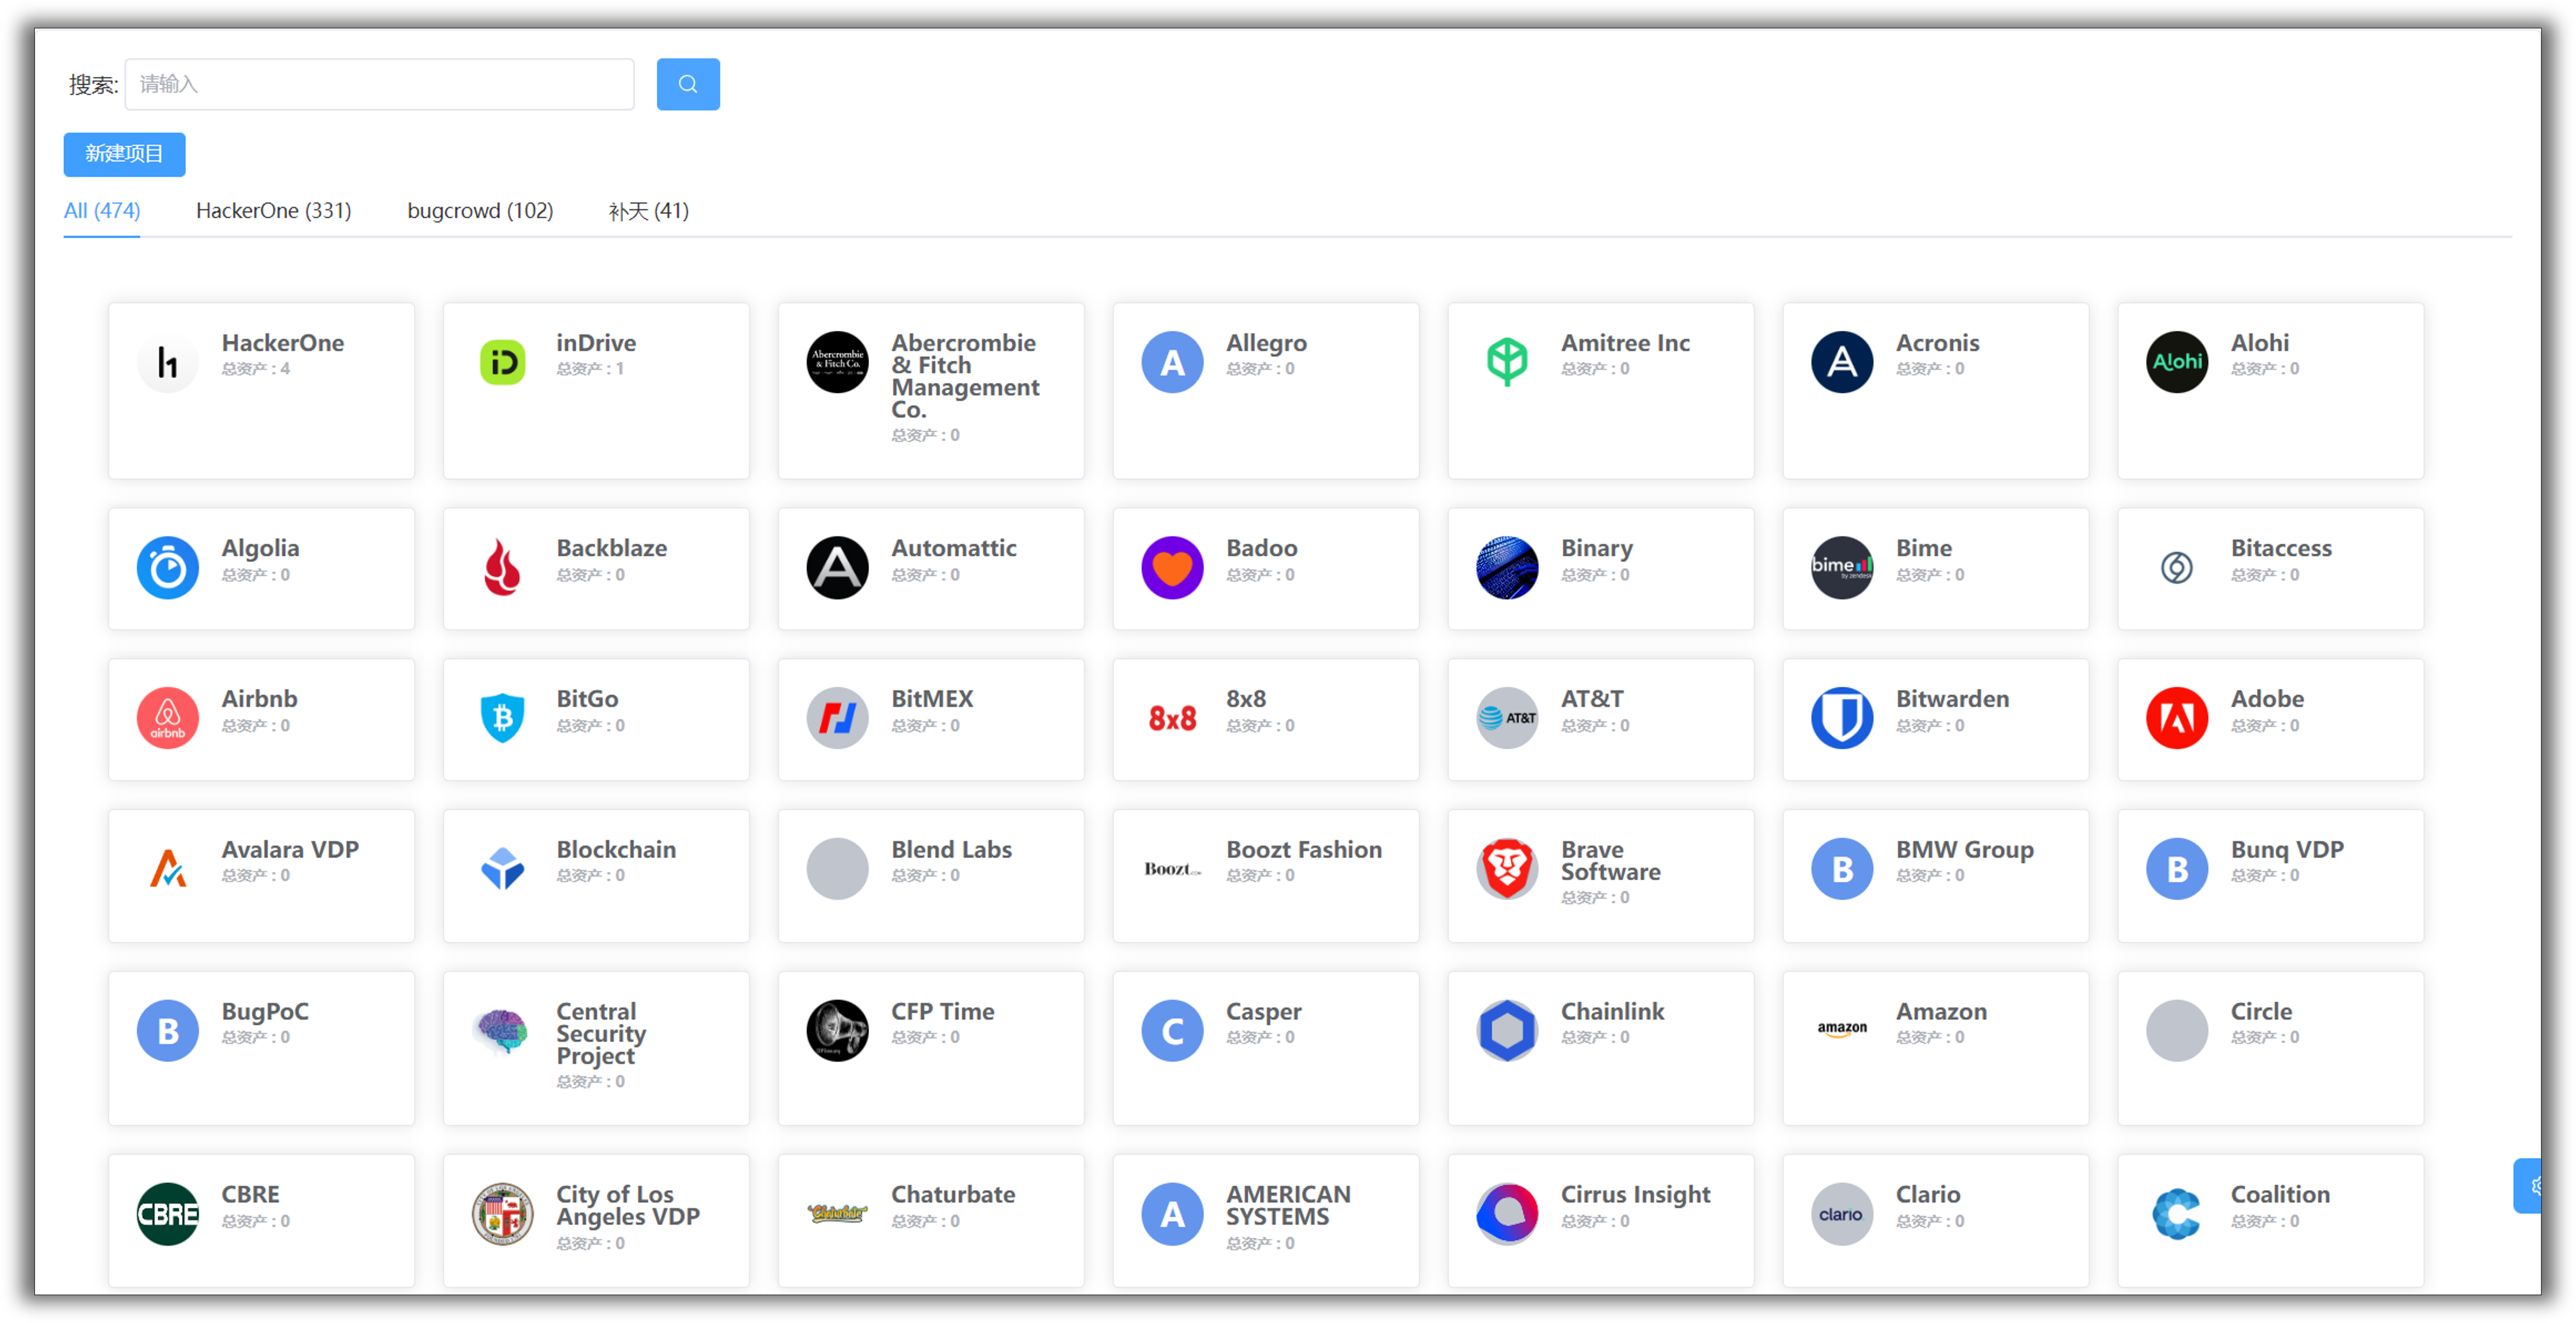
Projects
Project asset aggregation
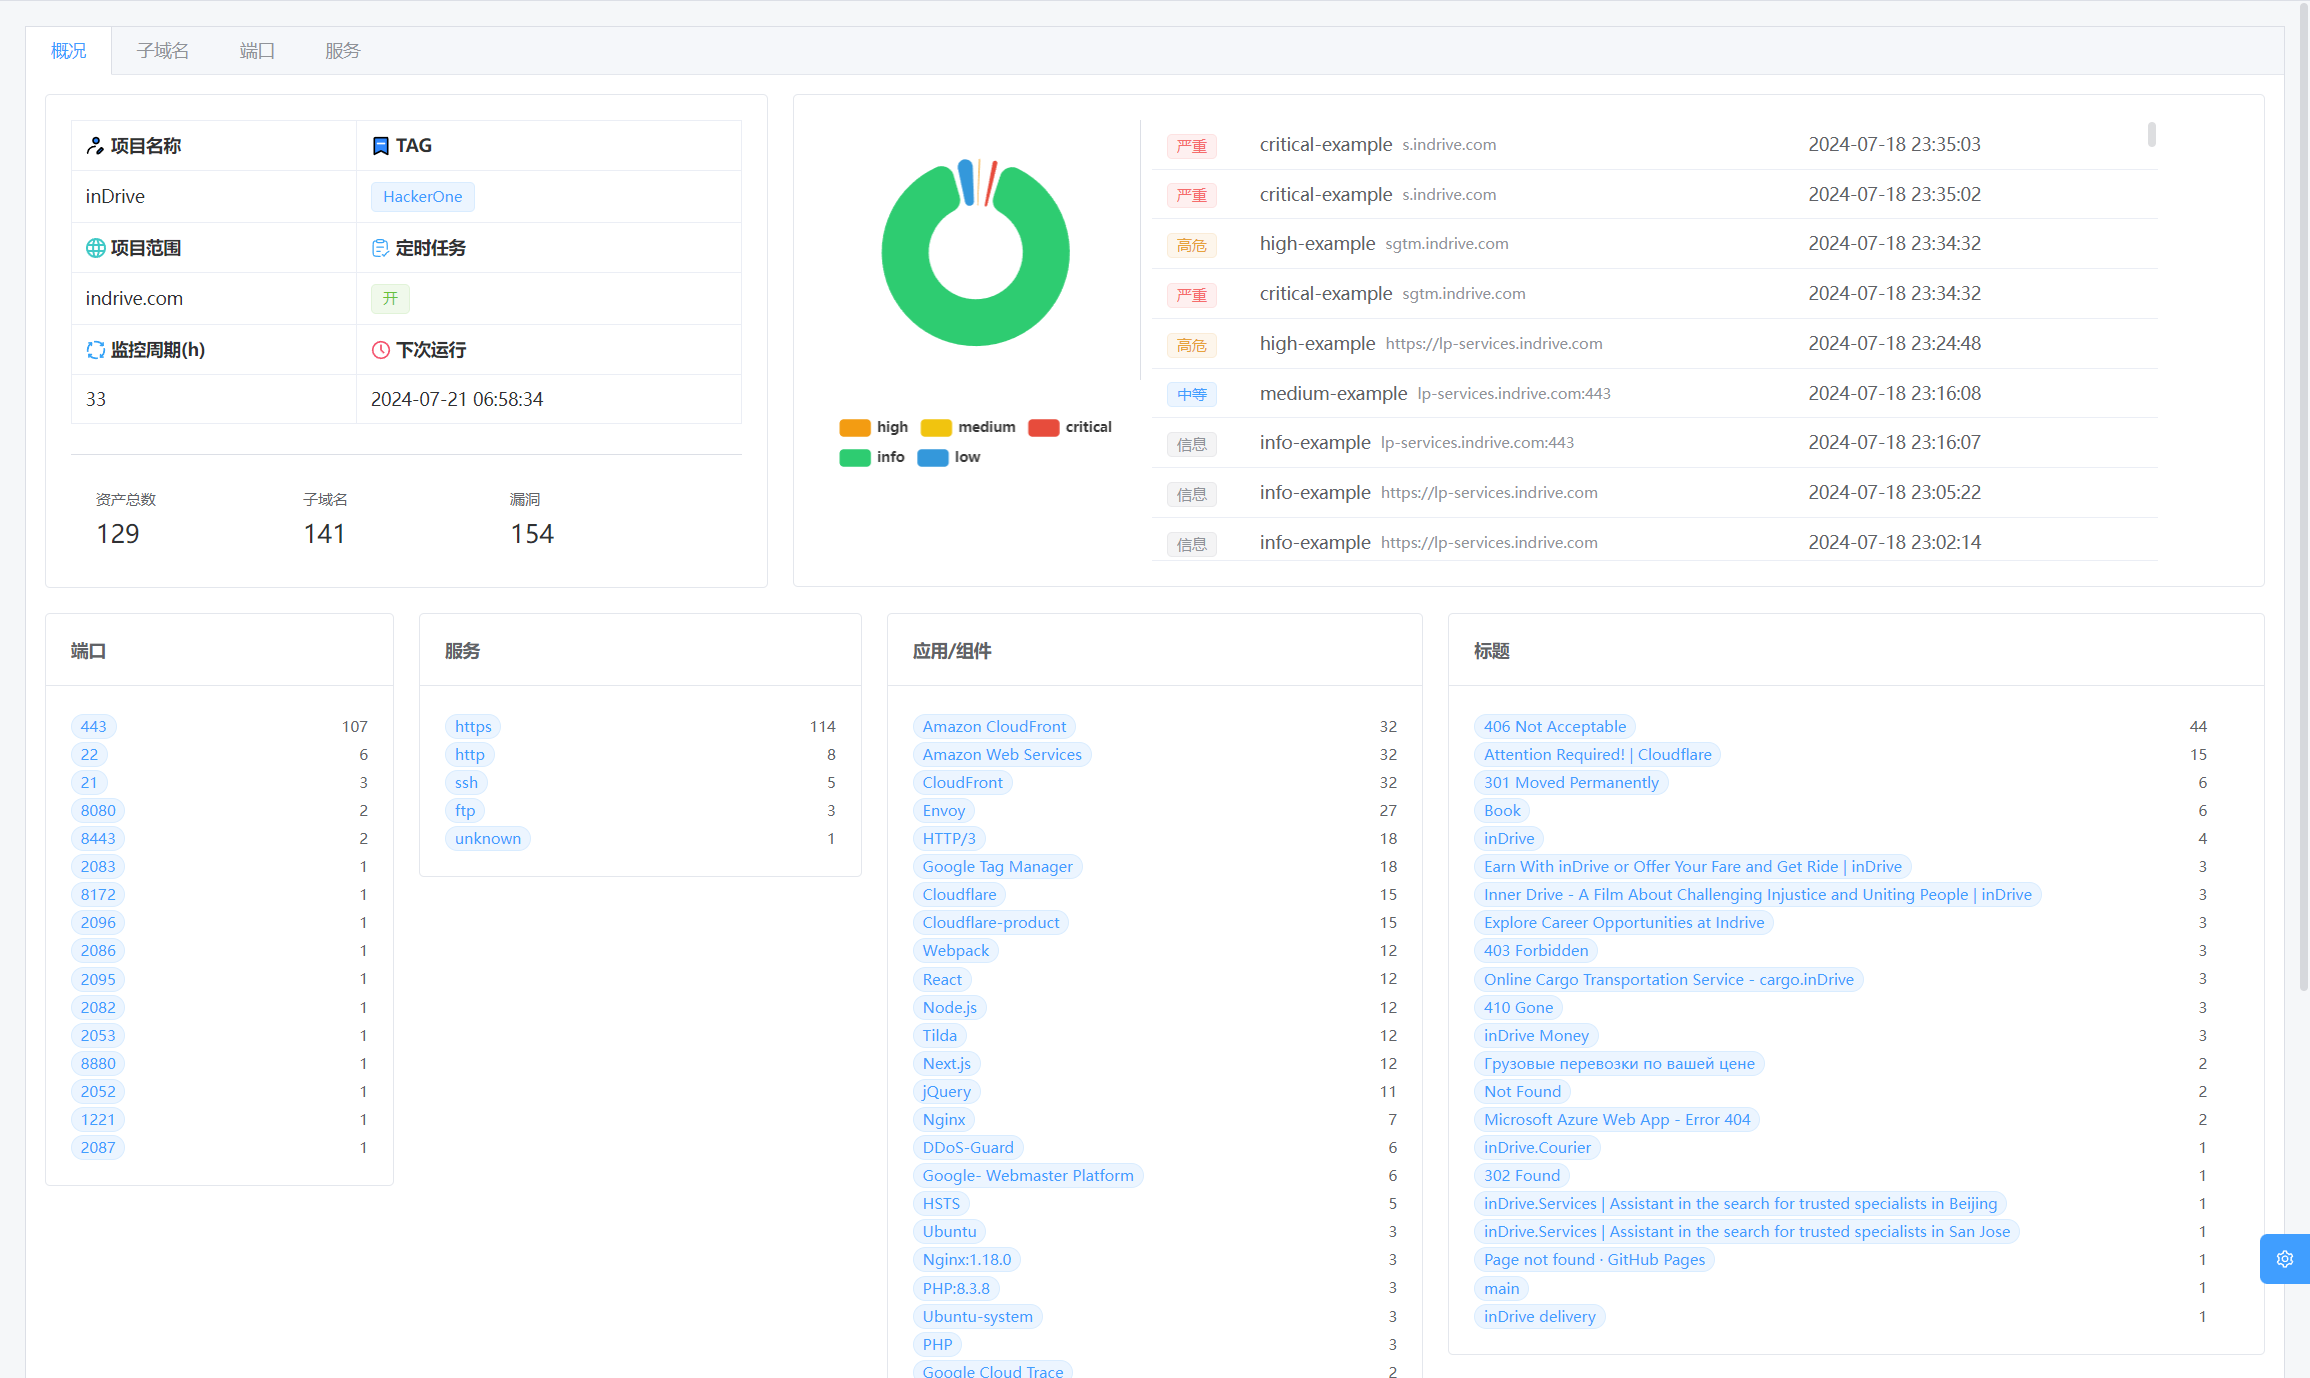
Panel - Overview
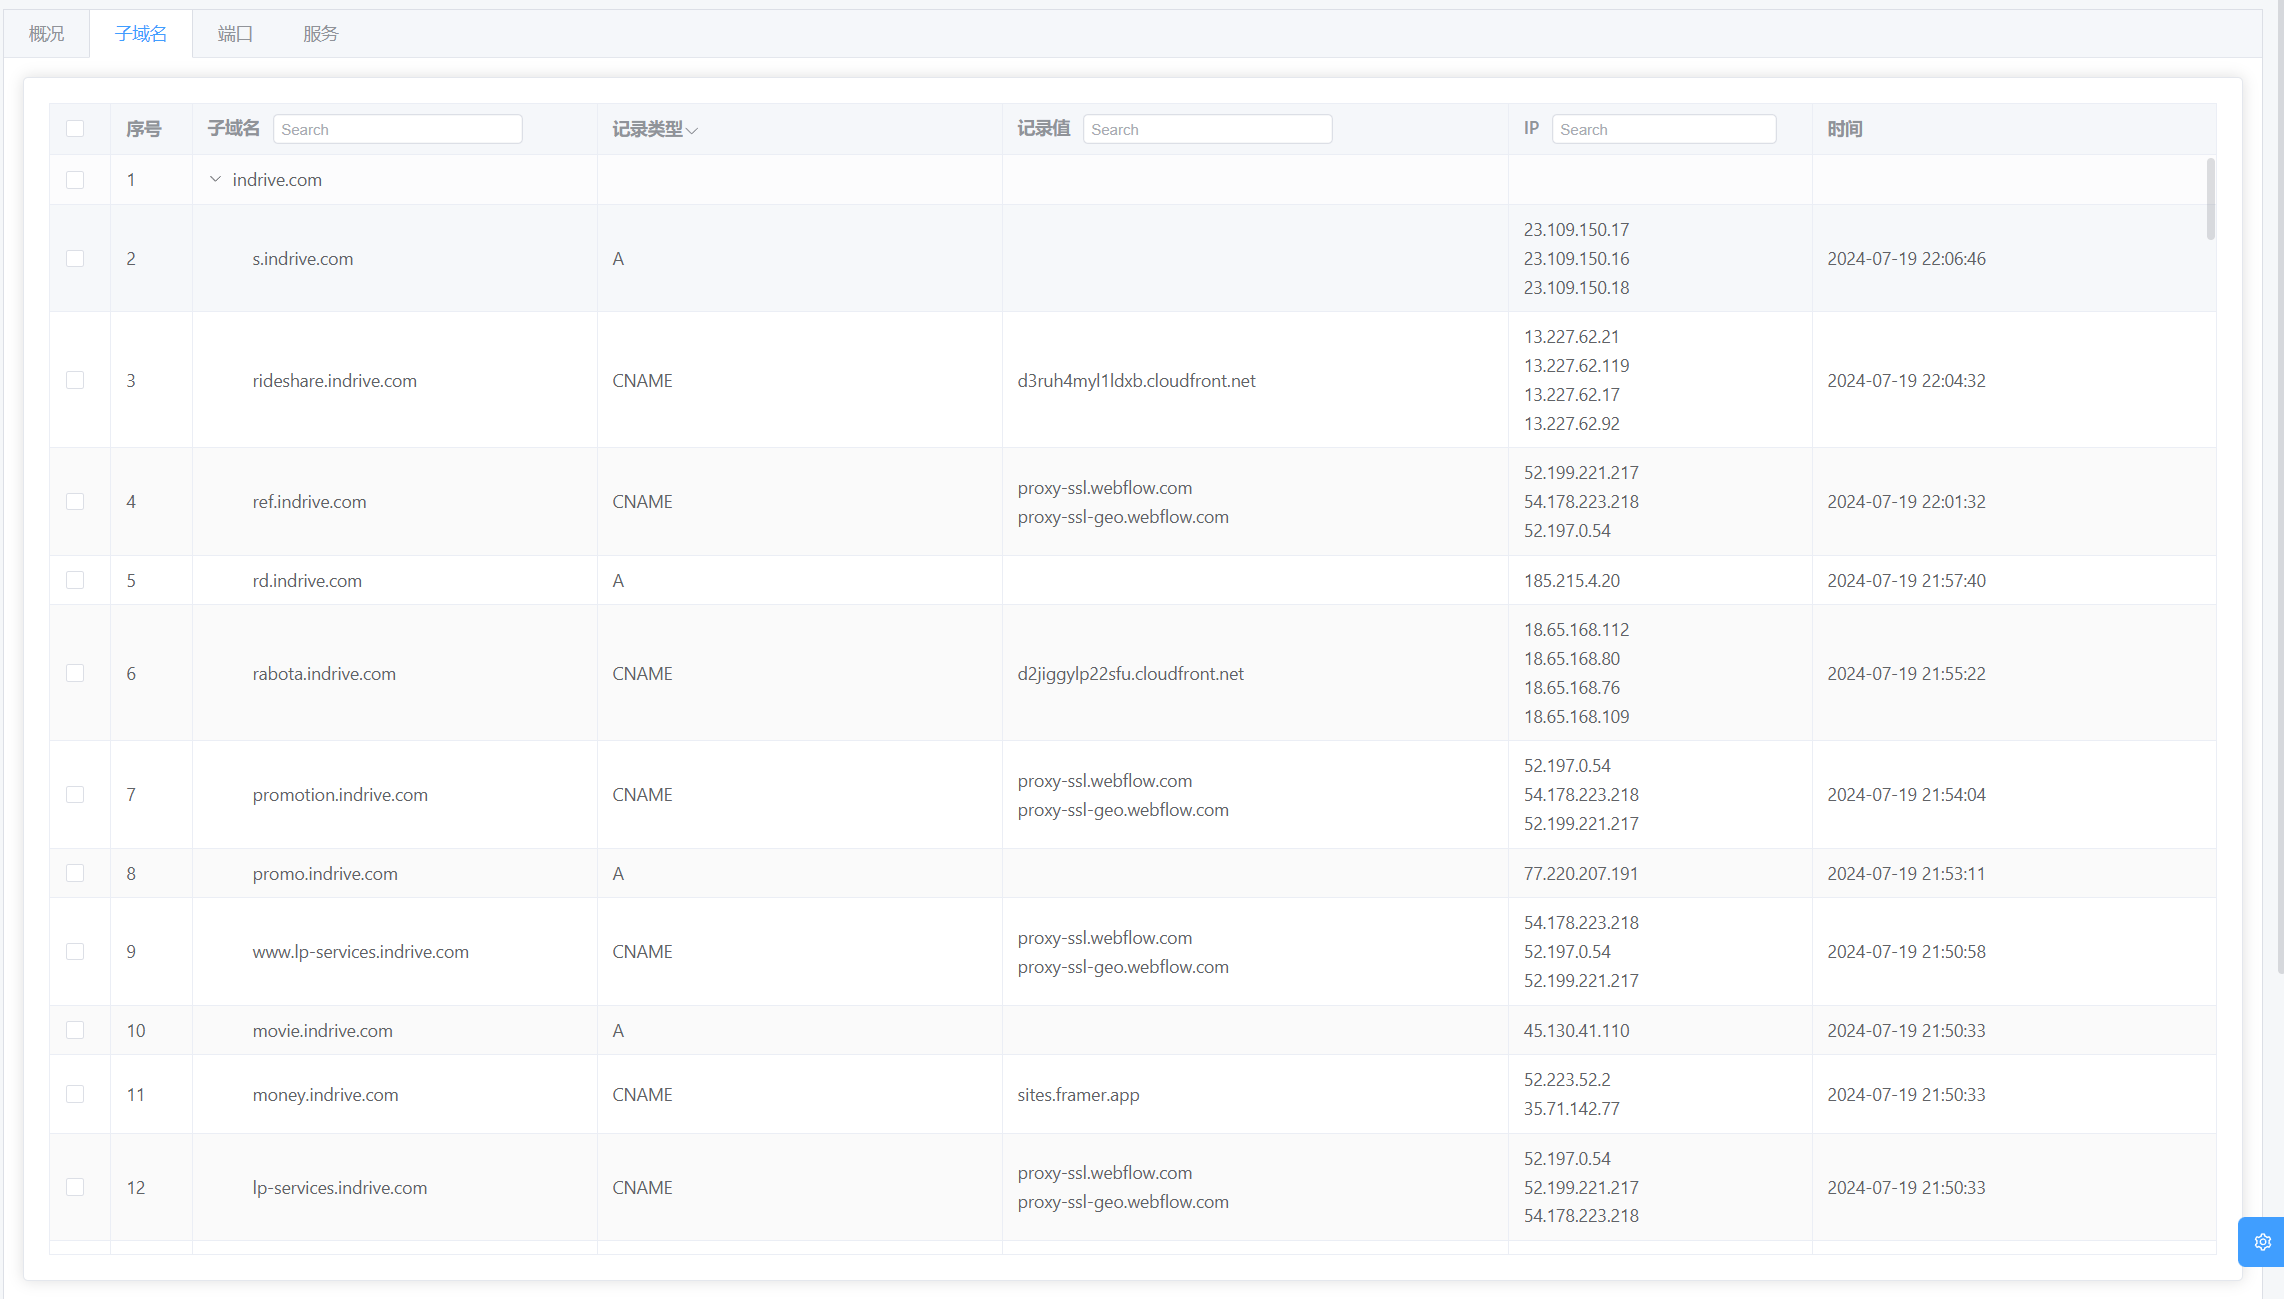
Subdomains
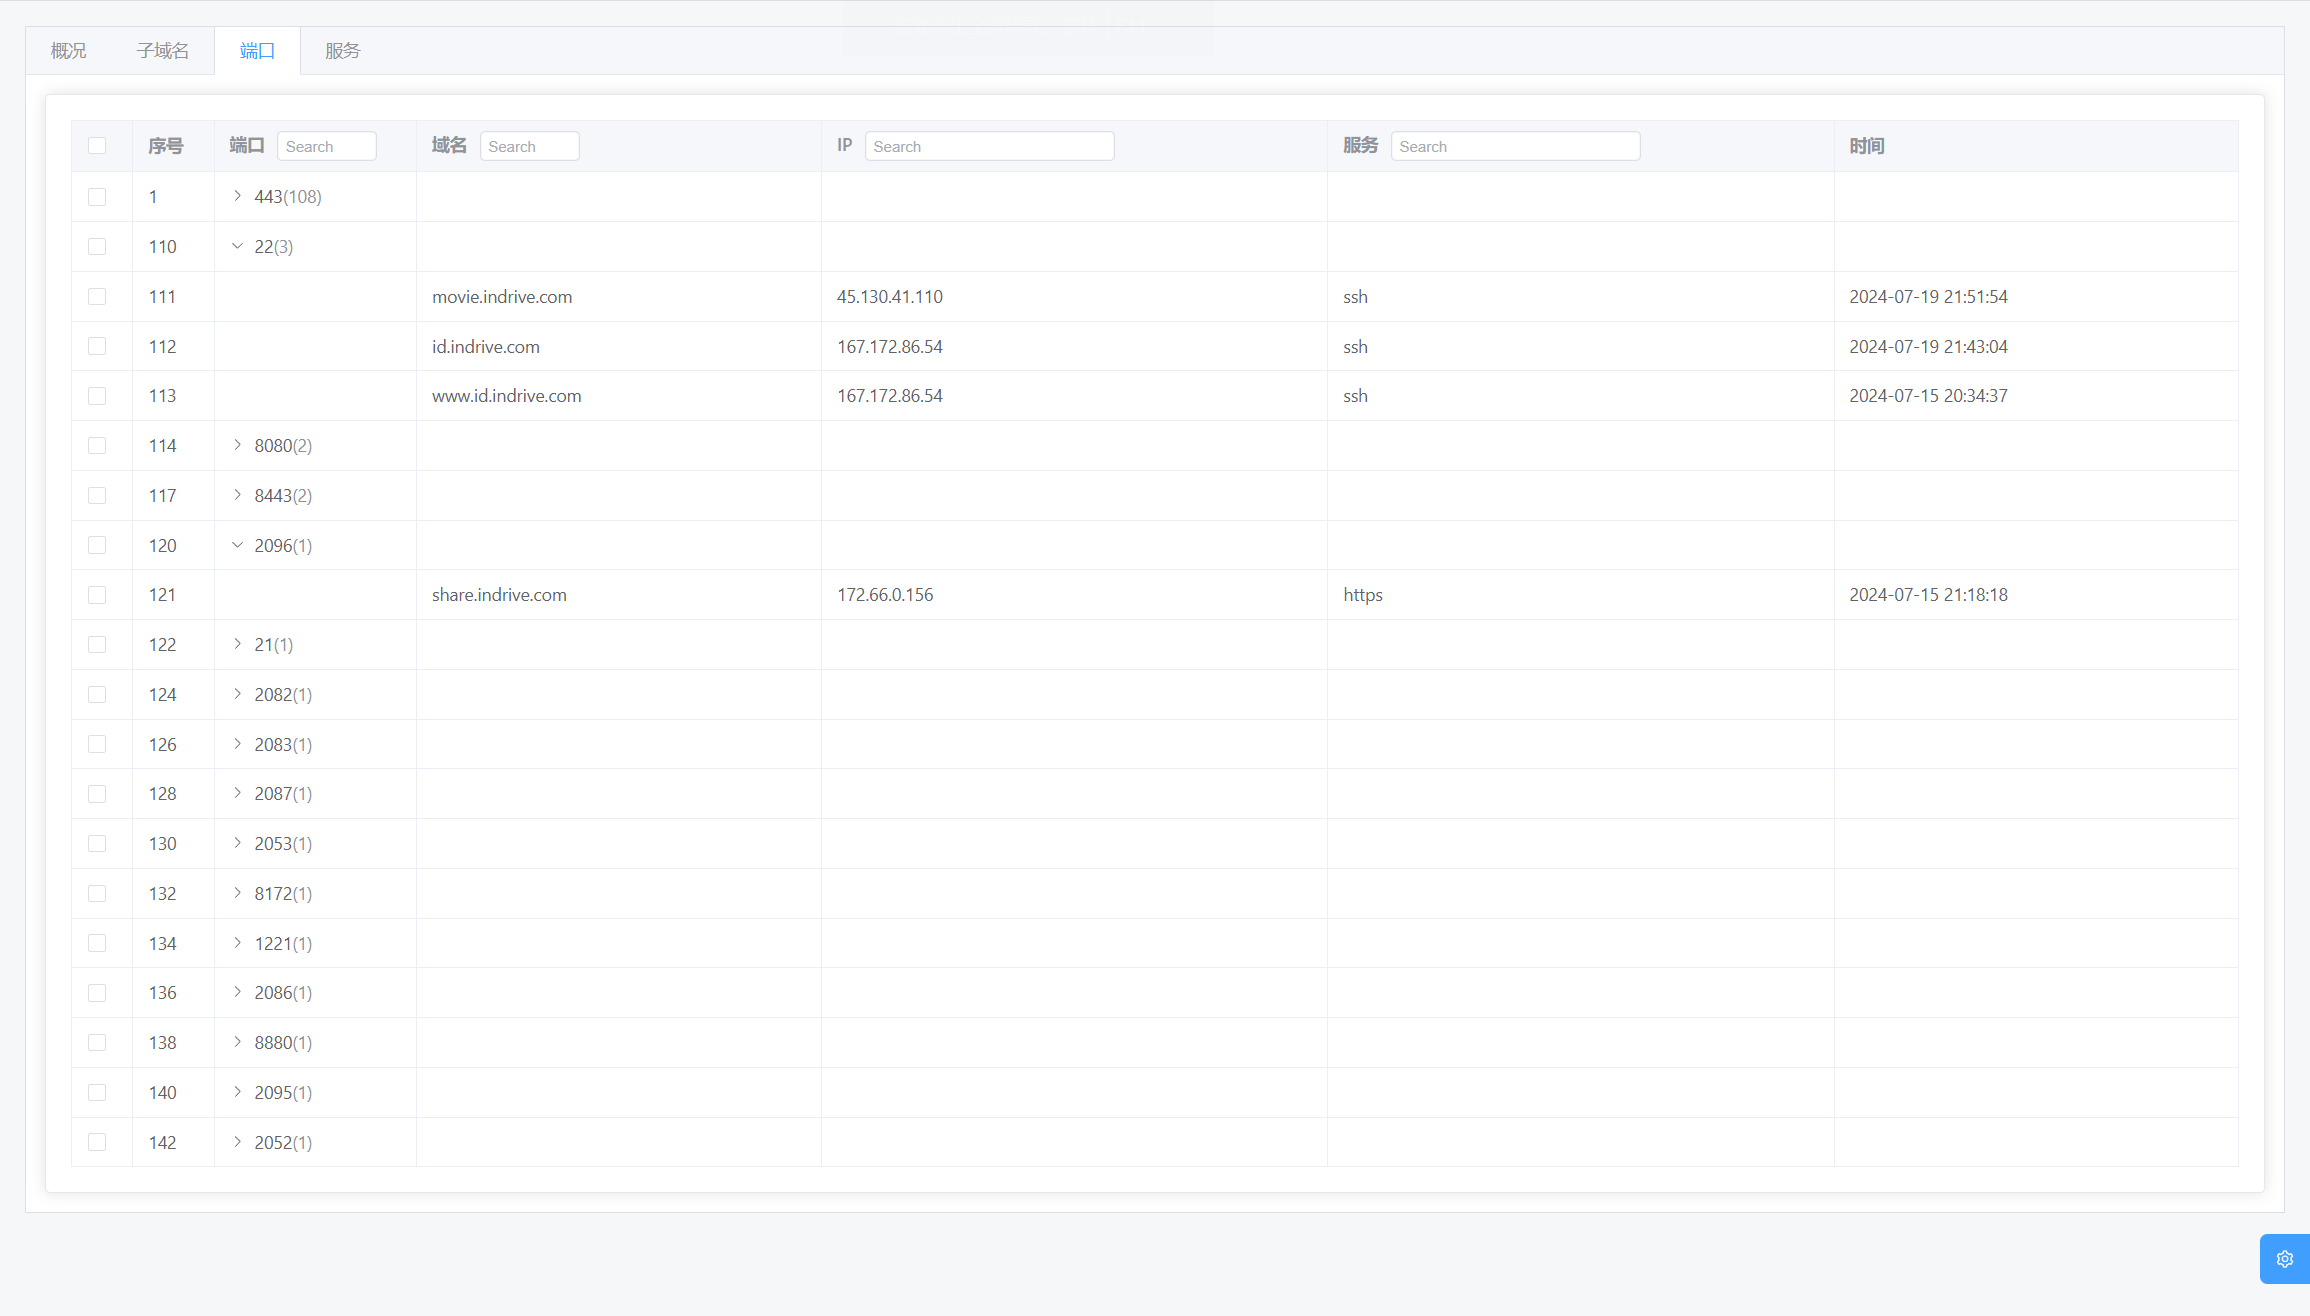
Port
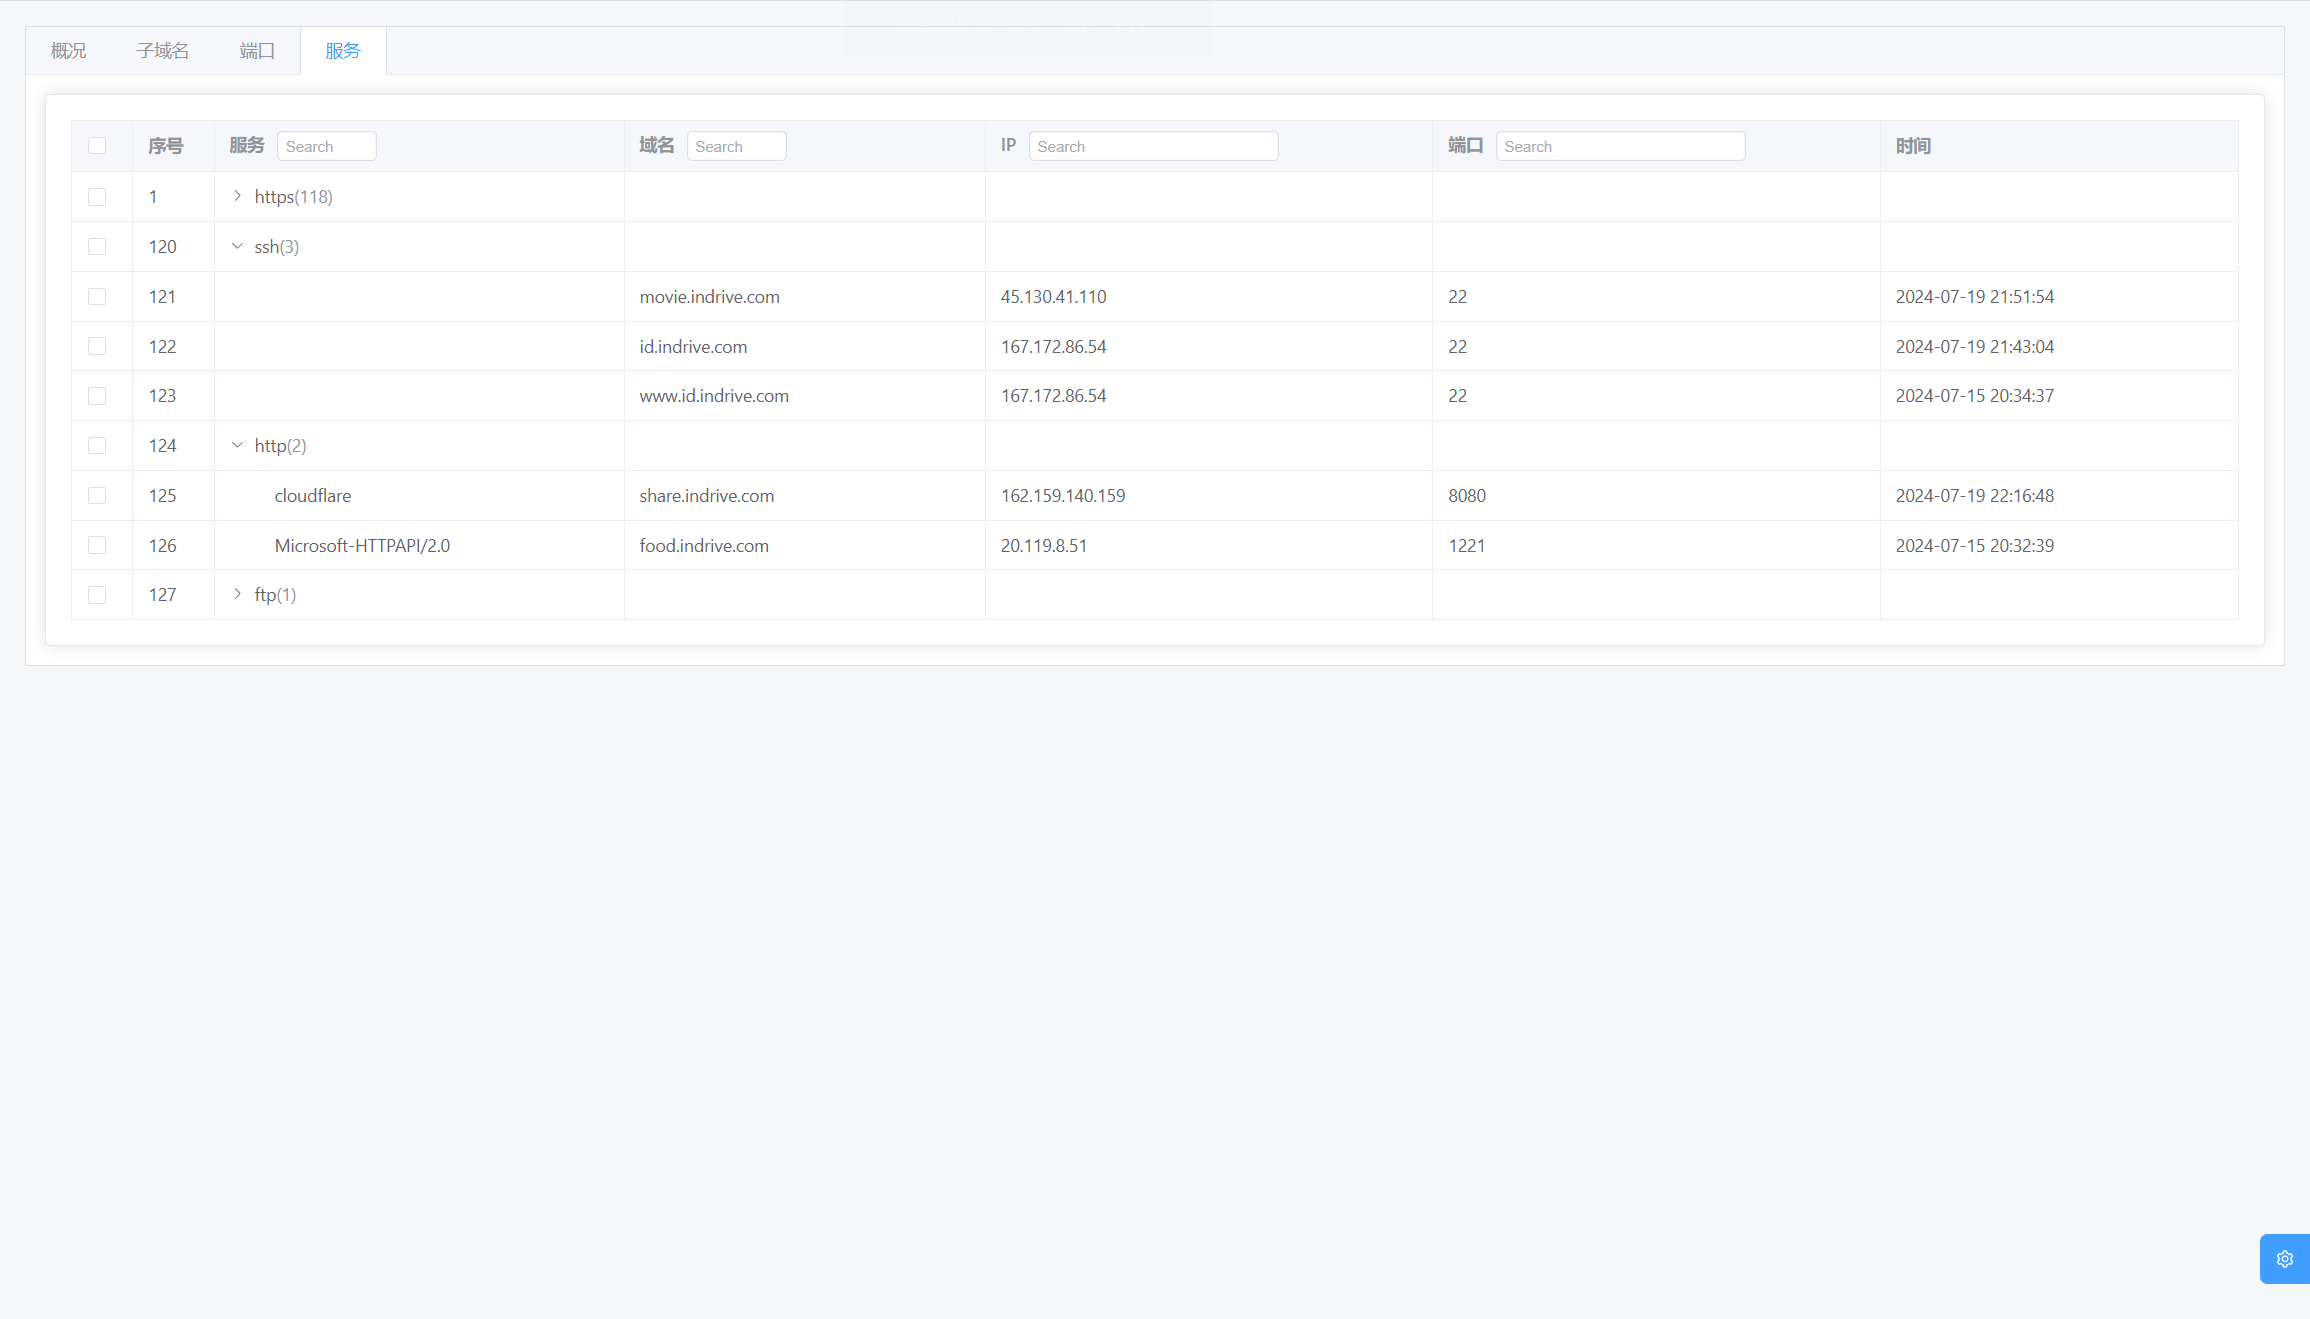
Service
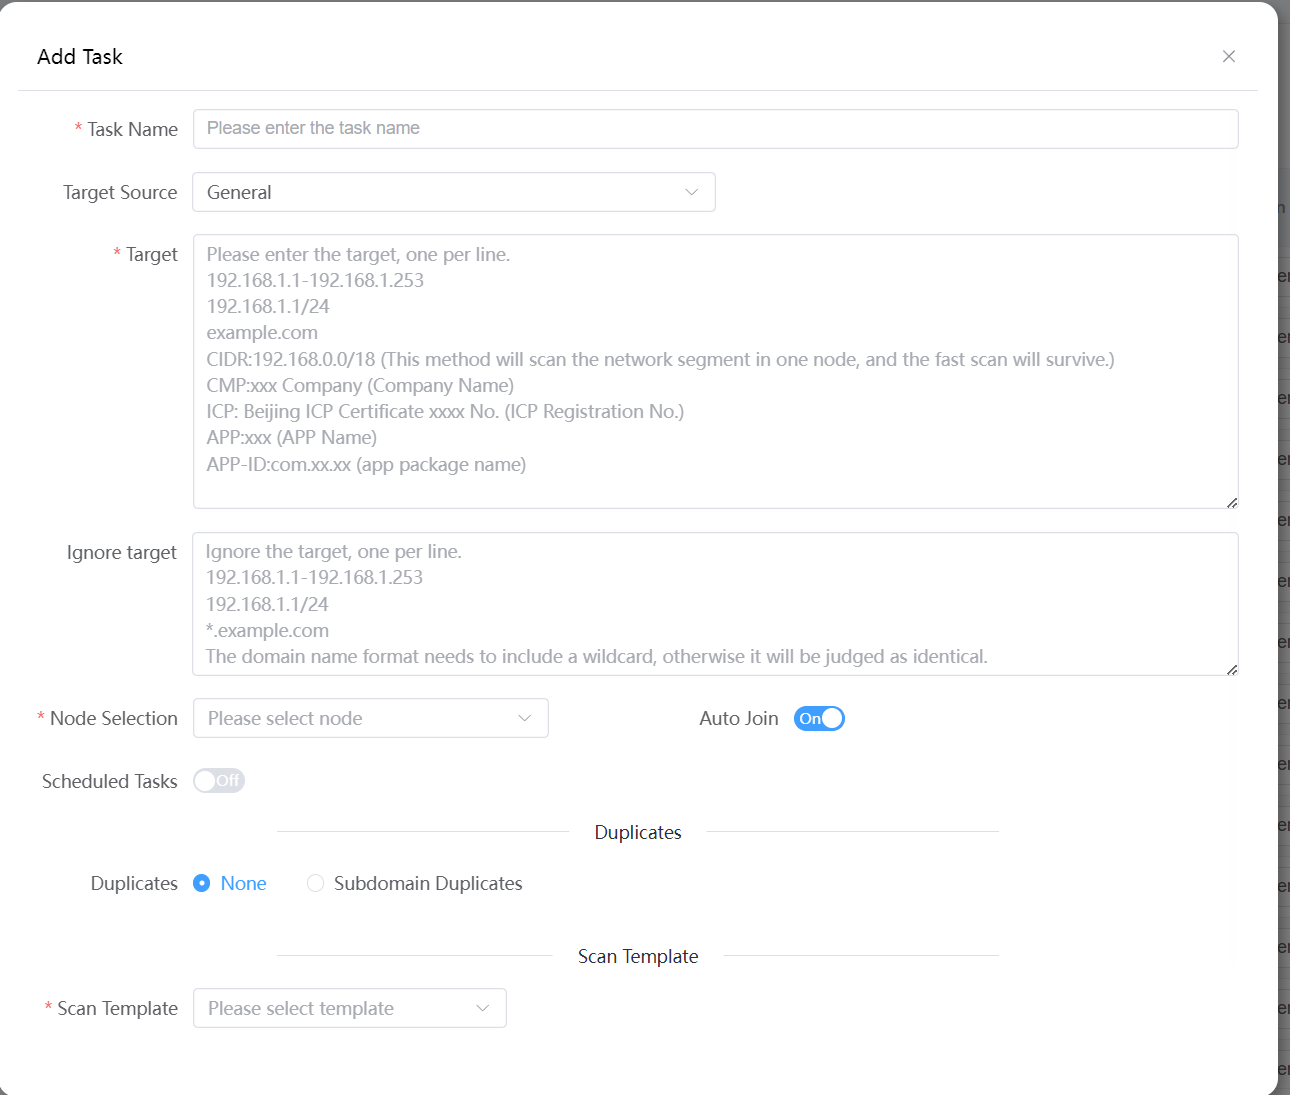
Tasks
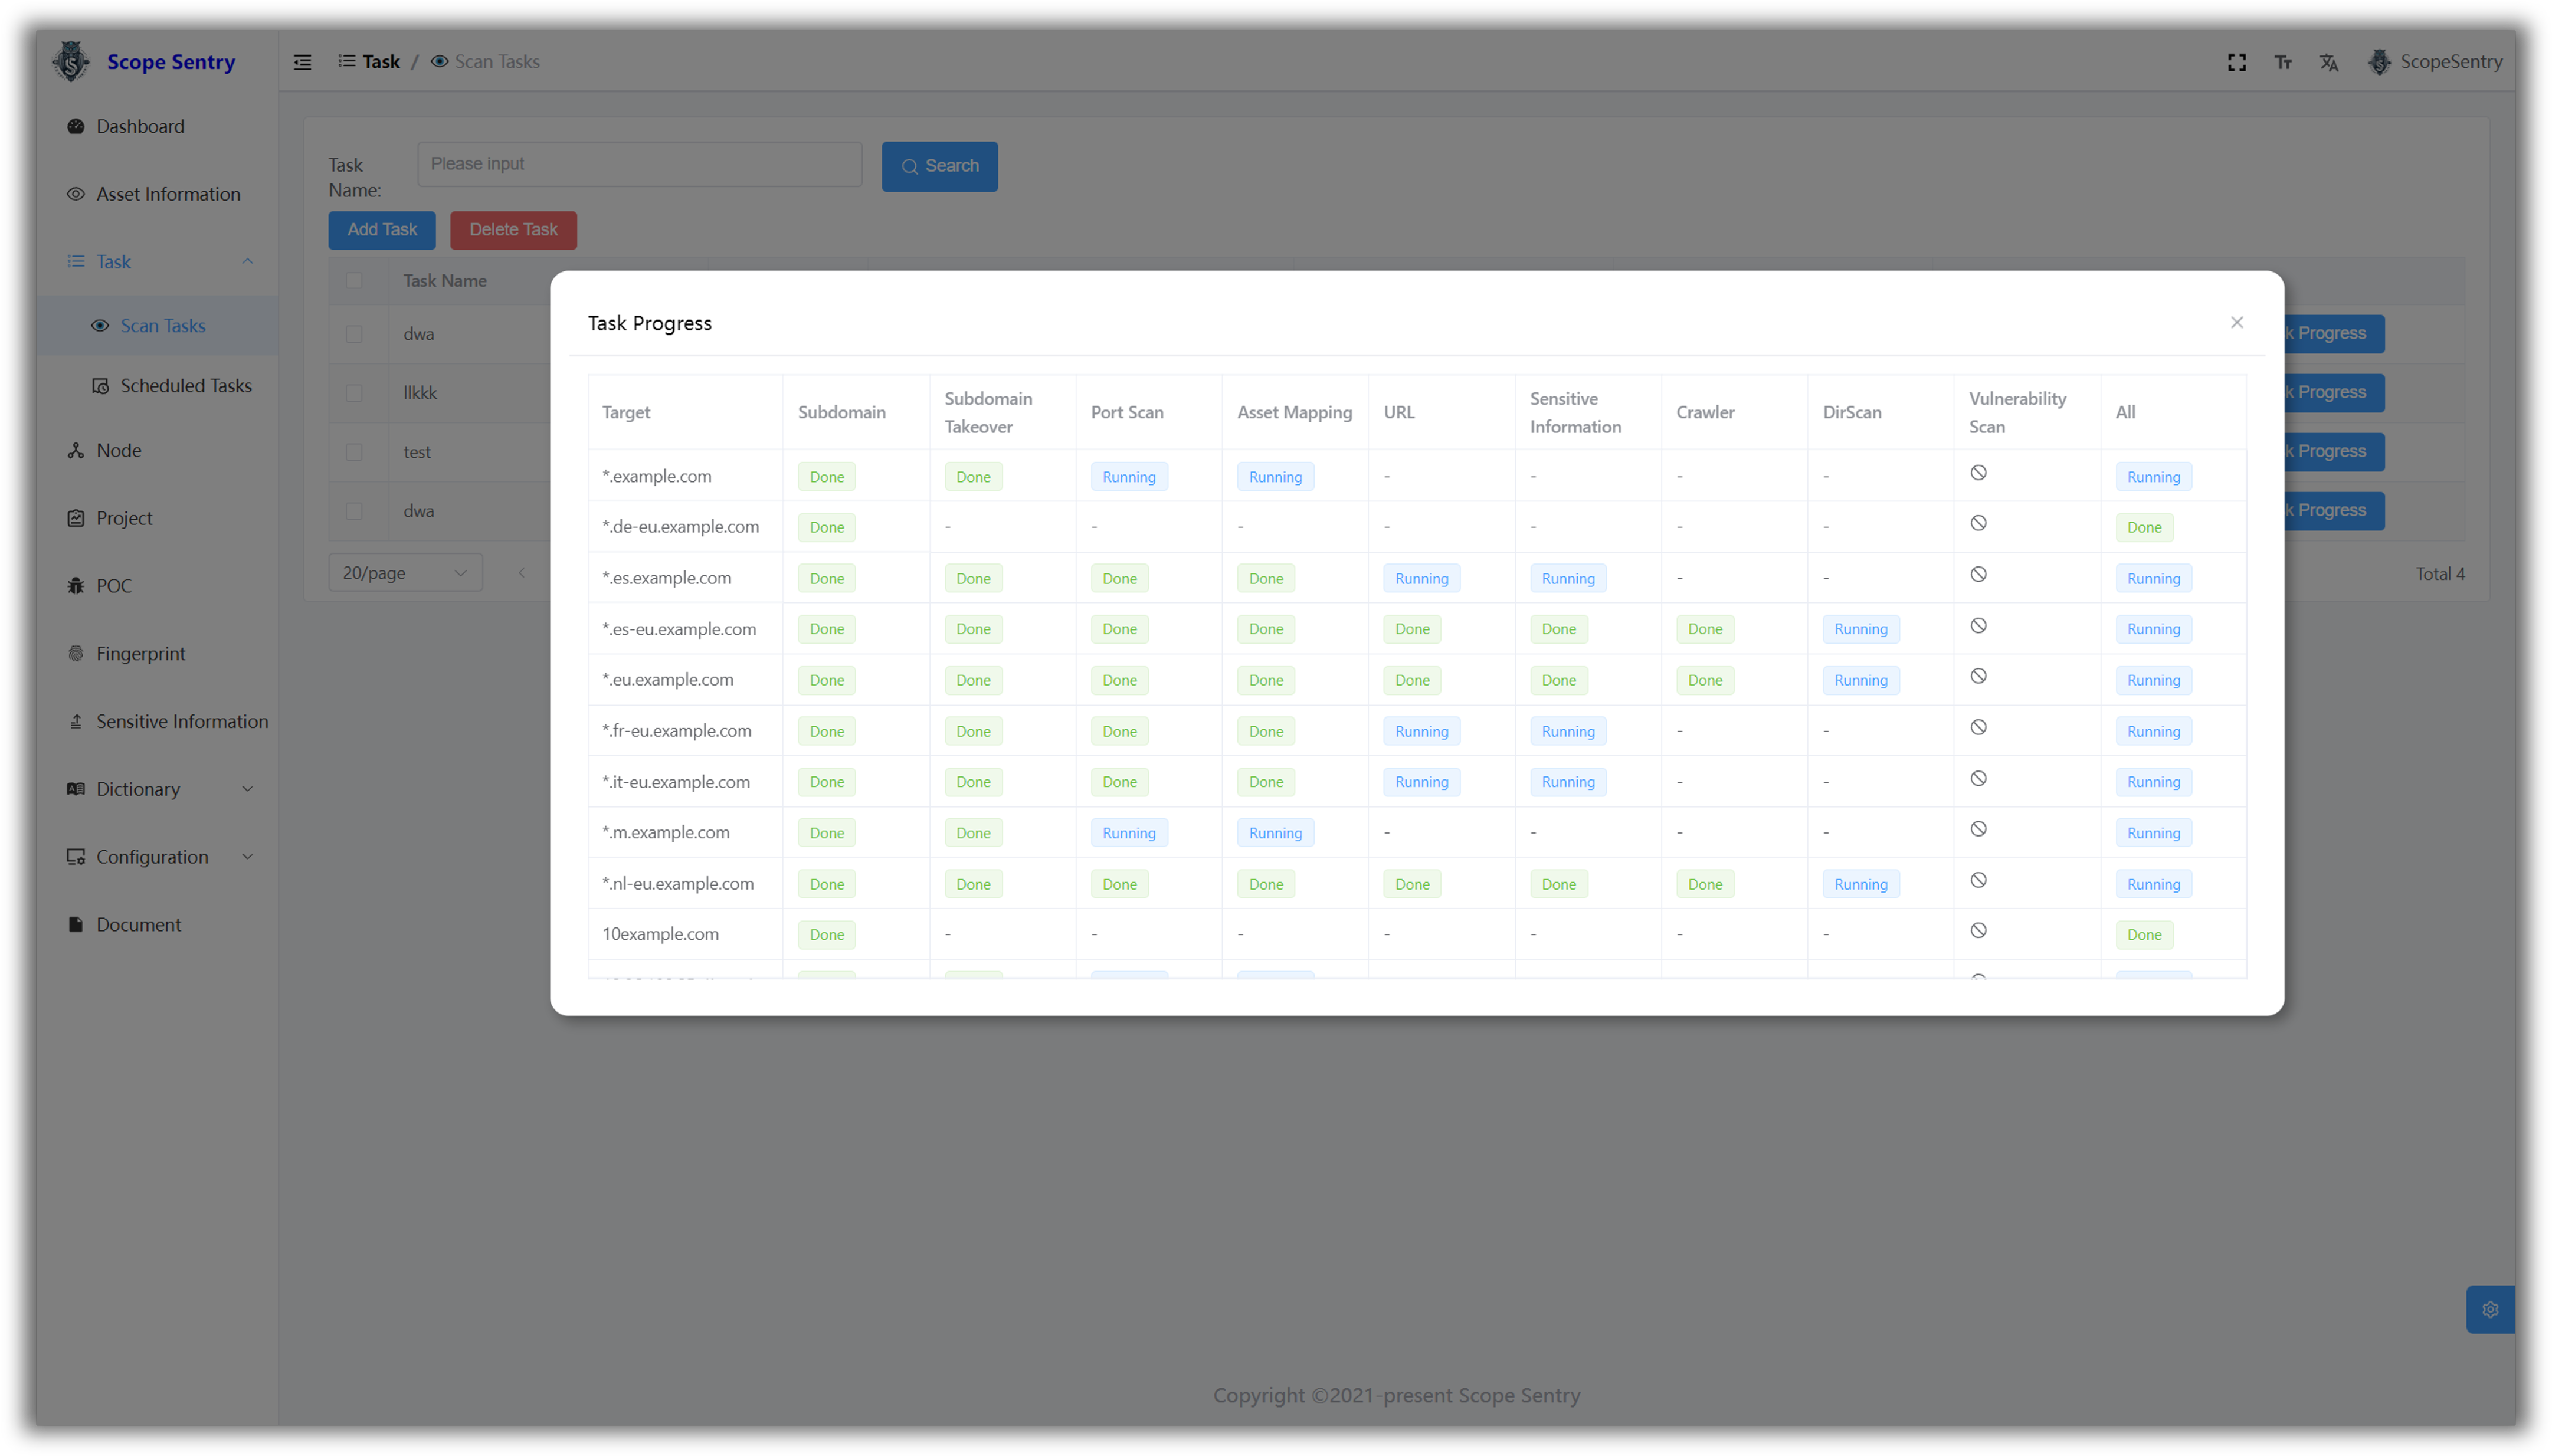
Task Progress
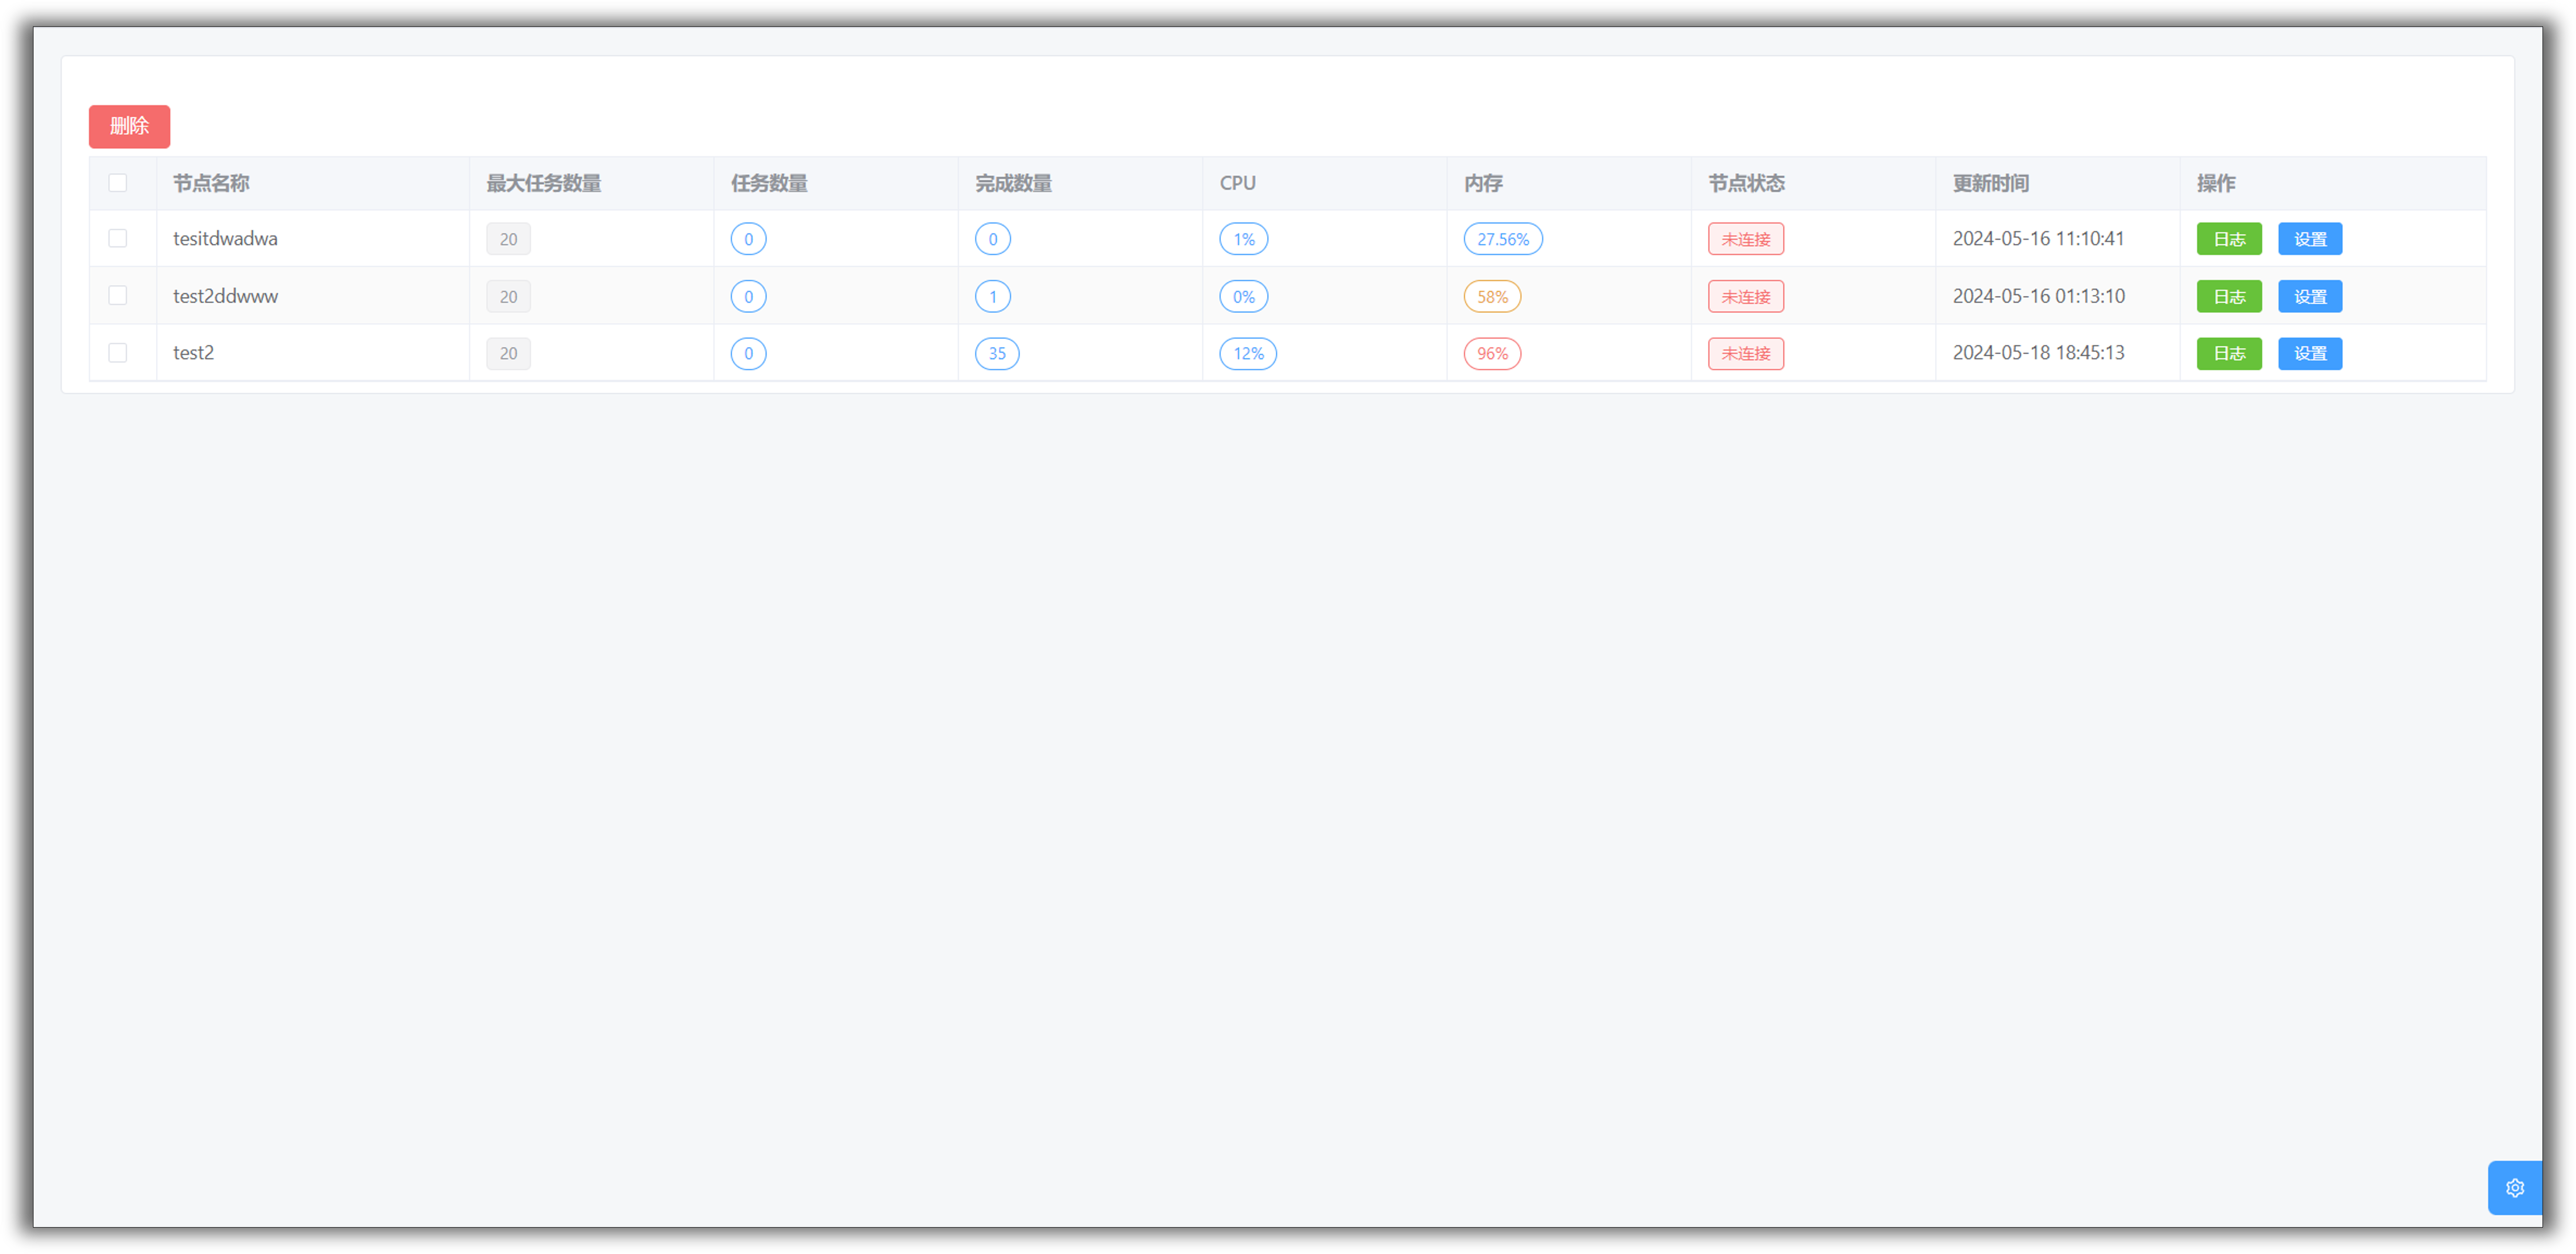
Nodes
License
All branches of this project follow AGPL-3.0, and additional terms need to be followed: 1. The commercial use of this software requires a separate commercial license. 2. Companies, organizations, and for-profit entities must obtain a commercial license before using, distributing, or modifying this software. Individuals and non-profit organizations are free to use this software in accordance with the terms of AGPL-3.0. 4. If you have any commercial license inquiries, please contact [email protected] .