1
 →
Open-source AI penetration testing tool to find and fix your app’s vulnerabilities.
usestrix/strix is an open-source project on GitHub, mainly written in Python. Open-source AI penetration testing tool to find and fix your app’s vulnerabilities. It currently holds 64,997 stars and 7,130 forks with 414 open issues, and was last pushed on 2026-09-25 (repository created 2025-08-05).
Git Homed tracks it on the Today's Trending board, currently at rank #19 with 208 new stars today.




[!TIP]
New! Strix integrates seamlessly with GitHub Actions and CI/CD pipelines. Automatically scan for vulnerabilities on every pull request and block insecure code before it reaches production - Get started with no setup required.
---
Strix are autonomous AI penetration testing agents that act just like real hackers - they run your code dynamically, find vulnerabilities, and validate them through actual proofs-of-concept. Built for developers and security teams who need fast, accurate security testing without the overhead of manual pentesting or the false positives of static analysis tools.
Key Capabilities:
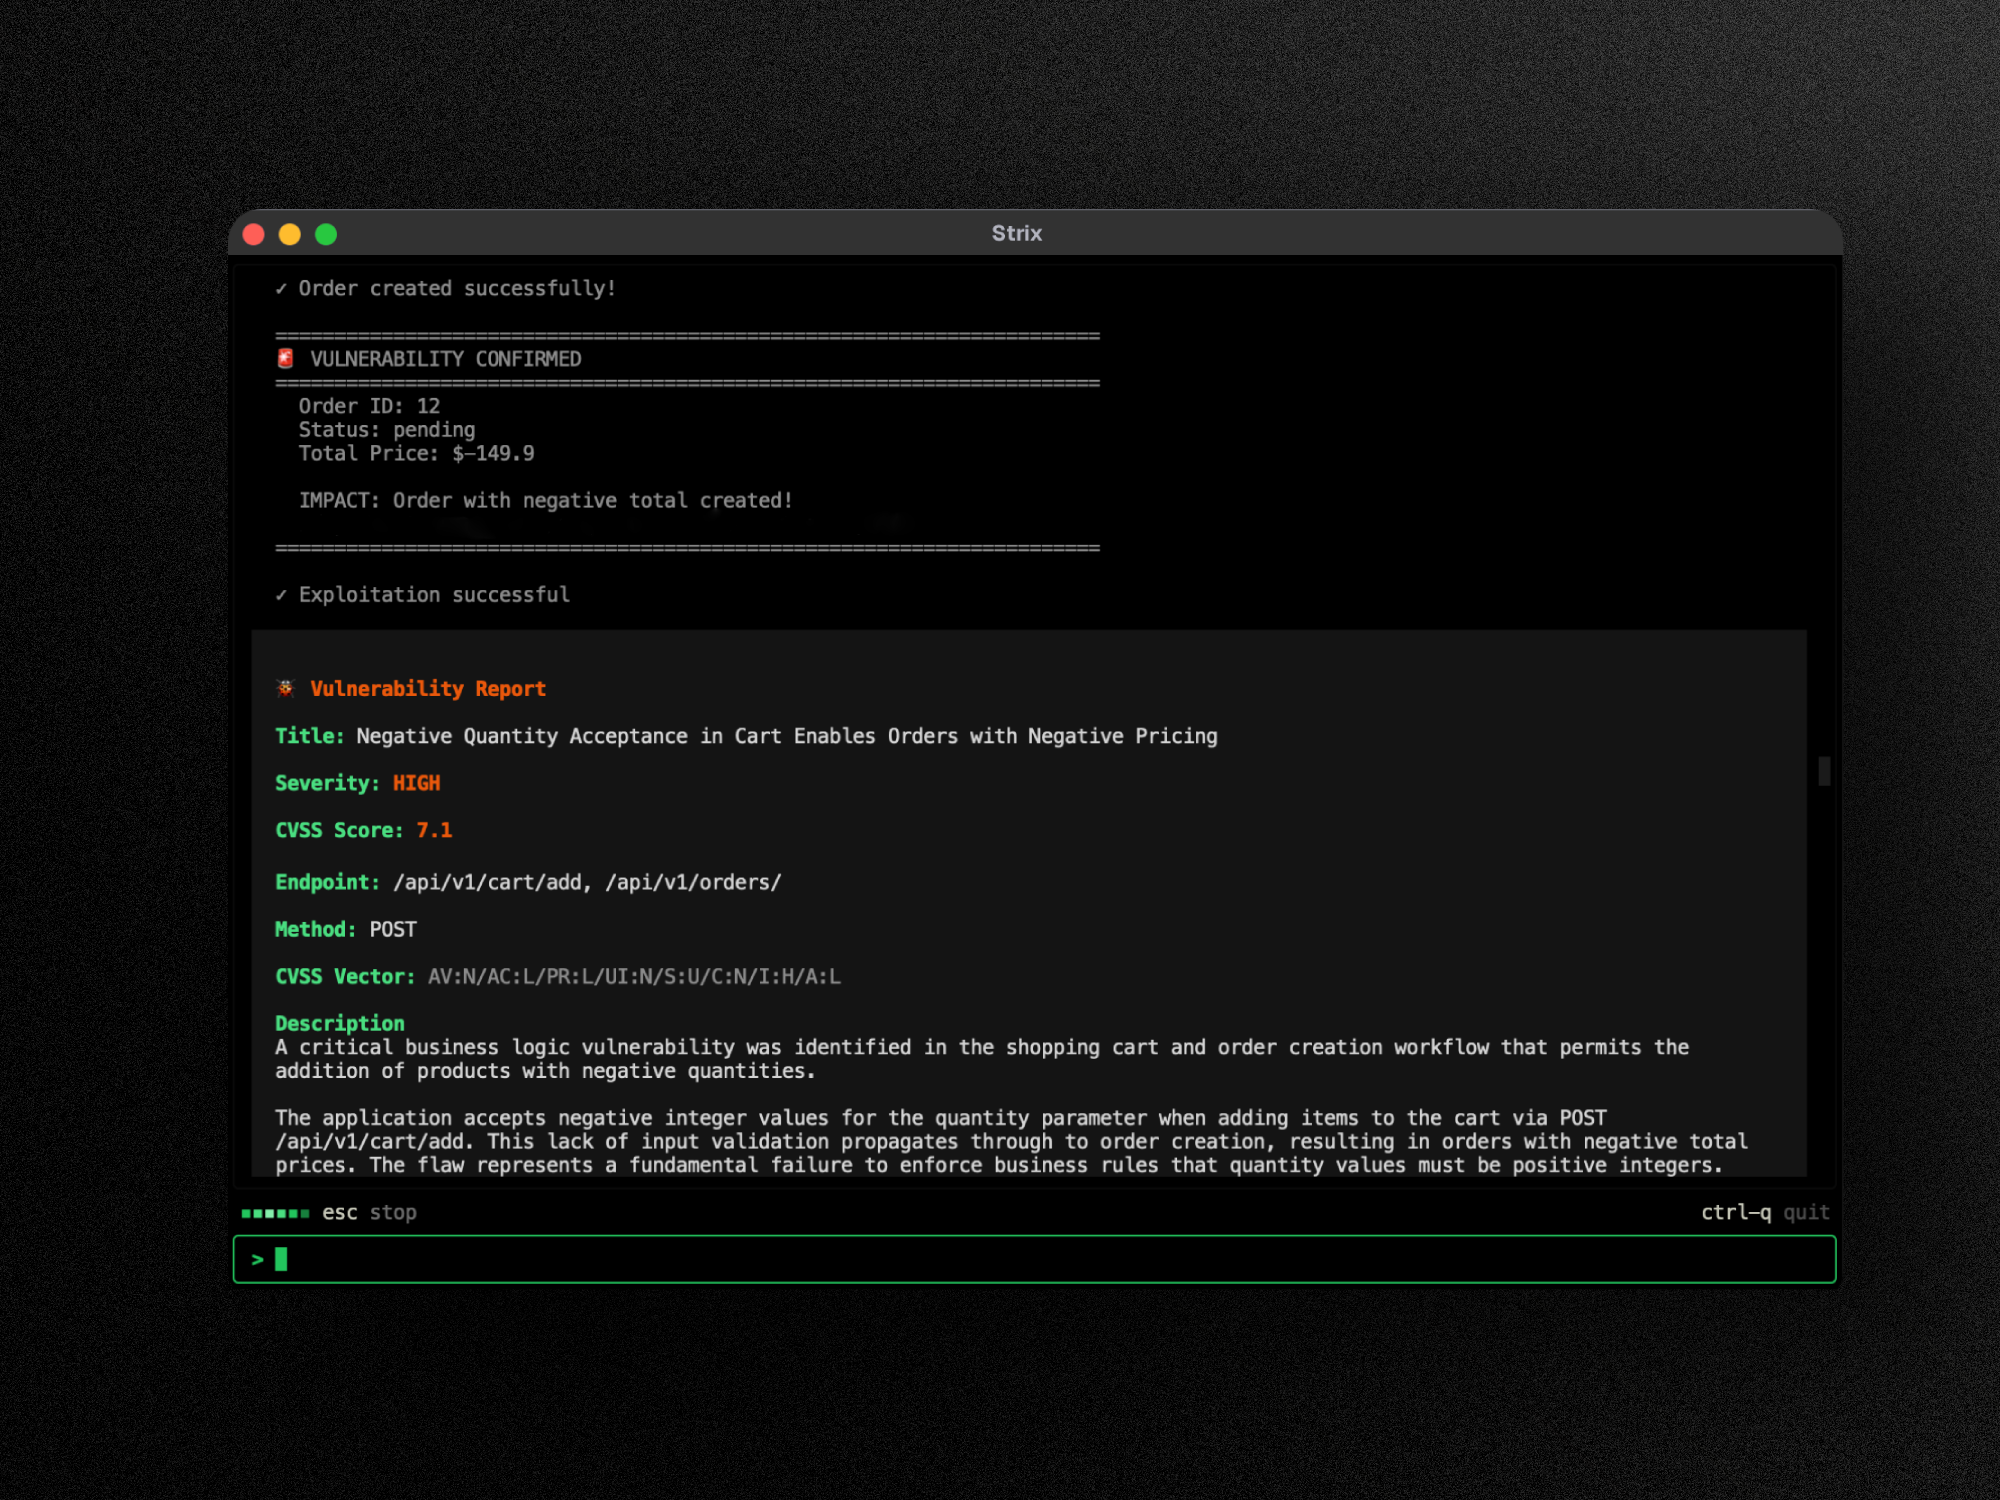
Prerequisites:
# Install Strix
curl -sSL https://strix.ai/install | bash
Configure your AI provider
export STRIX_LLM="openrouter/z-ai/glm-5.3"
export LLM_API_KEY="your-api-key"
Run your first security assessment
strix --target ./app-directory
[!NOTE]
First run automatically pulls the sandbox Docker image. Results are saved to strix_runs/
---
Try the Strix full-stack penetration testing platform at app.strix.ai - sign up for free, connect your repos and domains, and launch a pentest in minutes.
Get the same Strix experience with enterprise-grade controls: SSO (SAML/OIDC), custom compliance-ready penetration testing reports (SOC 2, ISO 27001, PCI DSS), dedicated support and SLA, custom deployment options (VPC or self-hosted), BYOK model support, and tailored AI pentesting agents optimized for your environment.
---
Strix is agent-ready. Give Claude Code, Cursor, Codex, or any SKILL.md-compatible agent the ability to run pentests, fix findings, and set up CI scanning:
npx skills add usestrix/strix
This installs nine skills for running pentests, fixing findings, and CI scanning, against code, web apps, APIs, and the OWASP Top 10. Agents can use the local CLI or the managed cloud with the same engine.
See AGENTS.md for the quick reference, docs.strix.ai/llms.txt for the CLI, and docs.app.strix.ai for the API.
---
Strix agents come equipped with a comprehensive offensive security toolkit - the same tools used by professional penetration testers and ethical hackers:
Strix identifies, validates, and exploits a wide range of security vulnerabilities across the OWASP Top 10 and beyond:
Advanced multi-agent orchestration for comprehensive automated penetration testing:
Every scan writes its results to disk as it runs. Bring them up in a local dashboard with a single command:
# Open the most recent run
strix view
...or open a specific run by name
strix view my-run-name
Expose the viewer on all IPv4 interfaces at a fixed port
strix view --host 0.0.0.0 --port 8080 --no-open
The dashboard shows the findings, a live map of the agent team, and past runs. Nothing leaves your machine, and the UI ships prebuilt. strix view binds to 127.0.0.1 and prints a tokened link that grants access to the run, so share it carefully.
See the viewer documentation for the options and for reaching the viewer from another machine.
---
# Scan a local codebase
strix --target ./app-directory
Security review of a GitHub repository
strix --target https://github.com/org/repo
Black-box web application assessment
strix --target https://your-app.com
Point Strix at an API contract and it tests every declared endpoint instead of having to discover them by crawling. Pair the spec with the live base URL so the agent knows where to send traffic:
# OpenAPI / Swagger file, Postman export, or a live collection by id
strix --target ./openapi.yaml --target https://api.your-app.com
strix --target postman:// --target https://api.your-app.com
# Grey-box authenticated testing
strix --target https://your-app.com --instruction "Perform authenticated testing using credentials: user:pass"
Multi-target testing (source code + deployed app)
strix -t https://github.com/org/app -t https://your-app.com
Targets from a file, one target per non-empty, non-comment line
strix --target-list ./targets.txt
See the CLI reference for every option, including scan modes, diff scope, instruction files, and budgets.
Run Strix programmatically without interactive UI using the -n/--non-interactive flag - perfect for servers and automated jobs. The CLI prints real-time vulnerability findings and the final report before exiting. Exits with non-zero code when vulnerabilities are found.
strix -n --target https://your-app.com
Strix can be added to your pipeline to run a security test on pull requests with a lightweight GitHub Actions workflow:
name: strix-penetration-test
on:
pull_request:
jobs:
security-scan:
runs-on: ubuntu-latest
steps:
- uses: actions/checkout@v6
with:
fetch-depth: 0
- name: Install Strix
run: curl -sSL https://strix.ai/install | bash
- name: Run Strix
env:
STRIX_LLM: ${{ secrets.STRIX_LLM }}
LLM_API_KEY: ${{ secrets.LLM_API_KEY }}
run: strix -n -t ./ --scan-mode quick
[!TIP]
In CI pull request runs, Strix automatically scopes quick reviews to changed files, which is why the
checkout above fetches full history. See the
CI/CD documentation for the details.
export STRIX_LLM="openrouter/z-ai/glm-5.3"
export LLM_API_KEY="your-api-key"
Optional
export LLM_API_BASE="your-api-base-url"  # if using a local model, e.g. Ollama, LMStudio
[!NOTE]
Strix automatically saves your configuration to ~/.strix/cli-config.json, so you don't have to re-enter it on every run.
See the configuration reference for every environment variable.
Instead of a metered API key, you can run Strix on your ChatGPT Plus/Pro subscription:
strix auth login chatgpt             # sign in with your ChatGPT account
export STRIX_LLM="chatgpt/gpt-5.4"   # chatgpt/ runs on the subscription
strix auth status                    # show the active sign-in, or logout to forget it
strix cloudRun scans on app.strix.ai from the terminal, without Docker or an LLM key:
strix cloud login                                  # browser sign-in, one credential per install
strix cloud scans start --source . --yes --wait    # scan local code, approving the upload
strix cloud scans start --engagement-type live_test --domain-ids  --wait
strix cloud vulns list --severity critical
Every REST API operation has a matching strix cloud command. Run strix cloud to list the resources, and add help to a resource to list its verbs. Output is JSON when stdout is not a terminal or when you pass --json. Binary downloads are the exception: redirect the raw bytes, or combine --output FILE --json for download metadata.
See the cloud CLI documentation for scopes, workspaces, billing, and source-upload options.
Strix can connect to Model Context Protocol (MCP) servers you list and expose their tools to the agent during a run. Create ~/.strix/mcp-servers.json with a JSON list of local stdio servers or remote http servers:
[
  {
    "name": "github",
    "transport": "http",
    "url": "https://api.githubcopilot.com/mcp/",
    "auth": { "kind": "bearer", "token": "your-token" },
    "allowed_tools": ["list_issues"]
  }
]
Each server's tools are namespaced by name, for example github_list_issues. See the MCP documentation for the full schema, tool filtering, and stdio servers.
Recommended models for best results:
openrouter/z-ai/glm-5.3 (the default pick)openai/gpt-5.4anthropic/claude-sonnet-4-6vertex_ai/gemini-3-pro-previewdeepseek/deepseek-v4-promoonshot/kimi-k3Full documentation is available at docs.strix.ai - including detailed guides for usage, CI/CD integrations, skills, and advanced configuration.
We welcome contributions of code, docs, and new skills - check out our Contributing Guide to get started or open a pull request/issue.
Have questions? Found a bug? Want to contribute? Join our Discord!
Love Strix? Give us a ⭐ on GitHub!
Strix builds on the incredible work of open-source projects like LiteLLM, Caido, Nuclei, Playwright, and Bubble Tea. Huge thanks to their maintainers!
[!WARNING]
Authorized use only. Strix actively tests the targets you point it at, so only run it against systems you own or have explicit, written permission to test, and stay within the agreed scope. Unauthorized testing is illegal in most jurisdictions.
You alone are responsible for obtaining authorization and complying with the law. Strix is provided "as is" with no warranty or liability for misuse.
→ →
 →
 →
 →
 →
 →
 →