1
 →
Shannon is an AI pentester for web applications and APIs. It analyzes your source code, identifies attack vectors, and executes real exploits to prove vulnerabilities before they reach production.
KeygraphHQ/shannon is an open-source project on GitHub, mainly written in TypeScript. Shannon is an AI pentester for web applications and APIs. It analyzes your source code, identifies attack vectors It currently holds 50,285 stars and 5,782 forks with 29 open issues, and was last pushed on 2026-10-27 (repository created 2025-09-27).
Git Homed tracks it on the Today's Trending board, currently at rank #25 with 334 new stars today.
[!NOTE]
php2shell upgrade verification: confirm your PHP apps are patched against the php2shell RCE chain with the experimental --exp-php2shell probe. See the test results.
It analyzes your source code, identifies attack paths, and executes real exploits to prove vulnerabilities before they reach production. No exploit, no report.
This repository is Shannon: the full open-source agent, run locally from your command line.
Launch Shannon
npx @keygraph/shannon@latest
The interactive launcher will guide you through setup and your first pentest.
---
---
[!TIP]
AI agents and LLMs: start with llms.txt for a concise map of this repository, or use llms-full.txt for the README and docs combined into one file.
Shannon is an autonomous AI pentester developed by Keygraph. It performs security testing of web applications and their underlying APIs by combining source-code analysis with live exploitation.
Shannon analyzes your web application's source code to identify potential attack vectors, then uses browser automation and command-line tools to execute real exploits against the running application and its APIs. Only vulnerabilities with a working proof-of-concept are included in the final report.
Shannon is the agent. This repository is Shannon, the open-source pentester you run yourself. The same Shannon also powers Keygraph's commercial editions, Pro and Enterprise. See Editions for how Shannon compares with Pro, Enterprise, and the Community Program.
Thanks to tools like Claude Code and Cursor, your team ships code non-stop. But your penetration test? That happens once a year. This creates a massive security gap. For the other 364 days, you could be unknowingly shipping vulnerabilities to production.
Shannon closes that gap by providing on-demand, automated penetration testing that can run against every build or release.
It's named after Claude Shannon, the father of information theory. At its core, pentesting is an information problem: every probe reduces uncertainty about a system's state. The best tools maximize the signal gained from every request, turning those bits of knowledge into an exploit path.
Also, we wanted you to be able to say, "Hey Claude, run Shannon" to find all the security flaws in your vibe-coded app.
Not a replacement for human pentesters
Shannon is built to work alongside expert pentesters and red teamers, not replace them. Great pentesters understand the business, chain attacks in ways nobody anticipated, and bring years of judgment that current models can't match.
Shannon solves a different problem: there is far more software to test than security teams have time to cover. Critical systems get periodic expert assessments, while the long tail of internal apps, APIs, and fast-moving services rarely gets tested at all.
Shannon shifts pentesting left into the software development lifecycle (SDLC). Use it to run exploitation-backed tests against staging environments and releases at the cadence they actually ship, and save expert human time for the risks that need someone who knows the organization.
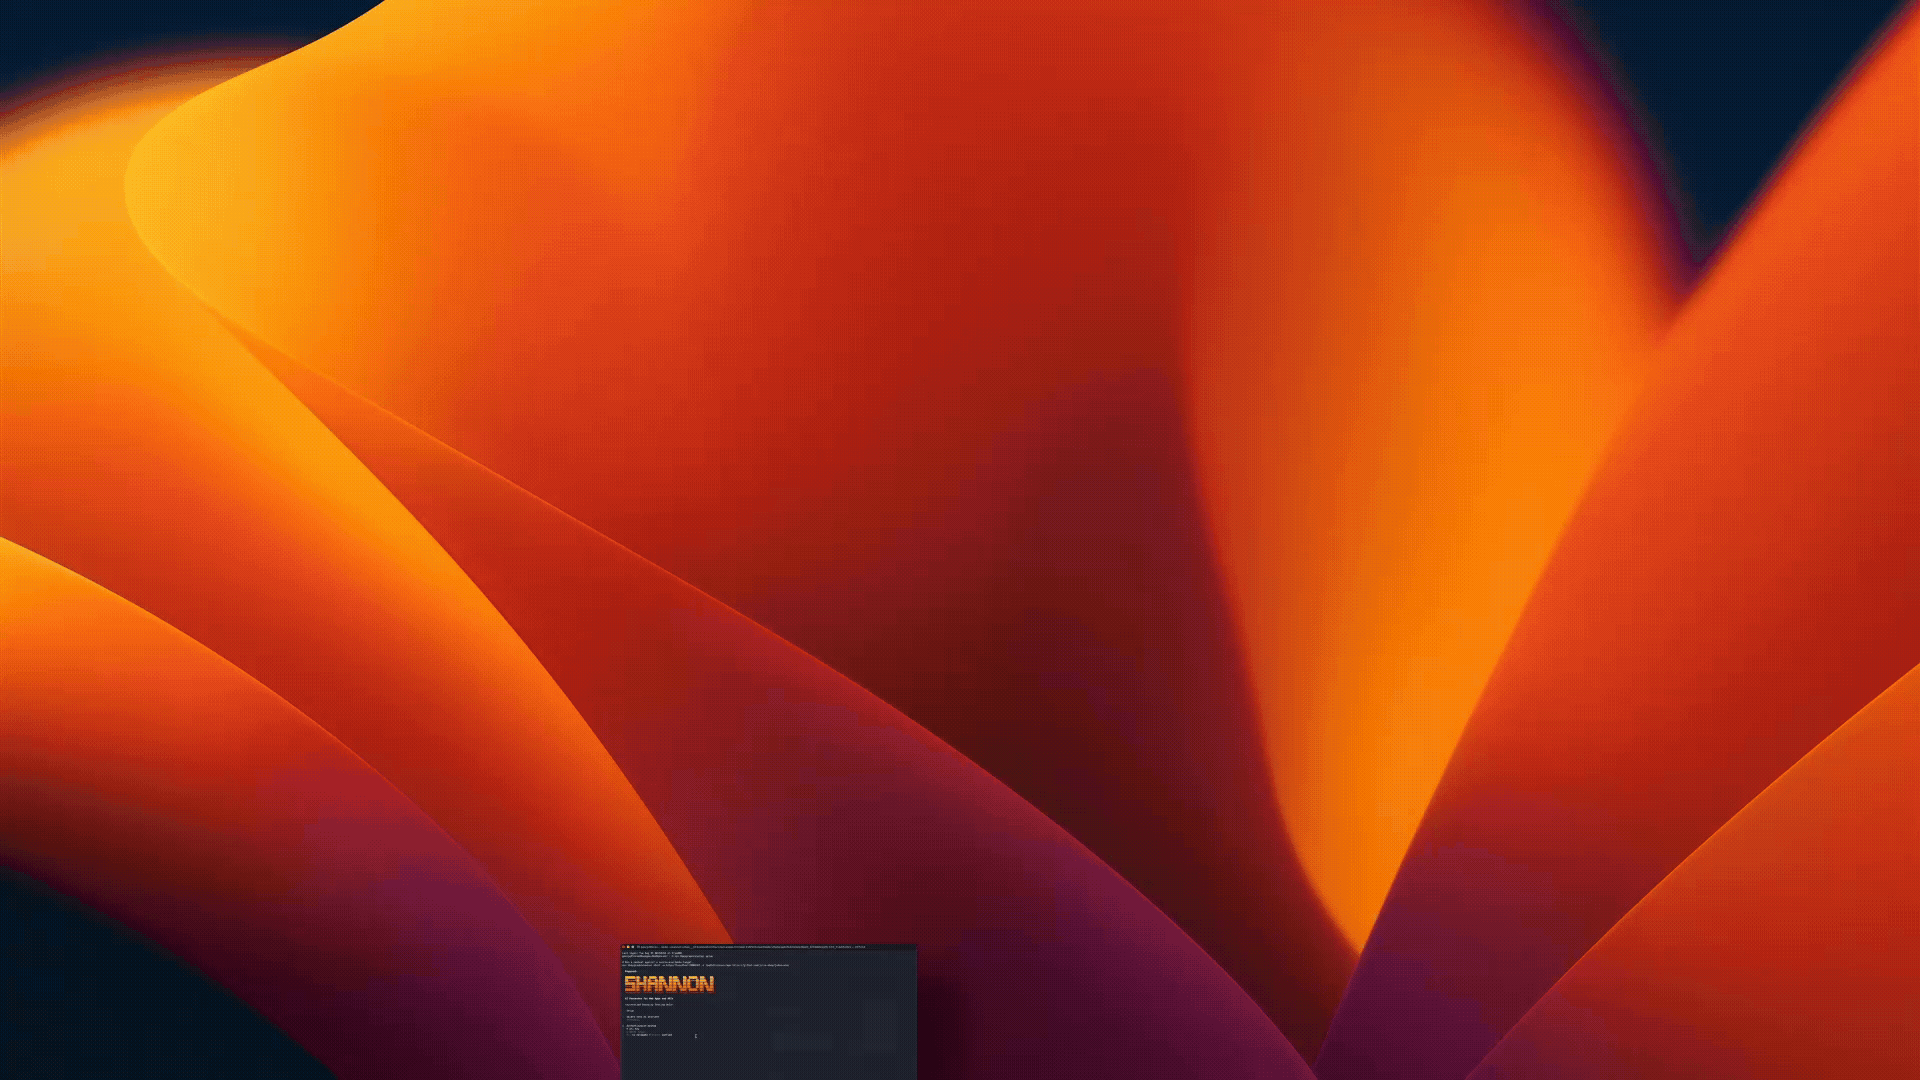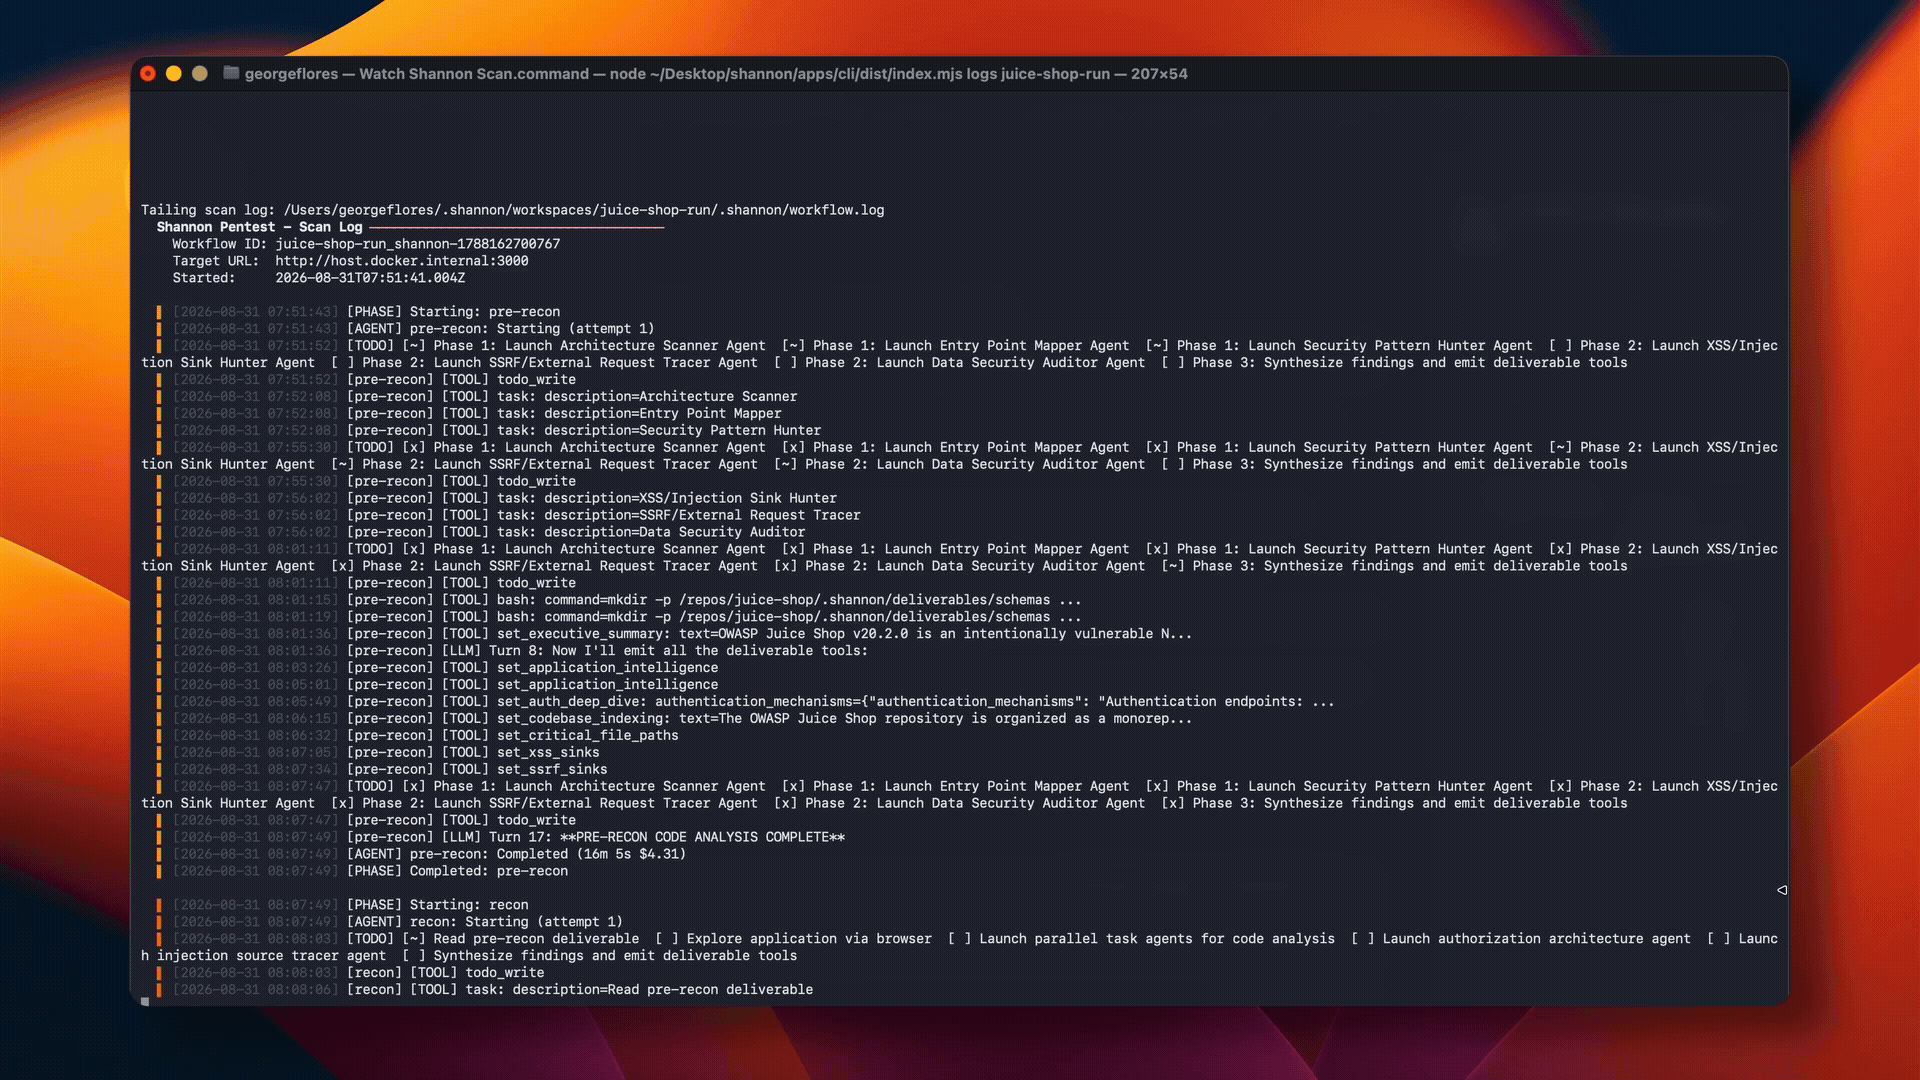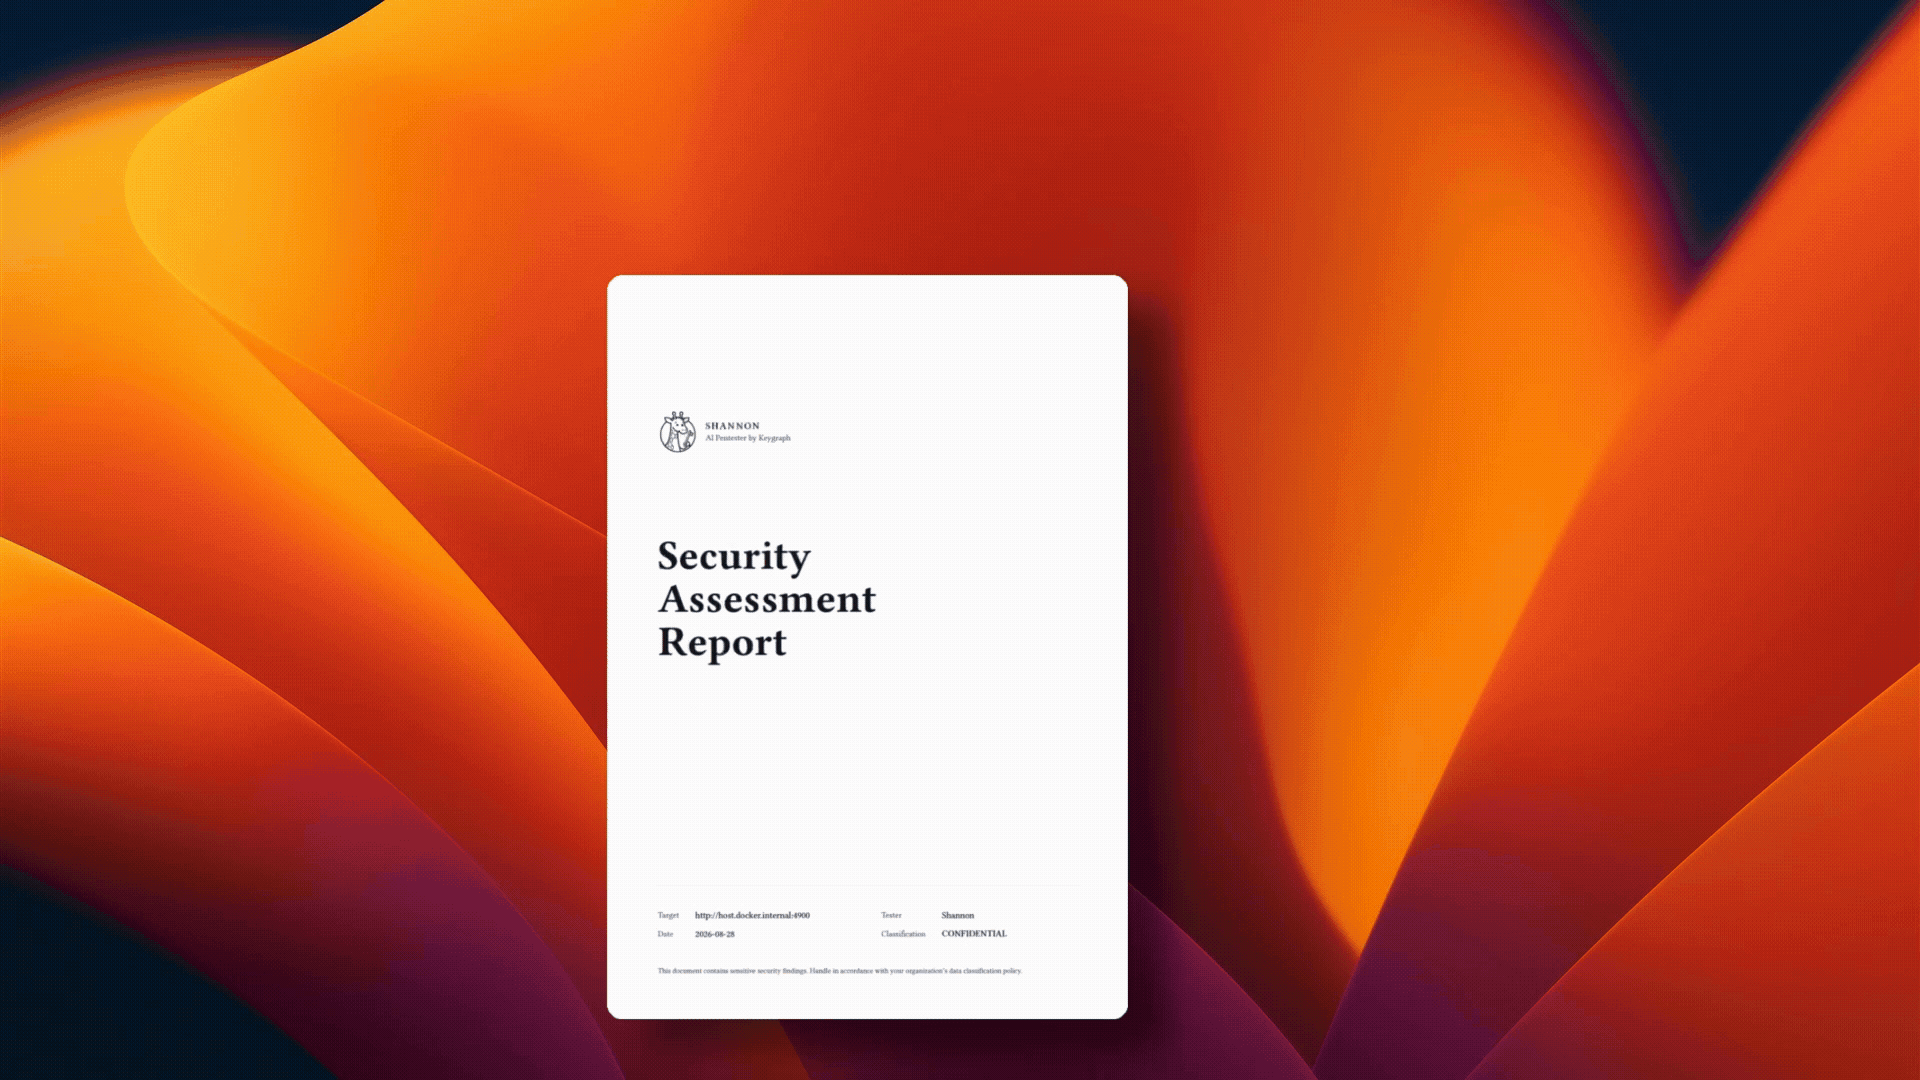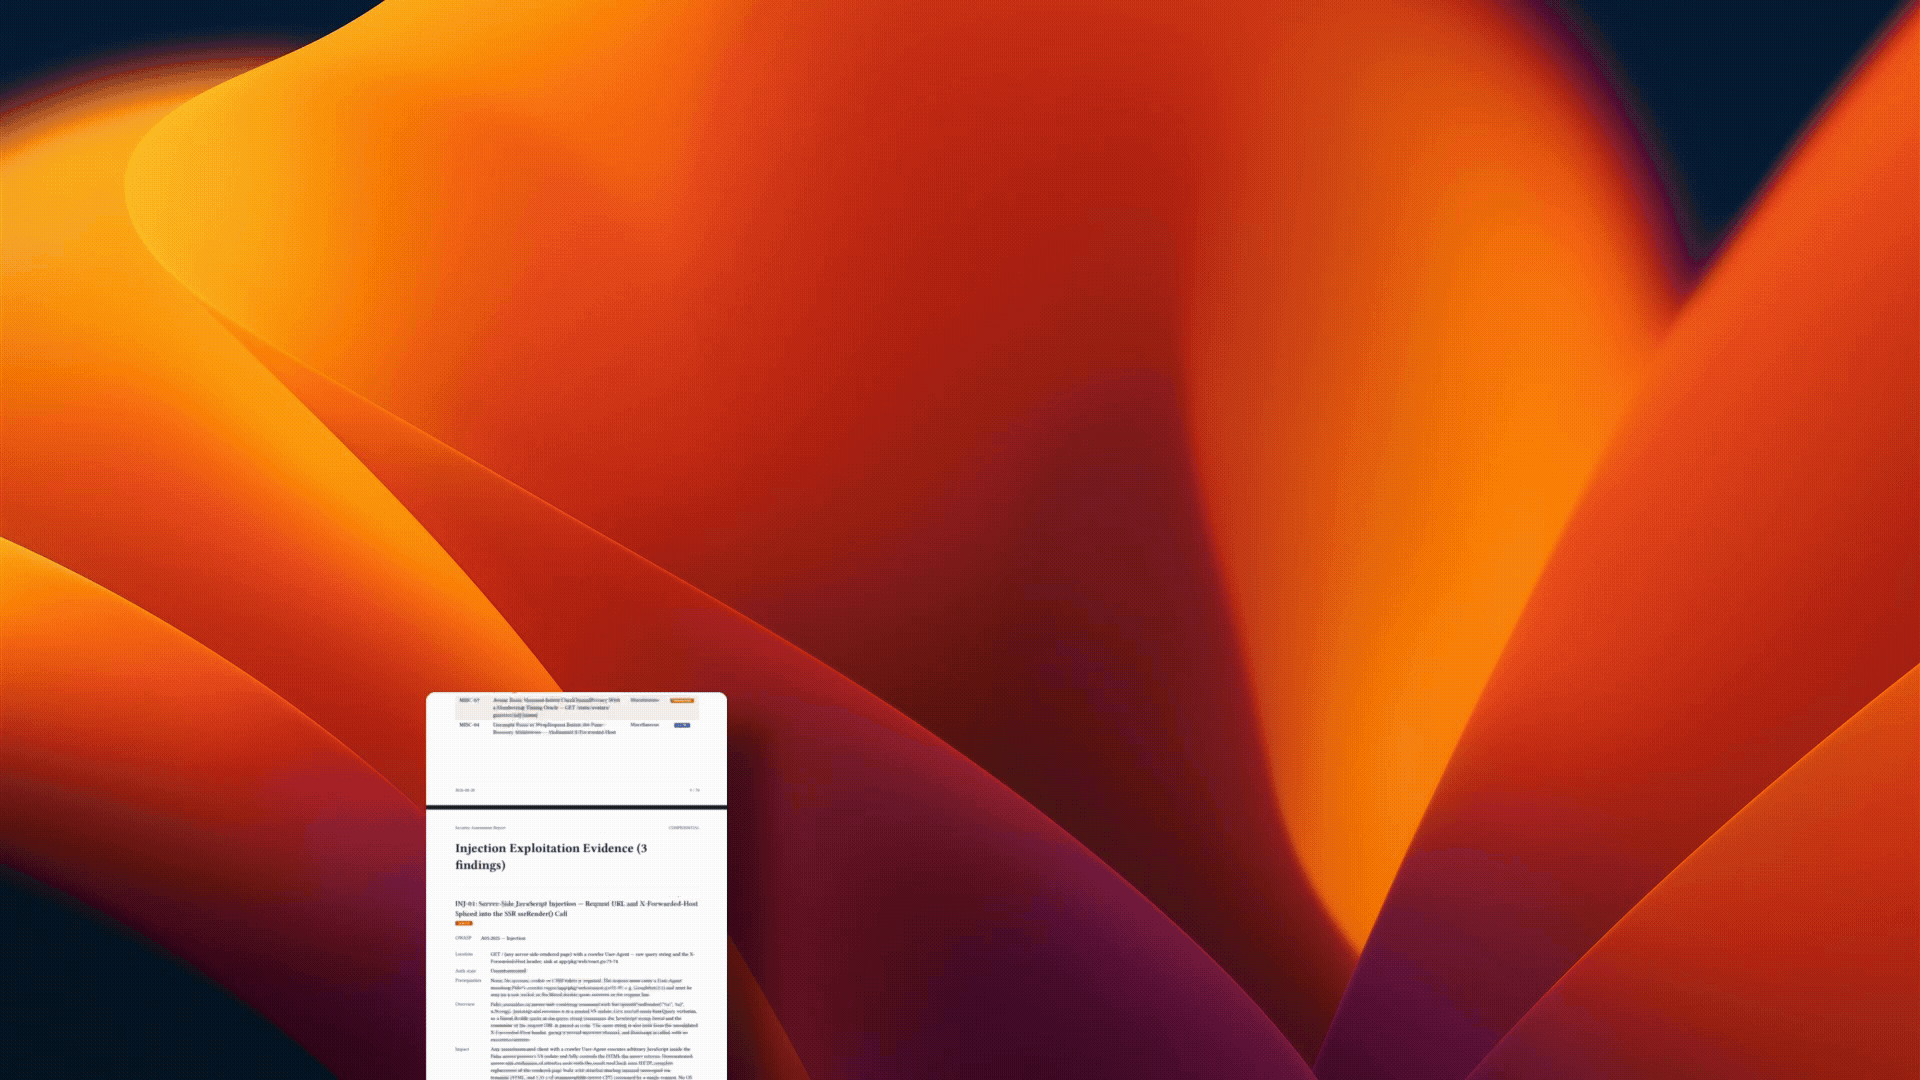
These reports are from Shannon OSS scans of Photoview 2.4.0, one of the applications in Doyensec's comparison of Aikido and XBOW. We ran Shannon against the same application version and evaluated its results separately. Read the Doyensec study and our Shannon follow-up comparison for the methodology, limitations, costs, and results.
| Model | Report | SARIF | | ----------------- | ---------------------------------------------------------------------------- | --------------------------------------------------------------- | | DeepSeek v4 Flash | View report | SARIF | | Grok 4.6 | View report | SARIF | | Claude Opus 5 | View report | SARIF |
npx workflow.[!WARNING]
Shannon actively executes exploits. Run it only against applications and environments you own or have explicit written authorization to test. Do not run Shannon against production systems.
# Configure credentials with the interactive wizard.
npx @keygraph/shannon@latest setup
Run a pentest against a source-available target.
npx @keygraph/shannon@latest start \
  -u https://your-app.com \
  -r /path/to/your/repo
Shannon pulls the worker image from Docker Hub, starts the required local infrastructure, mounts the target repository read-only inside an ephemeral worker container, and writes results to a local workspace.
For source builds, authenticated scans, provider-specific setup, and platform notes, see Documentation.
[!TIP]
Prefer to use a subscription instead of API credits?
> - OpenAI Codex: The latest version of Shannon supports ChatGPT Plus and Pro subscriptions. Follow the OpenAI Codex subscription setup guide to get started.
- xAI (Grok): The latest version of Shannon supports xAI subscriptions. Follow the xAI subscription setup guide to get started.
- Claude Code: The latest version of Shannon does not support Claude Code subscriptions. Follow the Claude Code subscription setup guide to use version 1.9.0, which is the final release built on the Claude Agent SDK.
Shannon can run continuously against deployed staging and development environments through official integrations for GitHub Actions and GitLab CI/CD.
Both integrations:
status: exploited.
name: Shannon Pentest
on:
workflow_dispatch:
permissions:
security-events: write
jobs:
pentest:
runs-on: ubuntu-latest
steps:
- uses: actions/checkout@v4
- name: Run Shannon
uses: KeygraphHQ/shannon-action@v1
with:
url: https://staging.example.com
api-key: ${{ secrets.SHANNON_AI_API_KEY }}
fail-on-severity: high
upload-sarif: true
The Action defaults repo to the checked-out GitHub workspace. It uploads one artifact containing the security assessment reports and SARIF, plus a separate run artifact containing scan and agent logs. Enabling upload-sarif publishes supported findings to GitHub code scanning.
Requirements:
| Edition | What it is | Price | | --- | --- | --- | | Shannon (open source) | This repository. A complete autonomous pentester you run yourself, locally or in CI/CD, against an application whose source code you have. Well suited to individual developers and small teams. | Open source under AGPL-3.0. You pay only your own model costs. | | Community Program | Keygraph Pro at no cost, for U.S.-based 501(c)(3) nonprofits and for seed or pre-Series-A startups with 20 or fewer active developers. | $0 in cloud service fees while you qualify. | | Pro | Keygraph's cloud-hosted edition, managed by Keygraph, with every module included. | $50 per active developer per month. | | Enterprise | Everything in Pro, self-hosted in your own environment or fully air-gapped. | Custom. |
See keygraph.io/pricing for current prices and the full feature table.
Pro, Enterprise, and the Community Program are powered by an enhanced, enterprise-grade version of the Shannon engine, and all three add:
Compare Shannon, Pro, and Enterprise in detail →
Shannon combines multi-stage security code analysis with live reconnaissance and exploitation:
flowchart TD
    S["Source code"] --> EXISTING["Recon + vulnerability analysis"]
    S --> SAST["Agentic security code analysis"]
EXISTING -- "Pentest candidates" --> REC["Finding reconciliation
(merge + deduplicate)"]
    SAST -- "SAST candidates" --> REC
REC -- "Reconciled exploitation queue" --> EXP["Exploitation agents"]
    APP["Running application"] --> EXP
EXP -- "Exploit demonstrated" --> REPORT["Reporting
PDF · Markdown · SARIF"]
    EXP -- "No exploit demonstrated" --> DROP["Discard"]
REPORT --> CICD["CI/CD gate"]
Stage by stage:
1. Recon and vulnerability analysis explores the running application, ties runtime behavior back to the source, and runs specialized agents across Injection, XSS, SSRF, Authentication, and Authorization. 2. Agentic security code analysis maps the application's architecture, trust boundaries, exposed interfaces, dependencies, data flows, and high-risk assets, then opens targeted investigations against them. 3. Finding reconciliation merges both streams of candidates, deduplicates the overlap, and groups what remains into an exploitation queue. 4. Exploitation agents attempt real proof-of-concept attacks against the running application. 5. Validation throws out every candidate Shannon can't demonstrate. 6. Reporting produces PDF and Markdown reports with the evidence attached, plus structured JSON and SARIF for downstream systems.
Only live-validated vulnerabilities become Shannon pentest findings or count toward CI/CD severity gates.
Each scan runs in an ephemeral Docker container with an isolated workspace and per-invocation orchestration.
Use these guides for operational detail:
| Guide | Use it for | | --------------------------------------------------------- | ------------------------------------------------------------------------------------------------------------------------------------------------------------------------- | | Source build and CLI commands | Cloning, building, common commands, output paths, and local development. | | Configuration | Authenticated testing, login flows, rules of engagement, and report filters. | | AI providers | Selecting the model, the supported providers (Anthropic, OpenAI, xAI, AWS Bedrock, and any other Pi-supported provider), and custom LLM gateways. | | Platforms and networking | Windows/WSL2, Linux, macOS, Docker networking, local apps, and custom hostnames. | | Workspaces and resuming | Naming workspaces, resuming interrupted scans, and workspace storage. | | Safety and limitations | Authorized-use requirements, non-production guidance, mutative effects, cost, and model caveats. | | Coverage and roadmap | Current vulnerability coverage and planned work. | | Pro and Enterprise | Shannon compared with Pro, Enterprise, and the Community Program: black-box pentesting, SCA and secrets, findings management, fix pull requests, retests, Jira, and deployment. |
Shannon is not a passive scanner. Its exploitation agents can create users, submit forms, mutate application state, trigger outbound requests, and otherwise affect the target system. Use sandboxed, staging, or local development environments with disposable data.
You are responsible for using Shannon legally and ethically. Do not point Shannon at systems, repositories, or applications you do not own or do not have explicit authorization to test.
Important limitations:
Shannon is licensed under the GNU Affero General Public License v3.0.
Commercial and enterprise licensing is available for organizations that need different license terms, commercial support, private redistribution, managed-service use, or broader deployment options, including Keygraph Pro and Enterprise.
For commercial licensing, contact [email protected].
Thanks to Pi, Playwright CLI, and Mantis.
See THIRD_PARTY_NOTICES.md for licensing and attribution details.
Keygraph is the company behind Shannon. It also builds Keygraph Pro and Keygraph Enterprise, the commercial editions that close the full AppSec lifecycle and run an enhanced build of Shannon as their pentesting engine.
Community office hours are available for hands-on help with bugs, deployments, and configuration questions.
At this time, Keygraph is not accepting external code contributions. Issues are welcome for bug reports and feature requests:
Stay connected:Yes. Shannon runs inside your infrastructure in an ephemeral worker container. It mounts the repository read-only and writes results to a local workspace.
Keygraph never receives your source code and never proxies your model traffic. Your model requests go straight to the provider or endpoint you configure, and they carry source and application context with them. Poin
→ →
 →
 →
 →
 →
 →
 →